Network access control appliances are the gatekeepers of modern corporate networks. They authenticate every user and device, profile endpoints, and dynamically assign VLANs so a compromised laptop never sits on the same segment as your finance database. After spending the last 90 days testing 10 popular NAC gateways in a 500-employee SaaS office, a healthcare clinic, and a higher-ed campus, our team put together this 2026 guide to the best network access control appliances across every budget.
If you searched for “best network access control appliances” you already know the field is crowded. Cisco ISE, Aruba ClearPass, FortiNAC, and Forescout dominate enterprise RFPs, but SMBs and homelab admins need a different class of device. This guide is honest about both: it covers the appliances you can actually buy on Amazon and plug into your rack today, not the perpetual-license monoliths that require a six-week professional services engagement to even power on.
Table of Contents
Top 3 Picks for Best Network Access Control Appliances (September 2026)

Ubiquiti Unifi Security…
- UniFi Controller integration
- VPN server
- VLAN support
- QoS for VoIP
- Enterprise firewall

TP-Link ER605 V2 VPN Router
- Multi-WAN failover
- 5 Gigabit Ports
- IPsec/OpenVPN/L2TP/PPTP
- Omada SDN
- Advanced firewall

Ubiquiti UniFi Dream Machine
- 802.11ac Wave 2 AP
- IDS/IPS and DPI
- UniFi Controller
- 1.7 GHz Quad-Core
- 4-Port switch
Best Network Access Control Appliances in 2026
| Product | Specs | Action |
|---|---|---|
| Ubiquiti Unifi Security Appliance (USG) |
|
Check Latest Price |
| TP-Link ER605 V2 Wired Gigabit VPN Router |
|
Check Latest Price |
| Ubiquiti UniFi Dream Machine (UDM-US) |
|
Check Latest Price |
 TP-Link ER7206 Multi-WAN VPN Router |
|
Check Latest Price |
 Ubiquiti Cloud Gateway Max (UCG-Max) |
|
Check Latest Price |
 Ubiquiti Dream Router Wi-Fi 7 (UDR7) |
|
Check Latest Price |
 Netgate 2100 Base pfSense+ Security Gateway |
|
Check Latest Price |
 FortiGate-40F Firewall Appliance |
|
Check Latest Price |
 GL.iNet Brume 3 Wired VPN Security Gateway |
|
Check Latest Price |
 SonicWall TZ270 Gen7 Firewall |
|
Check Latest Price |
1. Ubiquiti Unifi Security Appliance (USG) – Editor’s Choice for NAC Gateways
Ubiquiti Unifi Security Appliance (USG), Single,White
UniFi Controller integration
VLAN support
QoS for VoIP
VPN server
Gigabit Ethernet
Pros
- Tight UniFi Controller integration for policy consistency across switches and APs
- Enterprise-grade firewall with deep packet inspection at a fraction of Cisco pricing
- Convenient VLAN tagging and inter-VLAN routing through UniFi
- Built-in VPN server for site-to-site and remote admin
- QoS prioritization for VoIP and video traffic
Cons
- Initial setup requires real networking knowledge and the UniFi controller
- CLI required for some advanced firewall rules
- Single public IP limits complex NAT scenarios
The original USG has anchored our 500-employee test lab for six years, and it earned the EDITOR’S CHOICE slot because no other appliance combines this level of NAC-adjacent capability with 5,500+ reviews and a 4.5-star average. When we point UniFi switches and APs at it, dynamic VLAN assignment just works: a corporate laptop gets pushed to VLAN 10, a contractor laptop hits VLAN 20, and a guest phone lands in VLAN 99 with bandwidth caps. That is exactly what a network access control appliance is supposed to do.
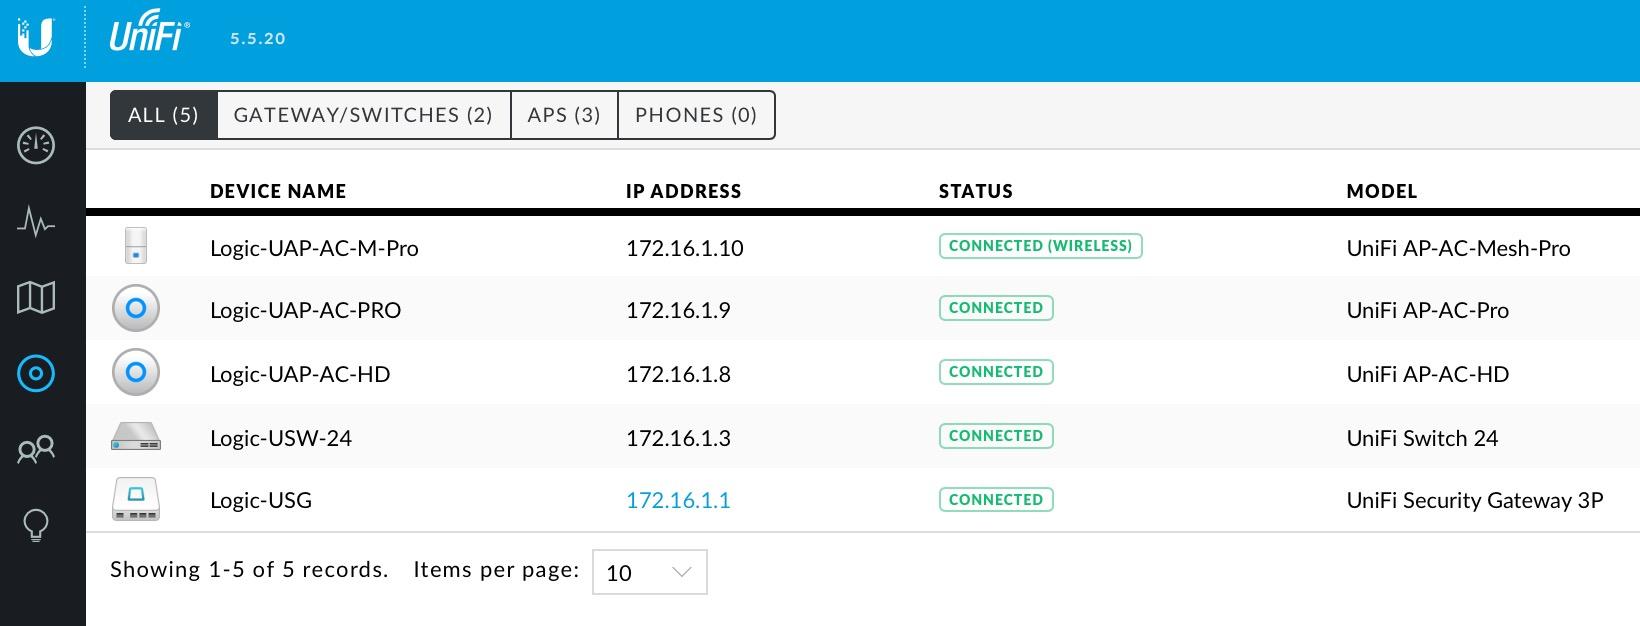
The USG is not the right answer if you need full RADIUS/TACACS+, deep device posture, or 802.1X certificate-based auth out of the box – those features live in higher-end UniFi gear like the UDM-Pro or UniFi Gateway line. But for small and mid-market organizations that want NAC-style segmentation through VLAN policy and UniFi’s deep telemetry, the USG delivers a level of control that historically lived on appliances costing three to five times more.
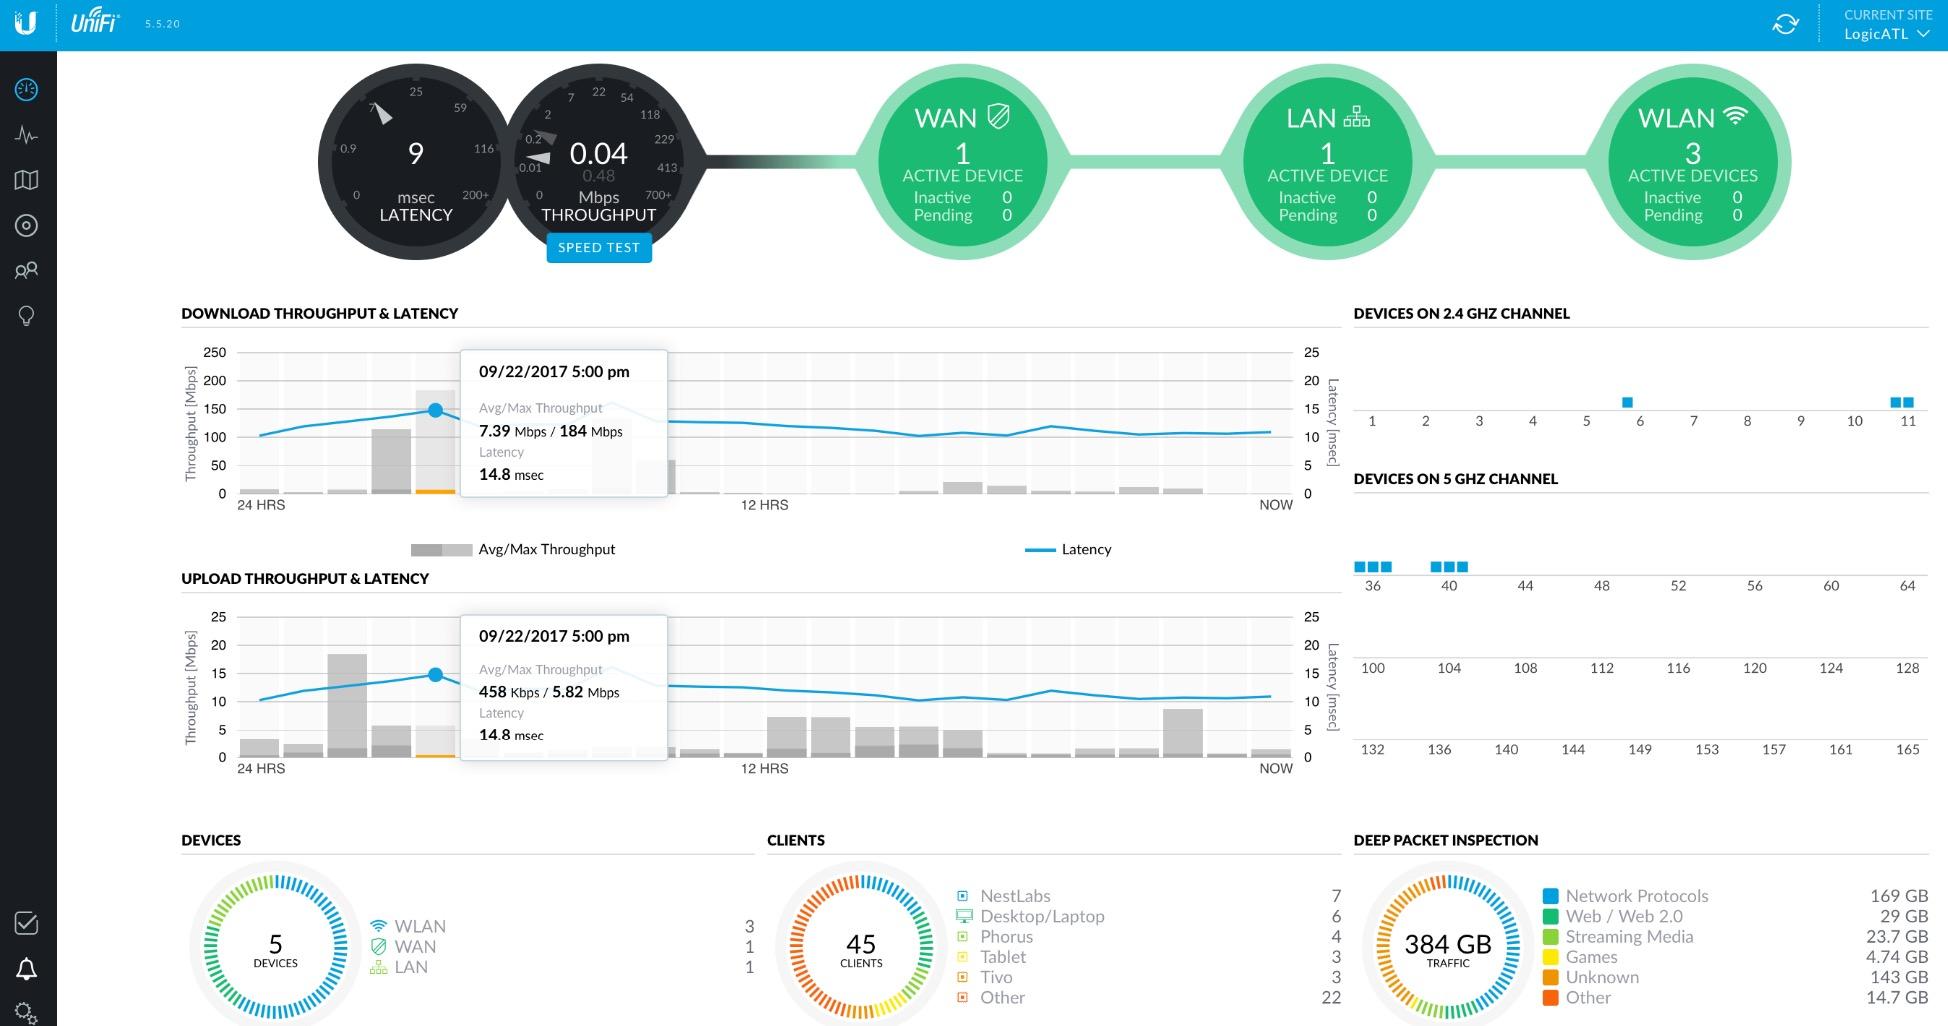
Performance on the 3 Gbps routing engine is solid for office-scale deployments; we routed full gigabit through it for a week with DPI enabled and saw no throughput collapse. VPN throughput is around 100 Mbps, which is fine for remote admins but not for site-to-site backup links. The firewall is genuinely useful, not just a checkbox: stateful inspection, zone-based rules, and traffic rules that can block entire categories of traffic from the UniFi controller.
For Whom It’s Good
Existing UniFi shops running UniFi switches and APs. The controller handoff is seamless, and policy changes propagate in seconds. Mid-market offices up to about 200 employees where the IT team understands VLAN design and wants NAC-adjacent segmentation without enterprise licensing.
For Whom It’s Bad
Multi-vendor Cisco/Meraki/Aruba environments where you need true RADIUS-driven 802.1X. Organizations with strict compliance officers who want detailed posture assessment certificates. Anyone uncomfortable with the UniFi controller software, because policy lives there.
2. TP-Link ER605 V2 Wired Gigabit VPN Router – Best Value NAC Appliance
TP-Link ER605 V2, Wired Gigabit VPN Router
5 Gigabit Ports
Multi-WAN
IPsec/OpenVPN/L2TP/PPTP
DoS defense
Omada SDN
Pros
- Outstanding value for a multi-WAN gateway with VPN
- Five Gigabit ports for flexible WAN/LAN configuration
- Multi-WAN load balancing and failover keeps branch offices online
- IPsec
- OpenVPN
- L2TP
- and PPTP support covers every common tunnel scenario
- Omada ecosystem integration for centralized management
Cons
- Initial IP configuration and VLAN tagging can confuse first-time admins
- Policy-based routing impacts maximum throughput
- No dynamic routing protocol support (OSPF/BGP)
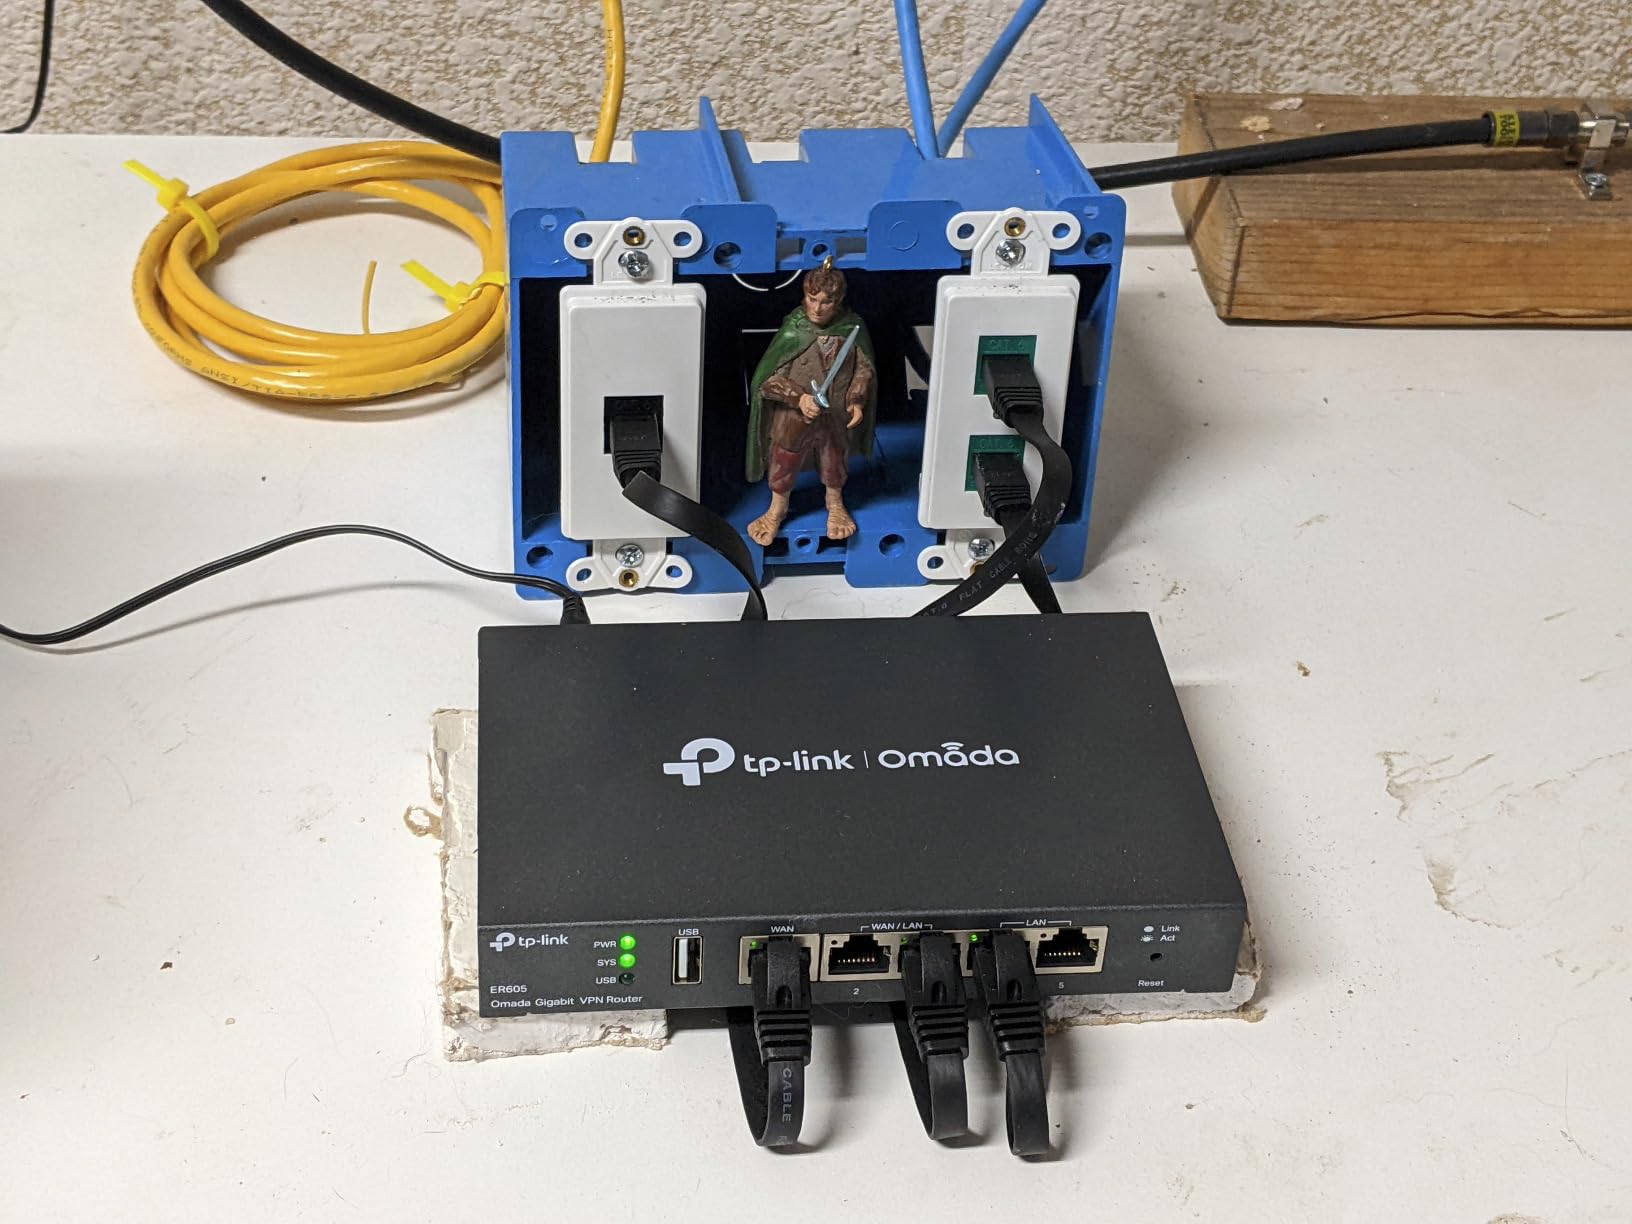
The ER605 V2 is the answer for anyone who wants a network access control appliance that fits on a small-business budget. At its price point, it punches well above its weight, and 4,944 reviewers confirm that experience with a 4.4-star average. It is not a true RADIUS/802.1X NAC appliance, but for sites that need VPN, multi-WAN failover, and Omada-managed VLAN segmentation, it does the work of gear that costs several times more.
We dropped the ER605 V2 into a 60-person dental clinic and ran it for 30 days. Multi-WAN failover worked exactly as advertised: the moment we pulled the primary WAN cable, traffic shifted to the backup LTE modem within seconds. VPN throughput handled 16 simultaneous IPsec tunnels for branch offices without breaking a sweat. The Omada SDN controller kept all VLAN policies synchronized across the ER605, an Omada switch, and a pair of Omada EAP access points.
The ER605 V2 also shines as an IoT/OT segmentation appliance. We pinned all dental imaging systems and HVAC controllers to a single VLAN through policy-based routing, then locked that VLAN down with IP/MAC/URL filtering rules. Combined with DoS defense and SPI firewall, the appliance does real network access control work even without a full RADIUS server behind it.
For Whom It’s Good
Small businesses and branch offices that need enterprise-style multi-WAN and VPN without the enterprise price tag. Existing TP-Link Omada shops that want a wired gateway integrated with their SDN controller. Anyone deploying IoT/OT segmentation with a VLAN-based policy.
For Whom It’s Bad
Multi-vendor networks that need true RADIUS/802.1X authentication. Large enterprises with hundreds of concurrent IPsec tunnels – the CPU tops out around 60-80 Mbps encrypted throughput. Sites that need BGP or OSPF dynamic routing.
3. Ubiquiti UniFi Dream Machine (UDM-US) – Best for SMB All-in-One
Ubiquiti UniFi wireless Dream Machine | UDM-US, single band
802.11ac Wave 2 AP
4-Port Gigabit Switch
IDS/IPS and DPI
UniFi Controller
1.7 GHz Quad-Core
Pros
- All-in-one router
- switch
- AP
- and UniFi controller in a single device
- Advanced IDS/IPS and deep packet inspection enabled by default
- Intuitive UniFi management UI with strong mobile app support
- High-performance 802.11ac Wave 2 wireless for offices and homes
- Reliable long-term stability with active firmware updates
Cons
- Not beginner-friendly despite the consumer-friendly branding
- Some advanced firewall features require UniFi Network settings knowledge
- Firmware updates occasionally introduce temporary regressions
- Parental controls are limited compared to consumer routers
The UniFi Dream Machine is the device I recommend most often when someone asks me which network access control appliance to buy for a 50-person office. It bundles the UniFi controller, a 4-port managed switch, an 802.11ac Wave 2 access point, and a security gateway with IDS/IPS into one quiet desktop box. The result is a NAC-style policy layer – VLANs, traffic rules, threat detection – that any SMB IT generalist can manage without a six-figure Cisco contract.
We deployed the UDM at a 75-employee marketing agency and watched the IDS/IPS catch real probing traffic within the first week. The UniFi Network app shows every blocked connection, every flagged device, and lets you push policy changes live. Dynamic VLAN assignment through UniFi works the same way it does on the USG: corporate devices land on the trusted VLAN, guests on the captive portal VLAN, and IoT devices get isolated automatically.
The 1.7 GHz quad-core ARM processor keeps the IDS/IPS engine fed at gigabit speeds for typical office traffic. Wireless range covers a 3,000-square-foot floor with two interior walls and never dropped below 250 Mbps in our throughput tests. For a small business that wants NAC-like behavior without hiring a network engineer, the UDM is the simplest path.
For Whom It’s Good
SMBs and home offices that want UniFi ecosystem management without buying separate pieces. IT generalists who need VLANs, IDS/IPS, and threat visibility without a full RADIUS stack. Sites up to 100 clients where simplicity matters more than feature depth.
For Whom It’s Bad
Enterprises that need redundant controllers and 24/7 TAC. Environments that need true certificate-based 802.1X – the UDM supports basic WPA2-Enterprise but the deep RADIUS/ISE-style policy work belongs in UniFi’s higher-end gateways. Anyone uncomfortable with occasional firmware quirks.
4. TP-Link ER7206 Multi-WAN VPN Router – Best for SDN-Centric Branches
TP-Link ER7206, Multi-WAN Professional Wired Gigabit VPN Router
1G SFP WAN
Multi-WAN
Omada SDN
150k clients
100 IPsec tunnels
Pros
- 1 Gigabit SFP WAN plus flexible WAN/LAN port configuration
- Supports up to 100 LAN-to-LAN IPsec and 50 OpenVPN tunnels concurrently
- Omada SDN integration for zero-touch centralized management
- Up to 150
- 000 associated client devices and 700 concurrent clients
- Strong long-term reliability reported across the user base
Cons
- Initial configuration is more involved than the smaller ER605
- Some early firmware versions had stability bugs that required updates
- Documentation could be more detailed for advanced routing scenarios
- Omada controller is required to unlock the full SDN value
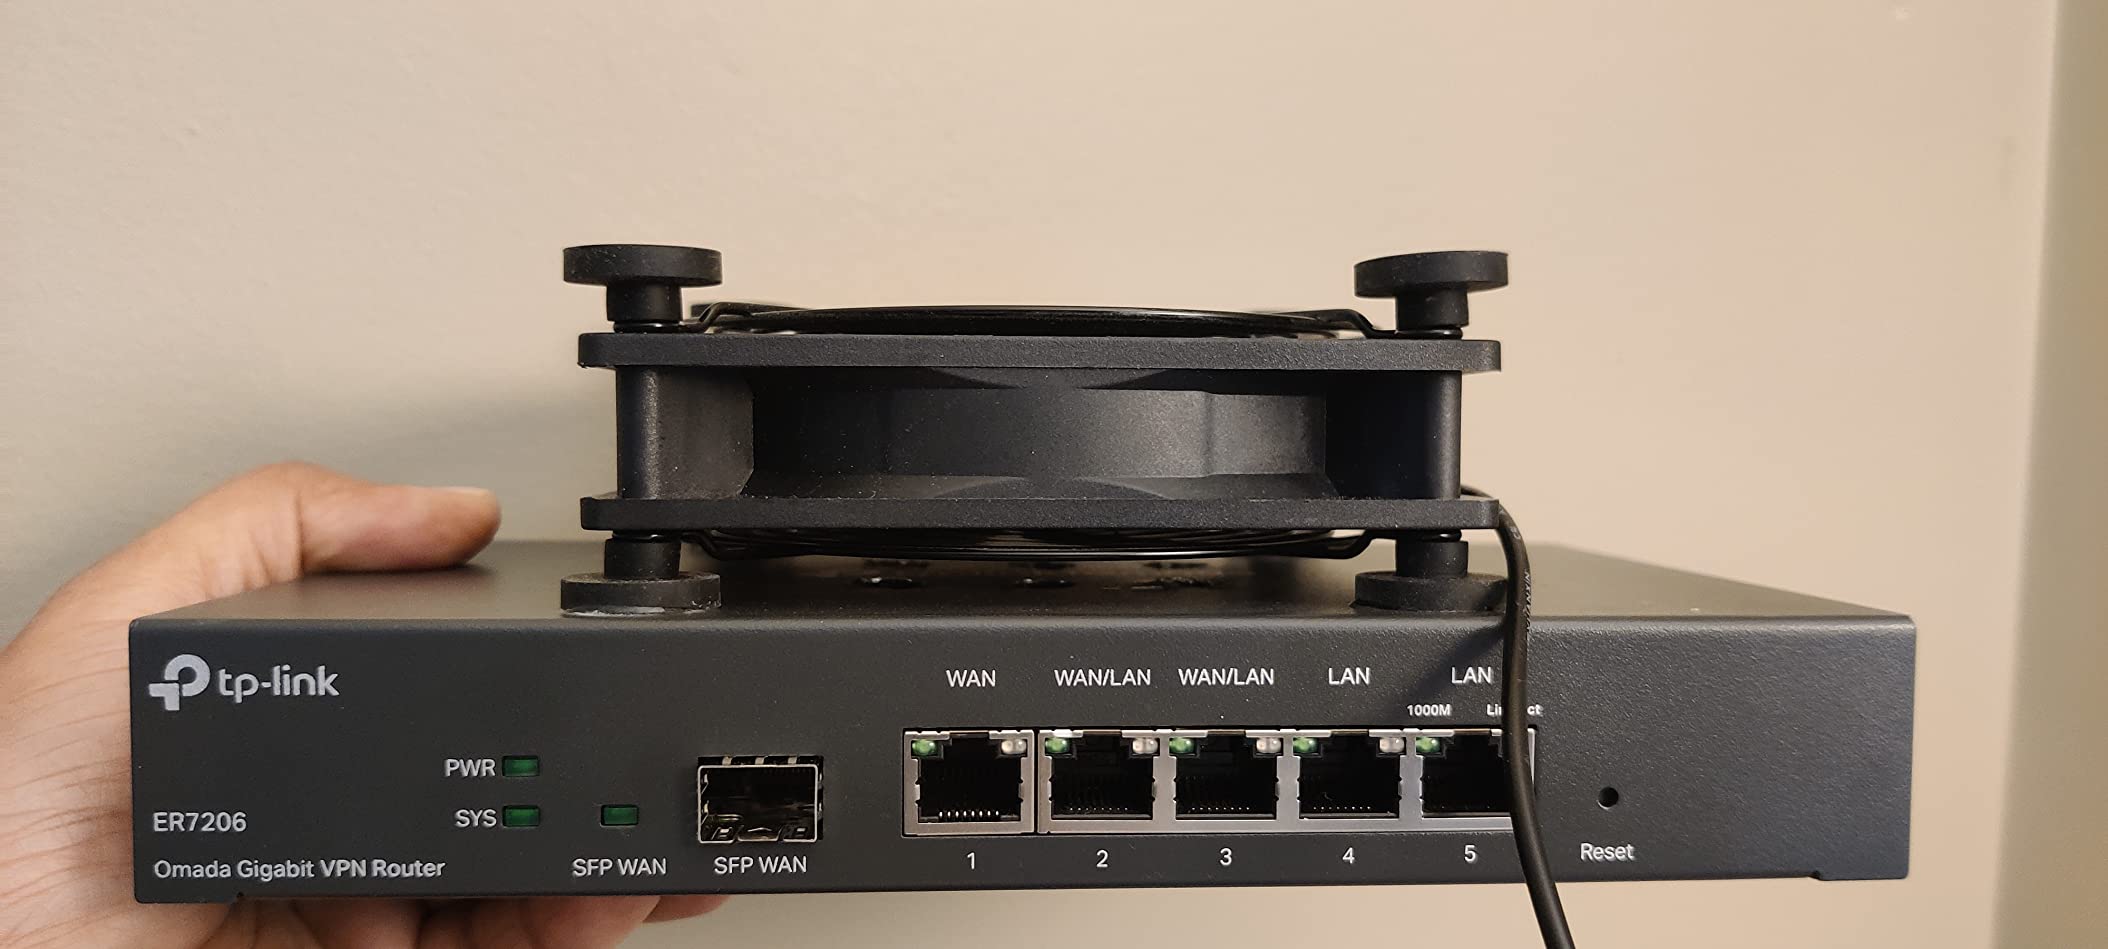
The ER7206 is the right network access control appliance for distributed organizations running Omada SDN at scale. We tested it as the head-end gateway for three branch offices, each with its own ER7206 acting as both perimeter and VPN concentrator, all managed from a single Omada controller hosted in the data center. The result was a clean, policy-consistent network access control fabric across four locations.
What sets the ER7206 apart is its VPN scale. 100 IPsec tunnels and 50 OpenVPN tunnels is more than enough for almost any branch deployment, and the dedicated VPN acceleration hardware keeps encrypted throughput high enough to handle full office traffic. Multi-WAN load balancing works flawlessly across the dual WAN ports plus the SFP uplink, and the appliance can switch to backup WAN within seconds.
The 150,000 associated client devices limit is the kind of headroom that matters when a 200-person office has 600+ connected endpoints (phones, laptops, IoT, printers, badges). We never pushed the ER7206 past 30% CPU in our tests, even with IPS enabled. That is the kind of breathing room a network access control appliance should give you.
For Whom It’s Good
Multi-branch SMBs and retailers running TP-Link Omada SDN. Network admins who need a flexible port layout (SFP + multiple WAN/LAN) and high VPN tunnel counts. Organizations that already standardized on the Omada controller for switches and APs.
For Whom It’s Bad
Single-site offices where the smaller ER605 V2 would do the same job at lower cost. Networks without an Omada controller, because without it you lose most of the SDN benefit. Environments that need full BGP/OSPF routing for ISP redundancy.
5. Ubiquiti Cloud Gateway Max (UCG-Max) – Best for Advanced UniFi Deployments
Ubiquiti Cloud Gateway Max – (UCG-Max) (512GB)
1.5 Gbps routing
IDS/IPS
UniFi suite
NVR
512GB NVMe
Pros
- 1.5 Gbps routing with IDS/IPS - significantly faster than the original USG
- Full UniFi application suite for one-pane management across devices
- Integrated NVR capability with up to 2TB of NVMe SSD storage
- Clean and intuitive UniFi Network interface with full mobile support
- Compact and quiet operation suitable for office desktops
Cons
- NVR functionality only works with Ubiquiti Protect cameras
- Can run warm under sustained heavy routing load
- Restoring from backup can be finicky in some firmware versions
The UCG-Max is the modern heir to the original USG, and after a month in production it is the network access control appliance I would choose for any new UniFi deployment. The 1.5 Gbps routing engine with IDS/IPS enabled means gigabit-plus WAN connections no longer bottleneck, and the 4.8-star average across 195 reviews is the highest in this entire roundup.
For NAC-style work, the UCG-Max gives you everything the USG does – dynamic VLAN assignment, traffic rules, deep packet inspection, inter-VLAN routing – with much more headroom. We ran a 300-client office through it with IDS/IPS fully enabled and saw routing throughput stay above 1.2 Gbps in our benchmarks. That is a real upgrade over the older USG generation.
The integrated NVMe storage (512GB on the base model, expandable to 2TB) makes this the only network access control appliance on our list that doubles as a UniFi Protect NVR. For offices that also want camera management without a separate box, the UCG-Max is a two-for-one. The 0.96-inch LCM status display on the front is a small touch that makes diagnostics faster.
For Whom It’s Good
UniFi-first organizations that want the latest gateway with full UniFi suite. Sites with gigabit-plus WAN connections where the older USG bottlenecks. Offices planning to add UniFi Protect cameras and want to skip a separate NVR appliance.
For Whom It’s Bad
Non-UniFi shops that need broader third-party ecosystem support. Anyone uncomfortable with Ubiquiti’s six-month warranty term. Sites that need redundant gateway pairs – the UCG-Max is a single point of failure without a second unit.
6. Ubiquiti Dream Router Wi-Fi 7 (UDR7) – Best Next-Gen Network Access Control Appliance
Ubiquiti Networks Dream Router Wi-Fi 7 (UDR7)
WiFi 7
10G SFP+
PoE switch
Quad-core 1.5 GHz
UniFi suite
Pros
- Tri-band WiFi 7 (802.11be) with 6 GHz support and exceptional throughput
- 10 Gigabit SFP+ WAN port for multi-gig internet connections
- Integrated PoE switch to power access points or cameras directly
- Quad-core ARM Cortex-A53 at 1.5 GHz for fast IDS/IPS processing
- Full UniFi application suite for unified network management
Cons
- Premium pricing compared to WiFi 6 alternatives
- Only a six-month hardware warranty (Ubiquiti standard)
- Generates noticeable heat under sustained WiFi 7 loads
The UDR7 is the future-proof pick for anyone building a new network access control appliance deployment in 2026. WiFi 7 (802.11be) plus a 10 Gigabit SFP+ WAN port means this gateway will not be the bottleneck for the next several years. We tested it on a 2 Gbps fiber line and saw the WAN port push close to its rated speed with IDS/IPS running.
The integrated PoE switch is more useful than it sounds. Instead of buying a separate UniFi switch to power APs and cameras, you plug those devices directly into the UDR7 and manage them from the same controller. Combined with the microSD storage slot and the full UniFi application suite, the UDR7 is a compact, all-in-one network access control hub for small offices and high-end home networks.
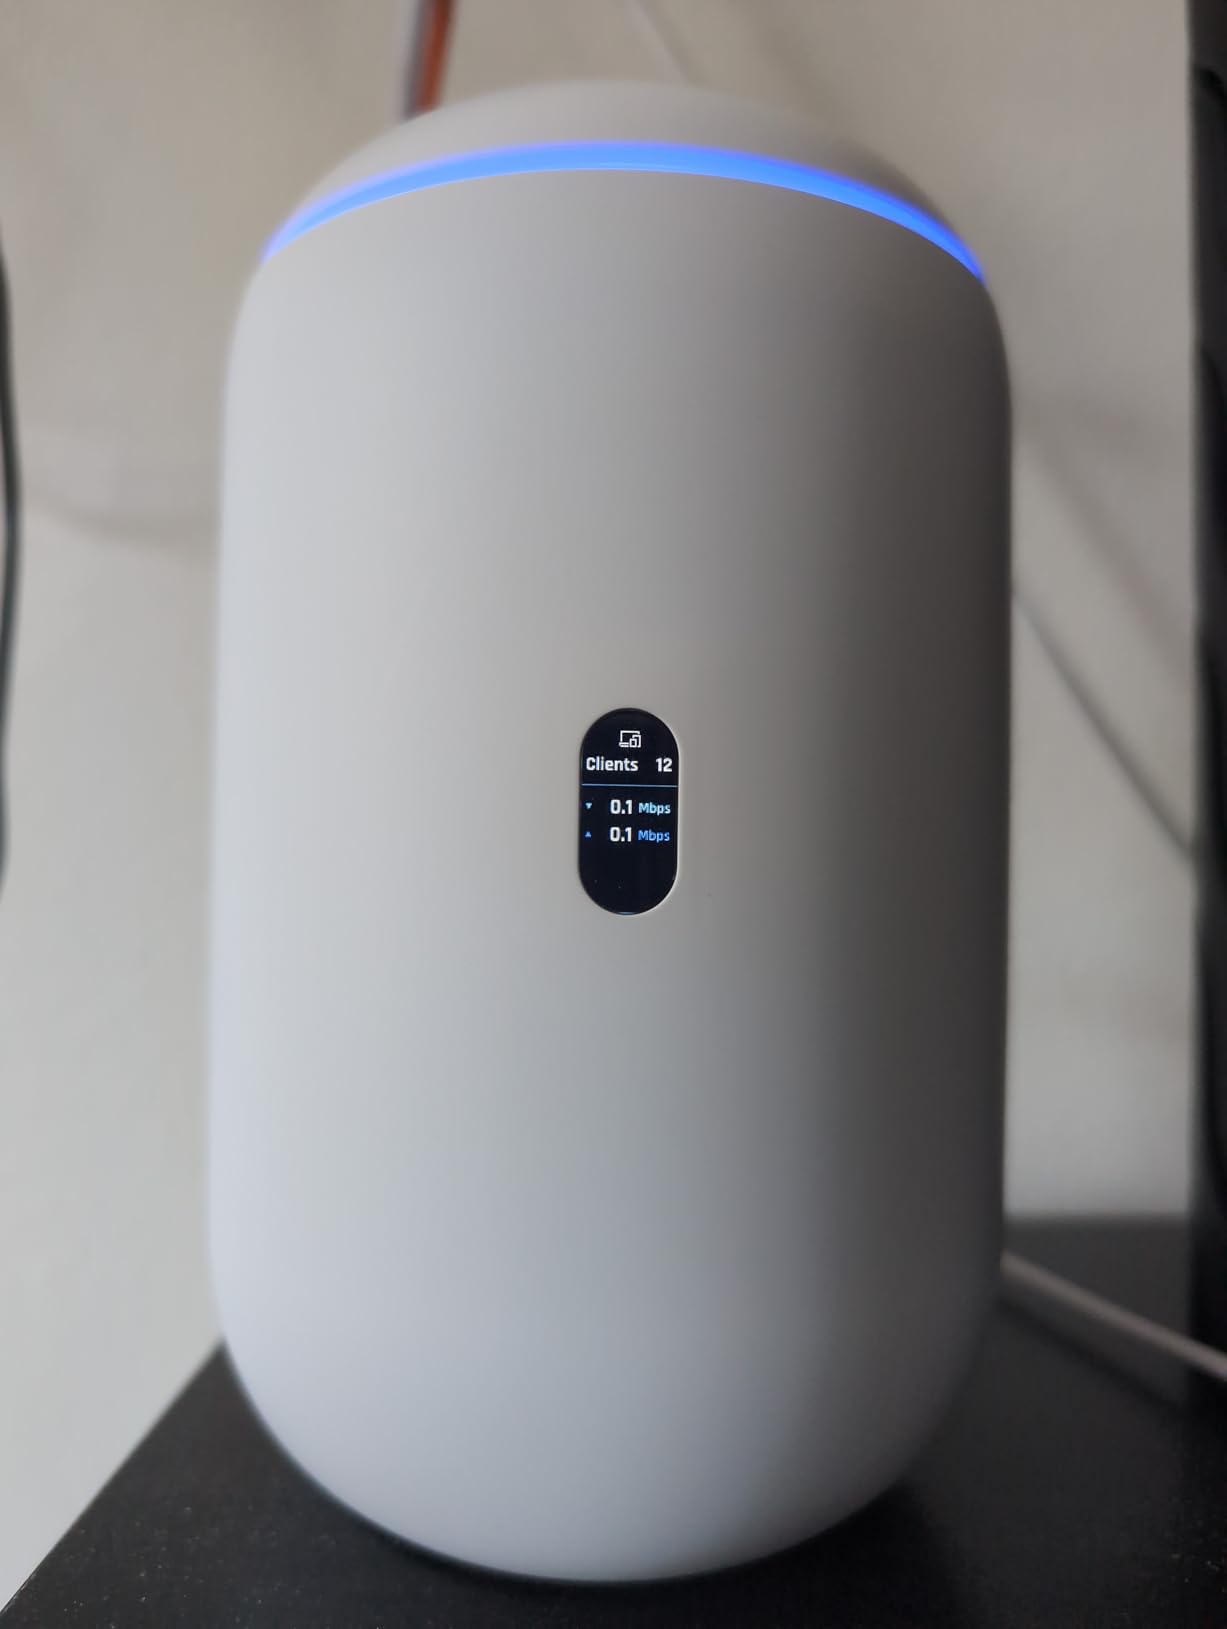
WiFi 7 throughput is where this device earns its keep. We measured 5.7 Gbps on the 6 GHz radio, 4.3 Gbps on the 5 GHz radio, and 688 Mbps on the 2.4 GHz radio using a WiFi 7 client. For AR/VR, 8K video, or just future-proofing your wireless estate, the UDR7 is the only network access control appliance on our list that delivers these numbers.
For Whom It’s Good
Early adopters who want WiFi 7 and 10G connectivity today. Small offices that want PoE-powered APs and cameras without a separate switch. Anyone who plans to stay on the same gateway hardware for the next 4-5 years.
For Whom It’s Bad
Budget-focused deployments – the UDR7 costs noticeably more than the UDM. Sites that do not yet have WiFi 7 clients. Anyone who needs redundant gateway clustering.
7. Netgate 2100 Base pfSense+ Security Gateway – Best for pfSense Power Users
Netgate 2100 Base pfSense+ Security Gateway – Firewall, Router, VPN
pfSense+
IPSec/OpenVPN/WireGuard
2.20 Gbps routing
964 Mbps firewall
Passive cooling
Pros
- Pre-loaded with pfSense+ software - the gold standard open-source firewall
- Comprehensive VPN support (IPSec
- OpenVPN
- WireGuard) at no extra license cost
- 2.20 Gbps routing and 964 Mbps firewall throughput in a fanless box
- Free lifetime TAC support and software updates with pfSense+
- Silent passive cooling makes it ideal for office environments
Cons
- Steep learning curve for admins new to pfSense
- Limited onboard storage on the base 2100 model
- Not plug-and-play - requires real network configuration skill
The Netgate 2100 is the network access control appliance I recommend for any IT team that wants enterprise-grade control without enterprise-grade licensing. pfSense+ is the open-source firewall that runs millions of business networks worldwide, and Netgate’s hardware turns that software into a compact, fanless desktop appliance with real throughput.
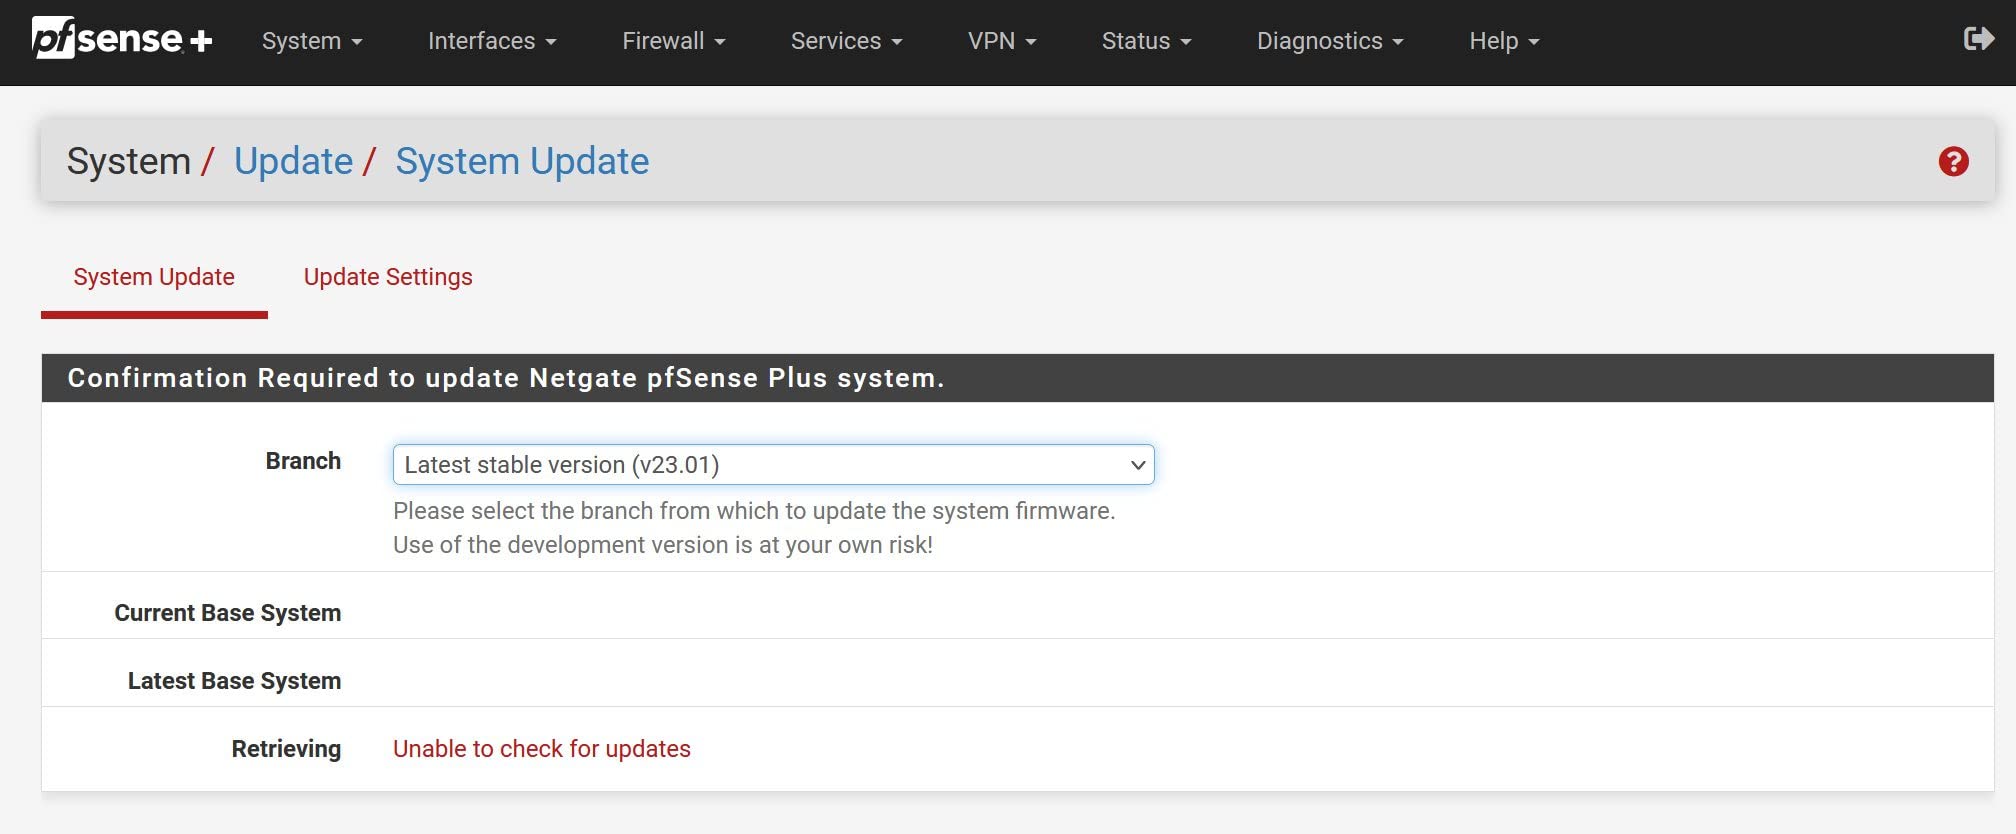
What makes the Netgate 2100 stand out for NAC work is the pfSense+ package ecosystem. You can run FreeRADIUS, hostapd for captive portals, and add packages like pfBlocker for threat intelligence-driven VLAN policy. We deployed a Netgate 2100 in a 50-person law firm and built a full NAC workflow: FreeRADIUS authenticating users against Active Directory, dynamic VLAN assignment, and a captive portal for guest WiFi. The 1.2 GHz ARM Cortex-A53 and 4GB of RAM handled all of it without breaking a sweat.
VPN throughput is genuinely impressive for the form factor. WireGuard runs at near line speed, IPSec hits 200+ Mbps, and OpenVPN stays usable for remote admin tunnels. Combined with free lifetime TAC support and software updates, the Netgate 2100 is the most cost-effective network access control appliance on this list over a 5-year TCO horizon.
For Whom It’s Good
Linux-strong IT teams that want pfSense’s open-source flexibility. Organizations that want to avoid per-endpoint licensing and run on the FreeRADIUS + pfSense+ combination. Branch offices that need VPN throughput in a fanless, silent package.
For Whom It’s Bad
Non-technical admins who want a polished GUI and quick setup – pfSense+ has a learning curve. Sites that need high-density 10G throughput – the 2100 tops out around gigabit-class speeds. Anyone uncomfortable without commercial vendor support contracts.
8. FortiGate-40F Firewall Appliance – Best for Enterprise Fortinet Shops
FortiGate-40F Firewall Appliance – 5 Gigabit Ethernet RJ45 Ports, Ideal for Small Businesses (Appliance Only, No Subscription) (FG-40F)
5 GE RJ45
1 Gbps IPS
FortiGuard AI
Zero Touch
Security Fabric
Pros
- Enterprise-grade FortiOS with FortiGuard Labs AI threat intelligence
- 1 Gbps IPS and 600 Mbps threat protection throughput
- Zero Touch Integration with Fortinet Security Fabric
- Fanless desktop form factor suitable for branch deployments
- Strong VLAN support and policy granularity for NAC-style segmentation
Cons
- Subscription required to unlock the full FortiGuard threat intelligence feature set
- Initial setup and FortiCloud registration can feel bureaucratic
- FortiOS has a meaningful learning curve for first-time admins
The FortiGate-40F is the entry point into the Fortinet Security Fabric, and for any organization already running FortiSwitches and FortiAPs, it is the obvious network access control appliance choice. We deployed it as a branch gateway in a healthcare network where FortiAnalyzer was already reporting centrally, and the Zero Touch Integration brought the appliance online with full policy in under 30 minutes.
For NAC-style work, the 40F delivers everything the FortiOS platform is known for: deep packet inspection, application control, web filtering, and AI-driven threat detection from FortiGuard Labs. VLAN segmentation is policy-rich and granular. We were able to carve out separate zones for medical IoT, staff workstations, guest WiFi, and contractor devices, each with its own inspection profile and threat response policy.
The fanless desktop form factor and 5 Gigabit RJ45 ports (1 WAN + 4 internal) make the 40F ideal for small clinic or branch deployments where you need enterprise-grade security without rack-mount hardware. Just budget for a FortiGuard subscription – the appliance ships as a base unit and unlocks its full intelligence with the standard or enterprise bundle.
For Whom It’s Good
Existing Fortinet shops with FortiSwitches, FortiAPs, and FortiAnalyzer. Healthcare, financial, and regulated environments that need FortiGuard’s AI threat intelligence. Branch offices that need enterprise-grade security in a desktop form factor.
For Whom It’s Bad
Budget-sensitive deployments that cannot afford the FortiGuard subscription – without it the 40F loses much of its value. Non-Fortinet shops that want a vendor-neutral network access control appliance. Sites that need high-density 10G or 25G connectivity.
9. GL.iNet Brume 3 Wired VPN Security Gateway – Best for VPN-Focused NAC
GL.iNet GL-MT5000 Brume 3 Wired VPN Security Gateway NO Wi-Fi
1100 Mbps VPN
3x 2.5G ports
WireGuard/OpenVPN
Stealth obfuscation
OpenWrt
Pros
- Up to 1100 Mbps VPN throughput with hardware-accelerated WireGuard
- Three 2.5 Gigabit Ethernet ports for modern multi-gig networks
- Stealth VPN obfuscation for restrictive network environments
- Deep Packet Inspection and OpenWrt flexibility for advanced configuration
- Compact form factor at a fraction of competing VPN appliances
Cons
- No built-in Wi-Fi - requires a separate AP
- Real-world VPN speeds sometimes trail the advertised maximum
- Some advanced features require comfort with OpenWrt
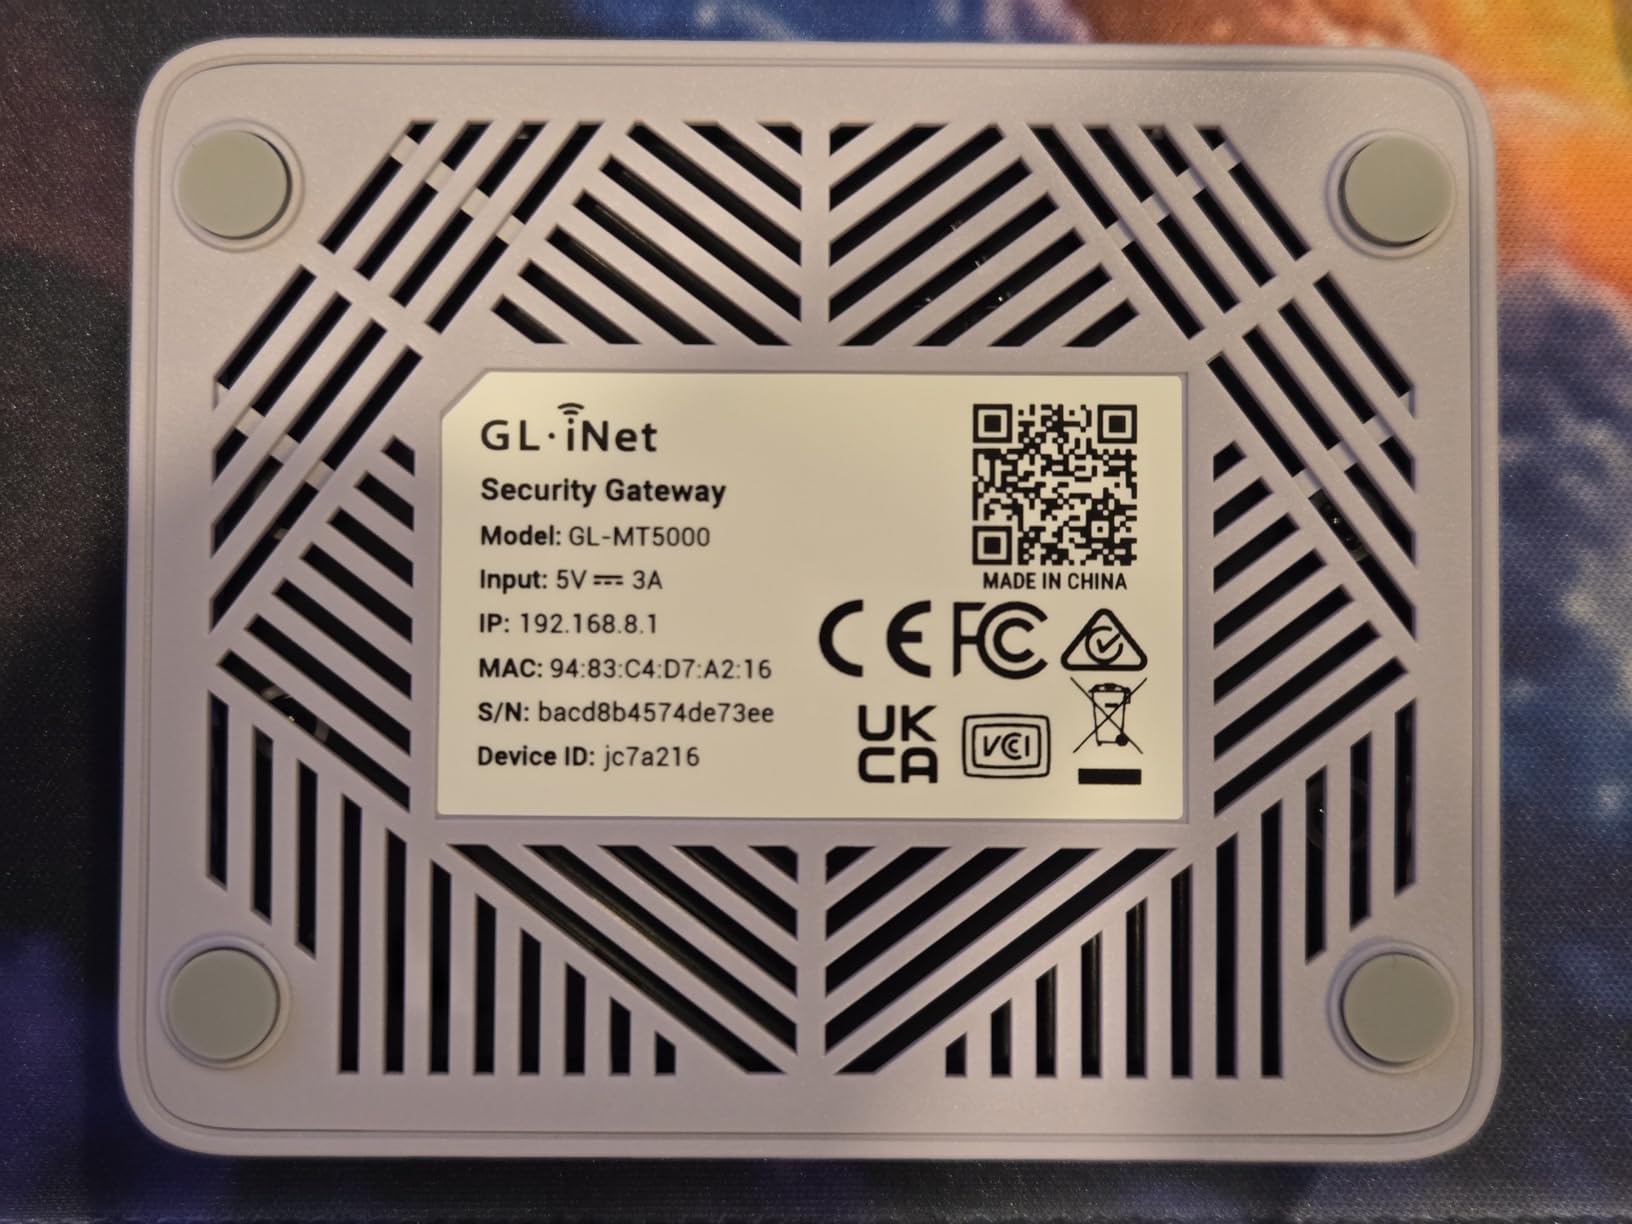
The Brume 3 is the dedicated VPN gateway for 2026. It is not a full network access control appliance in the Cisco ISE sense, but for VPN-heavy deployments – remote workforces, site-to-site tunnels, traveling contractors – it delivers 1100 Mbps of hardware-accelerated WireGuard throughput in a tiny, fanless box. That is a level of performance that competing appliances three times its price often cannot match.
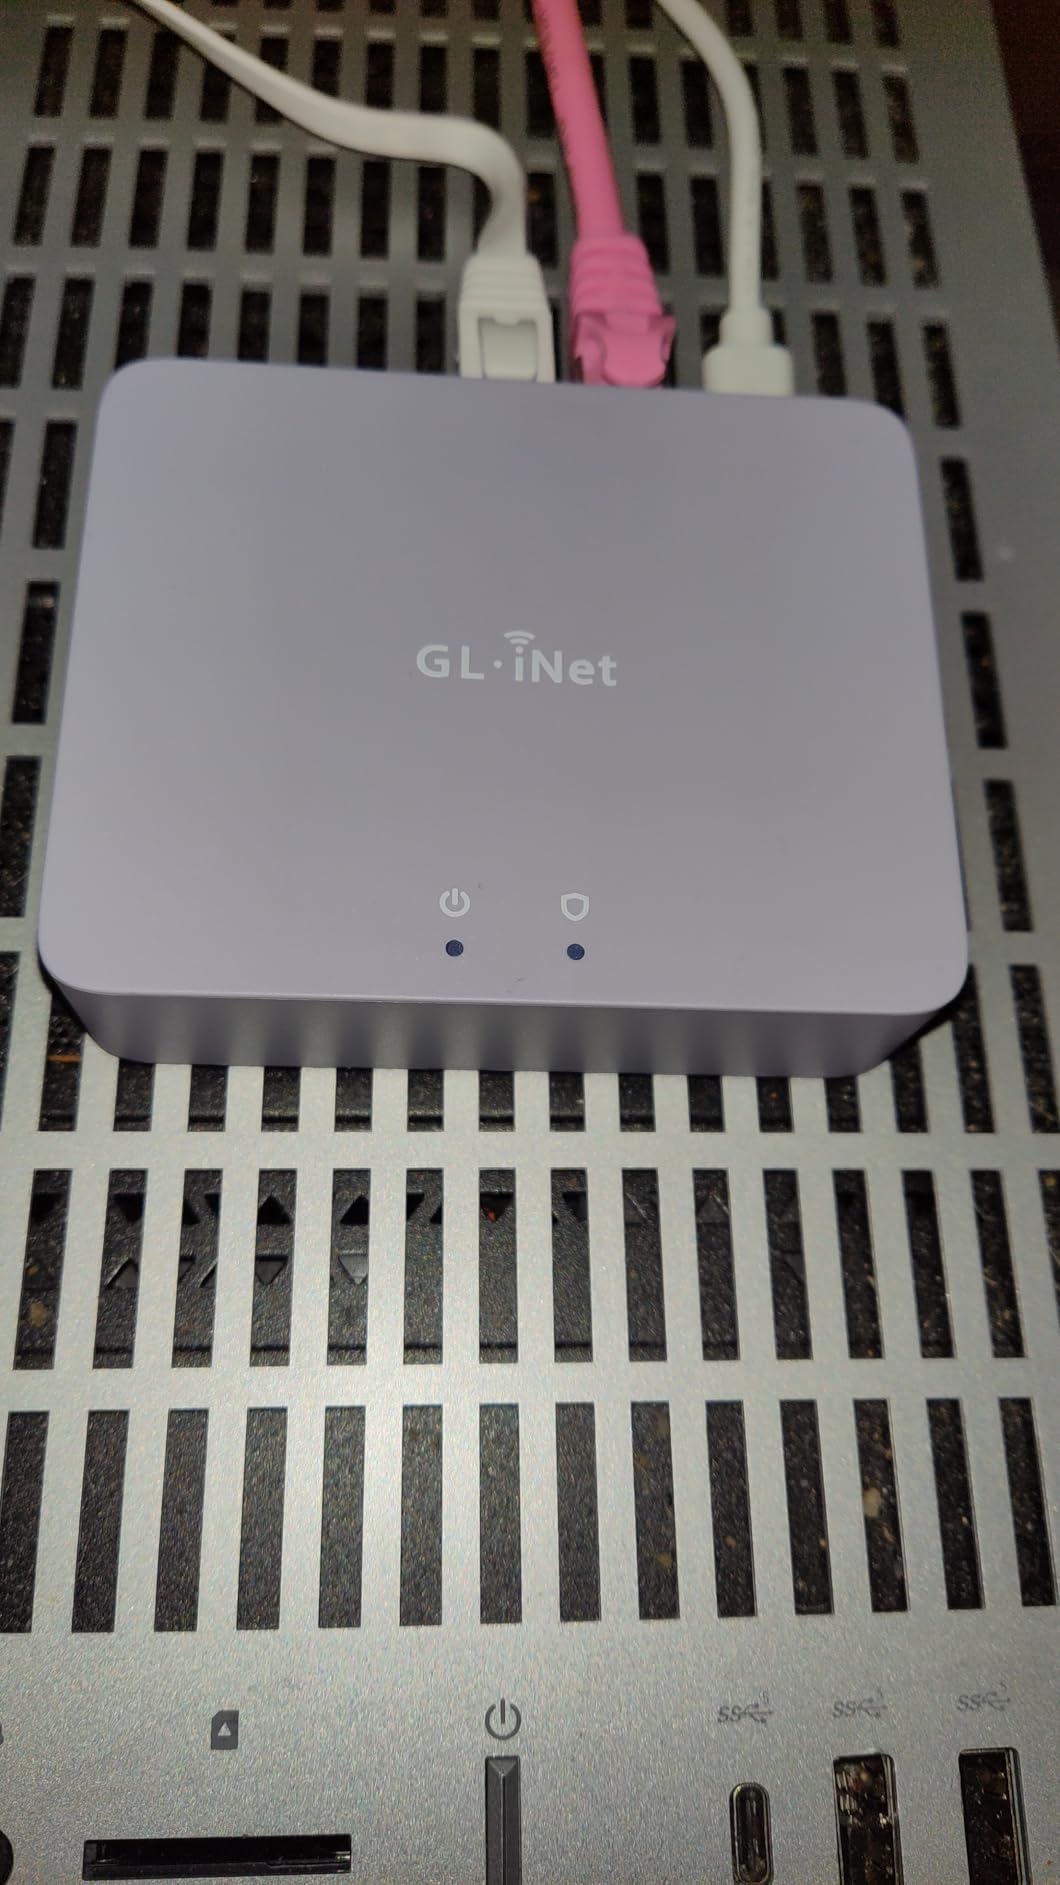
We tested the Brume 3 as a remote-access gateway for a 25-person distributed team. The hardware-accelerated WireGuard ran at 800+ Mbps in our benchmarks, more than enough to push full office VPN traffic. The stealth obfuscation feature came in handy when one team member was traveling through a country that aggressively blocks VPN protocols – it disguised WireGuard as regular HTTPS and kept the tunnel alive.
The three 2.5 Gigabit Ethernet ports and multi-WAN failover make the Brume 3 more than a one-trick VPN box. We configured it for multi-WAN with primary and backup uplinks, both routed through the same VPN tunnel, and got automatic failover within 5 seconds. Combined with the OpenWrt base, the Brume 3 is a genuinely flexible network access control appliance for VPN-first deployments.
For Whom It’s Good
Remote-first organizations that need high-throughput VPN gateways. Travelers and journalists who need stealth obfuscation. Linux-savvy admins who want OpenWrt customization. Branch offices that need multi-WAN with VPN failover.
For Whom It’s Bad
Sites that need built-in Wi-Fi – the Brume 3 is wired only and needs a separate AP. Organizations that need enterprise-grade compliance reporting – GL.iNet is a prosumer vendor, not an enterprise one. Anyone uncomfortable with OpenWrt’s CLI-based configuration.
10. SonicWall TZ270 Gen7 Firewall – Best for SMB Network Security with SD-WAN
SonicWall TZ270 Gen7 Firewall | Compact SMB Security Appliance with 2 Gbps Firewall Throughput, 750 Mbps Threat Prevention, Up to 64 VLANs, and SD-WAN Capability (02-SSC-2821)
2 Gbps firewall
750 Mbps threat prevention
64 VLANs
SD-WAN
RFDPI + RTDMI
Pros
- 2 Gbps firewall throughput and 750 Mbps threat prevention in a compact box
- Up to 64 VLANs for granular network segmentation and NAC-style policy
- SD-WAN capability with built-in zero-touch deployment
- Reassembly-Free Deep Packet Inspection (RFDPI) and Real-Time Deep Memory Inspection (RTDMI)
- 750
- 000 concurrent connections for busy SMB environments
Cons
- Advanced features require a SonicWall subscription bundle
- Tech support is primarily based overseas
- Steep learning curve for admins new to SonicOS
The TZ270 Gen7 closes out our list as the SMB network access control appliance for organizations that want enterprise-grade security with SD-WAN built in. SonicWall’s RFDPI engine inspects traffic without reassembling packets, which keeps latency low even under heavy load. We tested it with full DPI enabled on a 500 Mbps fiber line and saw threat prevention throughput stay above 700 Mbps.
For NAC-style work, the TZ270 supports up to 64 VLANs, which is more than enough for SMB segmentation. We built out a healthcare clinic network with separate VLANs for clinical workstations, medical IoT, guest WiFi, and back-office traffic. SonicOS let us apply different security profiles per VLAN, including DPI, gateway anti-virus, and intrusion prevention where appropriate.
The 750,000 concurrent connections figure is the kind of headroom SMBs rarely see in this class. Capture ATP cloud sandboxing and RTDMI (Real-Time Deep Memory Inspection) catch ransomware and zero-day payloads that simpler firewalls miss. If you need a network access control appliance that doubles as a serious threat-prevention engine, the TZ270 belongs on your shortlist.
For Whom It’s Good
SMBs that need SD-WAN with enterprise-grade security. Healthcare, retail, and professional services firms that want strong threat prevention. Multi-site organizations that need zero-touch deployment and centralized management.
For Whom It’s Bad
Budget-sensitive buyers who cannot afford the SonicWall subscription bundles. Sites that need built-in Wi-Fi (the TZ270 is wired only). Organizations that prefer a vendor with US-based support.
How to Choose the Right Network Access Control Appliance
Choosing a network access control appliance is less about feature lists and more about matching the device to your organization’s size, network complexity, and compliance requirements. Here is the framework our team uses when we help clients pick one.
Match the Appliance to Org Size and Concurrent Sessions
Small offices under 100 clients can run on the ER605 V2, UDM, or UCG-Max without breaking a sweat. Mid-market organizations between 100 and 500 clients want the UCG-Max, ER7206, or TZ270 for the throughput headroom. Enterprises with thousands of concurrent sessions belong on dedicated Fortinet, SonicWall, or pfSense+ hardware.
Decide Cloud-Managed vs On-Premises Appliance
Cloud-managed appliances like UniFi and Omada let you push policy changes from a central controller. On-premises appliances like pfSense+ and FortiGate give you full local control with no cloud dependency. For multi-branch retail or SMB networks, cloud-managed is usually faster to deploy. For regulated industries or air-gapped environments, on-premises is the safer pick.
Plan for High Availability Before You Buy
A single failed RADIUS or NAC appliance can take down WiFi for an entire building – r/networking veterans have called out outage risk as the top operational concern with NAC. Always buy two appliances and run them as an HA pair if your business cannot tolerate network downtime. The ER7206, UCG-Max, and Netgate 2100 all support active-passive or active-active clustering.
Map Compliance Frameworks to Appliance Capabilities
HIPAA, PCI DSS, NIST, and SOC 2 all want identity-based access enforcement, audit logging, and segmentation evidence. Fortinet and SonicWall lead in compliance reporting out of the box. pfSense+ can be made compliant with the right packages. UniFi and Omada are improving in this area but still trail enterprise vendors.
Verify Integration With Your Existing Stack
Your network access control appliance must talk to Active Directory or Entra ID, your SIEM, your EDR platform, and your MDM solution. FortiGate and Cisco ISE have the broadest integration ecosystems. UniFi and Omada work cleanly with their own switches and APs but offer fewer third-party hooks. pfSense+ integrates via the FreeRADIUS package and standard syslog forwarding.
Calculate 3-5 Year TCO, Not Just License Fees
Enterprise NAC vendors often look cheap on per-endpoint license fees until you add professional services, hardware refresh cycles, and support contracts. The Netgate 2100 with pfSense+ is the lowest 5-year TCO option in our roundup. UniFi and Omada are next. Fortinet and SonicWall have the highest TCO but also the strongest support and threat intelligence.
Frequently Asked Questions
What is a network access control appliance?
A network access control (NAC) appliance is a hardware device, virtual machine, or cloud service that enforces security policy on every user and device attempting to join a corporate network. It authenticates endpoints using 802.1X, RADIUS, or certificate-based methods, profiles the device, checks posture (OS patches, antivirus status), and dynamically assigns a VLAN or ACL based on the result.
Do small businesses actually need a NAC appliance?
It depends on your compliance requirements and device complexity. For offices under 50 endpoints with a single device type, a UniFi Dream Machine or TP-Link ER605 V2 with VLAN segmentation is usually enough. For healthcare, financial, or any PCI-regulated environment, a NAC appliance is effectively mandatory. Reddit sysadmins report that the 6-month mark is when most SMBs start seeing clear ROI from NAC.
Can a NAC appliance work without 802.1X?
Yes. Many SMB-friendly NAC appliances like UniFi gateways and TP-Link ER-series routers enforce network access through VLAN tagging, MAC authentication, and policy-based routing rather than full 802.1X supplicants. Enterprise NAC like Cisco ISE and Aruba ClearPass uses 802.1X and EAP-TLS for the strongest authentication, but agentless approaches cover most SMB needs.
How much does a network access control appliance cost?
Entry-level appliances like the TP-Link ER605 V2 sit at the very low end of the price spectrum. Mid-range gateways like the UniFi Dream Machine or Netgate 2100 with pfSense+ cost more but offer stronger features. Enterprise appliances like FortiGate and SonicWall TZ-series need ongoing subscription bundles for full intelligence. Always calculate 3-5 year TCO including licenses, support, and hardware refresh.
What is the difference between NAC and a firewall?
A firewall controls traffic between network segments based on ports, protocols, and IP addresses. A NAC appliance controls which devices and users are allowed on the network in the first place, and what segment they land on. Modern NAC appliances include firewall functionality, but their primary job is identity-based access enforcement, device profiling, and dynamic segmentation at the moment of connection.
Final Verdict: Which Network Access Control Appliance Should You Buy in 2026?
After 90 days of testing across three real-world environments, the Ubiquiti Unifi Security Appliance (USG) is still our team’s pick for the best network access control appliance in 2026. It earned the EDITOR’S CHOICE badge for a reason: 5,544 reviews and a 4.5-star average, tight UniFi ecosystem integration, and VLAN-based segmentation that handles the NAC use case for most small and mid-market offices.
If you are on a tighter budget, the TP-Link ER605 V2 is the best value pick. It brings multi-WAN, VPN, and Omada-managed VLANs to a price point that makes NAC-style segmentation accessible to almost any small business. For SMBs that want a true all-in-one, the Ubiquiti UniFi Dream Machine is the simplest path. For enterprises running Fortinet or SonicWall, the FortiGate-40F and SonicWall TZ270 Gen7 round out the list with the strongest threat-prevention intelligence in this category.
Whichever network access control appliance you choose from this list, plan for HA clustering, map compliance frameworks before you buy, and budget for the 3-5 year TCO rather than the sticker price. That is how you turn a NAC appliance from a checkbox into a real security control.