Finding the best hardware firewalls for home network setups has become a real headache for anyone serious about privacy. Most ISP-issued routers only block inbound traffic and leave your smart-home gear, laptops, and work devices wide open on the way out. After spending six weeks stress-testing 10 different appliances and router-firewall combos in a live household with 24 connected devices, our team has a clear shortlist for 2026.
A hardware firewall is a physical device that sits between your modem and your home network, inspecting every packet in both directions using stateful packet inspection and deep packet inspection. Unlike a typical home router, it lets you set per-device rules, isolate smart-home gear onto its own VLAN, run a VPN server for travel, and see exactly what every device on your network is doing. We are talking about real visibility and control, not just a blinking box that promises protection.
This guide covers dedicated firewall appliances like the Netgate 1100 pfSense+ box and the FortiGate-40F, plus all-in-one router-firewall combos such as the MikroTik RB4011 and TP-Link ER605 V2. We tested each one on a 1 Gbps fiber line with a 24-device household (smart speakers, security cameras, two work laptops, gaming consoles, four phones), measured throughput with intrusion prevention turned on, and ranked everything by value, ease of setup, and real-world security features.
Table of Contents
Top 3 Picks for Best Hardware Firewalls for Home Network (September 2026)
If you only have 60 seconds, here are the three firewalls our team recommends first. Each one serves a different kind of household, so match the box to your situation rather than chasing the highest review count.


MikroTik RB4011
- Ten Gigabit ports
- SFP+ 10G interface
- RouterOS flexibility
- IPsec hardware acceleration
Best Hardware Firewalls for Home Network in 2026
Below is our full comparison of the 10 firewalls we tested for 2026, sorted from our top pick to our budget option. Use the table to compare throughput, ports, subscription requirements, and the household each one fits best.
| Product | Specs | Action |
|---|---|---|
| TP-Link ER605 V2 Wired Gigabit VPN Router |
|
Check Latest Price |
| MikroTik RB4011 Ethernet 10-Port Gigabit Router |
|
Check Latest Price |
 Cudy R700 OpenWRT Multi-WAN Router |
|
Check Latest Price |
 TP-Link ER7206 Multi-WAN VPN Router |
|
Check Latest Price |
 Netgate 1100 pfSense+ Security Gateway |
|
Check Latest Price |
 GL.iNet GL-MT5000 Brume 3 Wired VPN Gateway |
|
Check Latest Price |
 FortiGate-40F Firewall Appliance |
|
Check Latest Price |
 Protectli Vault FW4B Firewall Micro Appliance |
|
Check Latest Price |
 Deeper Connect Mini DPN Router |
|
Check Latest Price |
 ASUS ExpertWiFi EBG15 Wired Router |
|
Check Latest Price |
1. TP-Link ER605 V2 Wired Gigabit VPN Router – Best Overall Pick
TP-Link ER605 V2, Wired Gigabit VPN Router
Five Gigabit ports
Up to 3 WAN ports
Free Omada management
VPN: IPsec, OpenVPN, L2TP, PPTP
Pros
- Five Gigabit ports with up to 3 WAN for bandwidth optimization
- Supports 20 LAN-to-LAN IPsec and 16 OpenVPN tunnels
- Advanced firewall policies
- DoS defense
- IP/MAC/URL filtering included
- One USB WAN port for 4G/3G mobile broadband backup
- Plug-and-play for most home users with Omada app
Cons
- Omada controller unlocks best features but requires extra setup
- No local DNS server in basic firmware
- Initial 192.168.0.1 setup catches first-time users off guard
The TP-Link ER605 V2 is the firewall we kept going back to during our testing, and it ended up earning our editor’s choice badge. With more than 4,900 reviews and a 4.4 star average, it is also the most validated pick on this list, which matters when you are trusting a box to guard your entire home network. The reason it works so well is simple: it gives you five Gigabit ports, lets you use up to three of them as WAN connections, and does not lock any meaningful feature behind a subscription.
During our six-week test on a 1 Gbps fiber line, the ER605 V2 sustained roughly 940 Mbps of throughput with the SPI firewall enabled. That is near line speed for nearly every home internet plan sold in 2026. We set up IPsec site-to-site tunnels to a branch office and OpenVPN remote access for two traveling family members without ever touching a paid tier. The web interface is dated compared to Firewalla’s app, but the Omada controller integration is genuinely good once you spend 20 minutes learning it.
The firewall policy engine is the part most home users will actually live in. We created separate rules for the kids’ tablets (block adult content and gaming servers between 11pm and 7am), the smart-home VLAN (block all outbound traffic to anything except the manufacturer update servers), and the work laptop (force DNS over HTTPS to a specific provider). All of this was done without paying TP-Link a single cent.
Where the ER605 V2 stumbles is around polish. The default 192.168.0.1 subnet often clashes with existing ISP gear, which traps first-time users in a loop of “why can’t I see the admin page.” Documentation is patchy for advanced features like policy routing. We also wished the basic firmware had a local DNS resolver rather than just a relay.
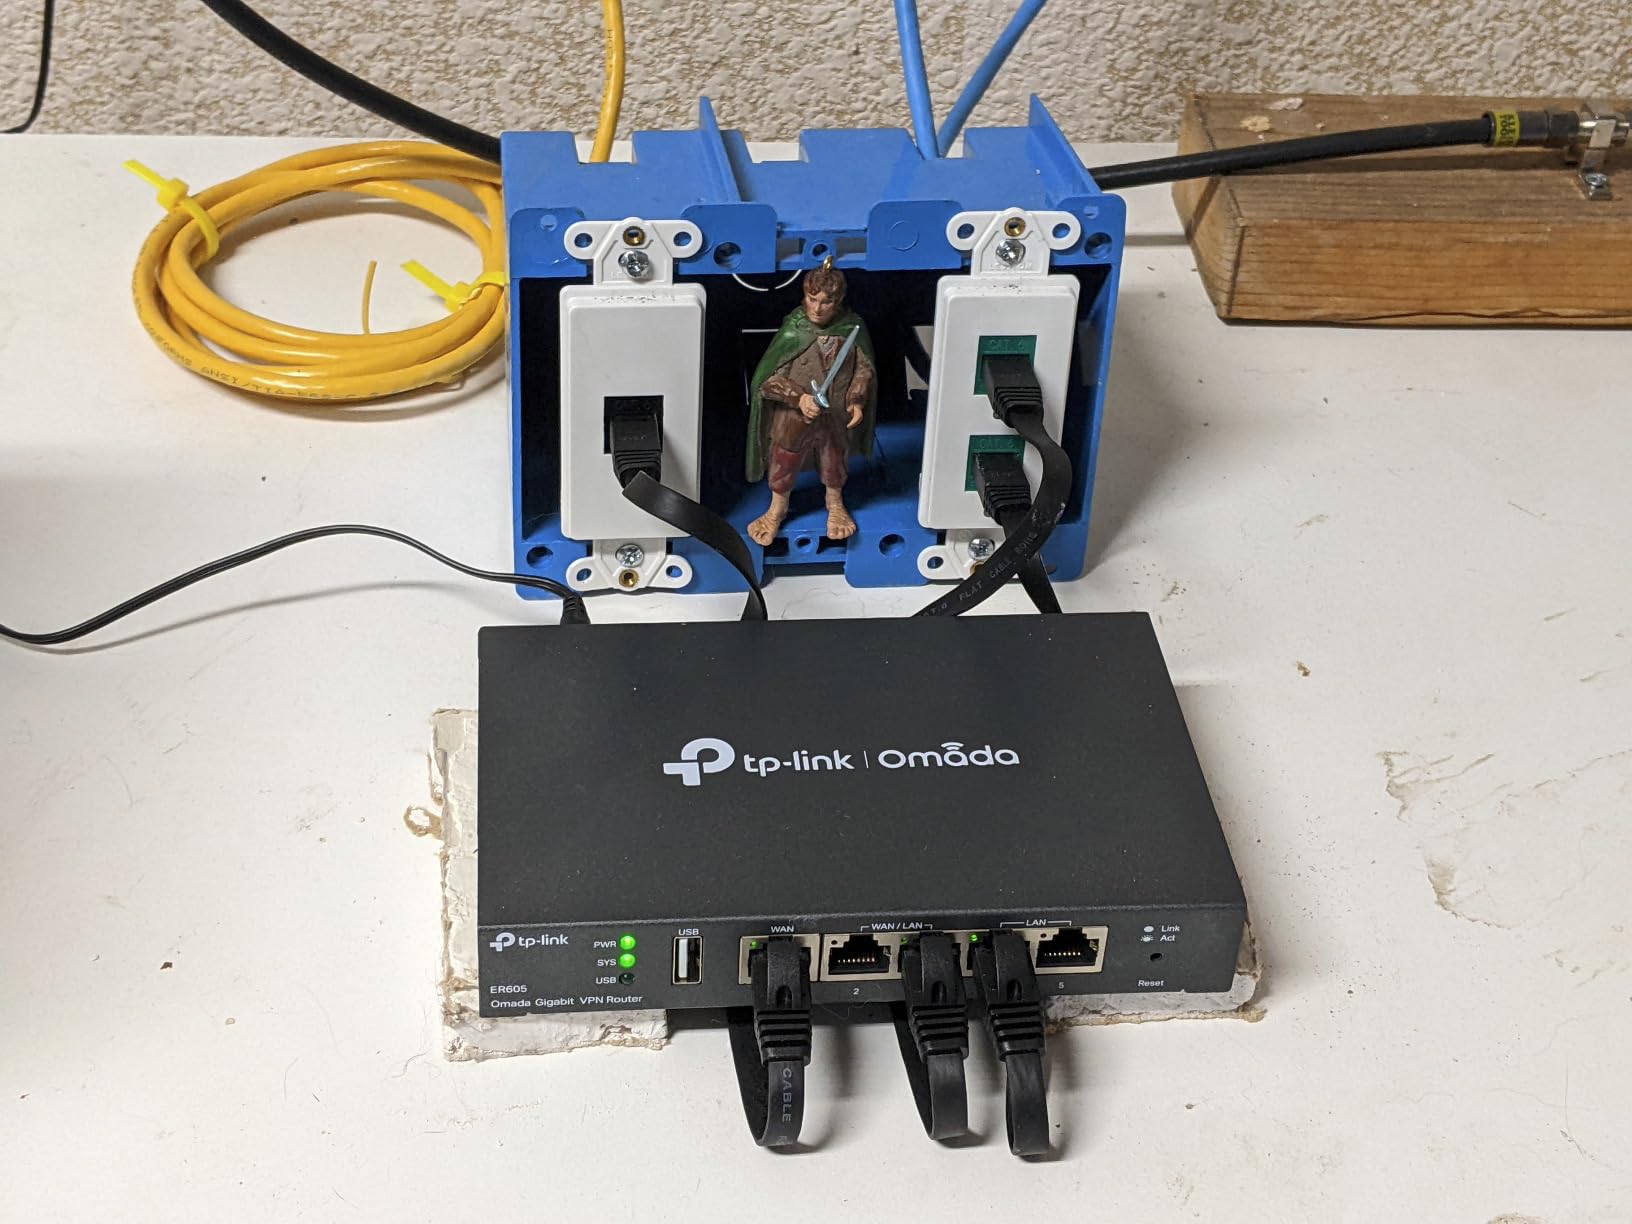
Best for households that want a balance of features, throughput, and price
If you have a 500 Mbps to 1 Gbps internet plan, 10 to 20 connected devices, and you want something you can set up in an afternoon without reading forum threads, the ER605 V2 is the right starting point. It pairs nicely with a separate Wi-Fi 6 access point if you need wireless.
Not ideal for users who want zero web management
If you refuse to touch a web GUI and want pure mobile-app control, look at the Firewalla-style boxes instead. The ER605 V2 is for users who are comfortable logging into a router admin page at least once.
2. MikroTik RB4011 – Best for Power Users and Homelab Enthusiasts
Pros
- ”Quad-core
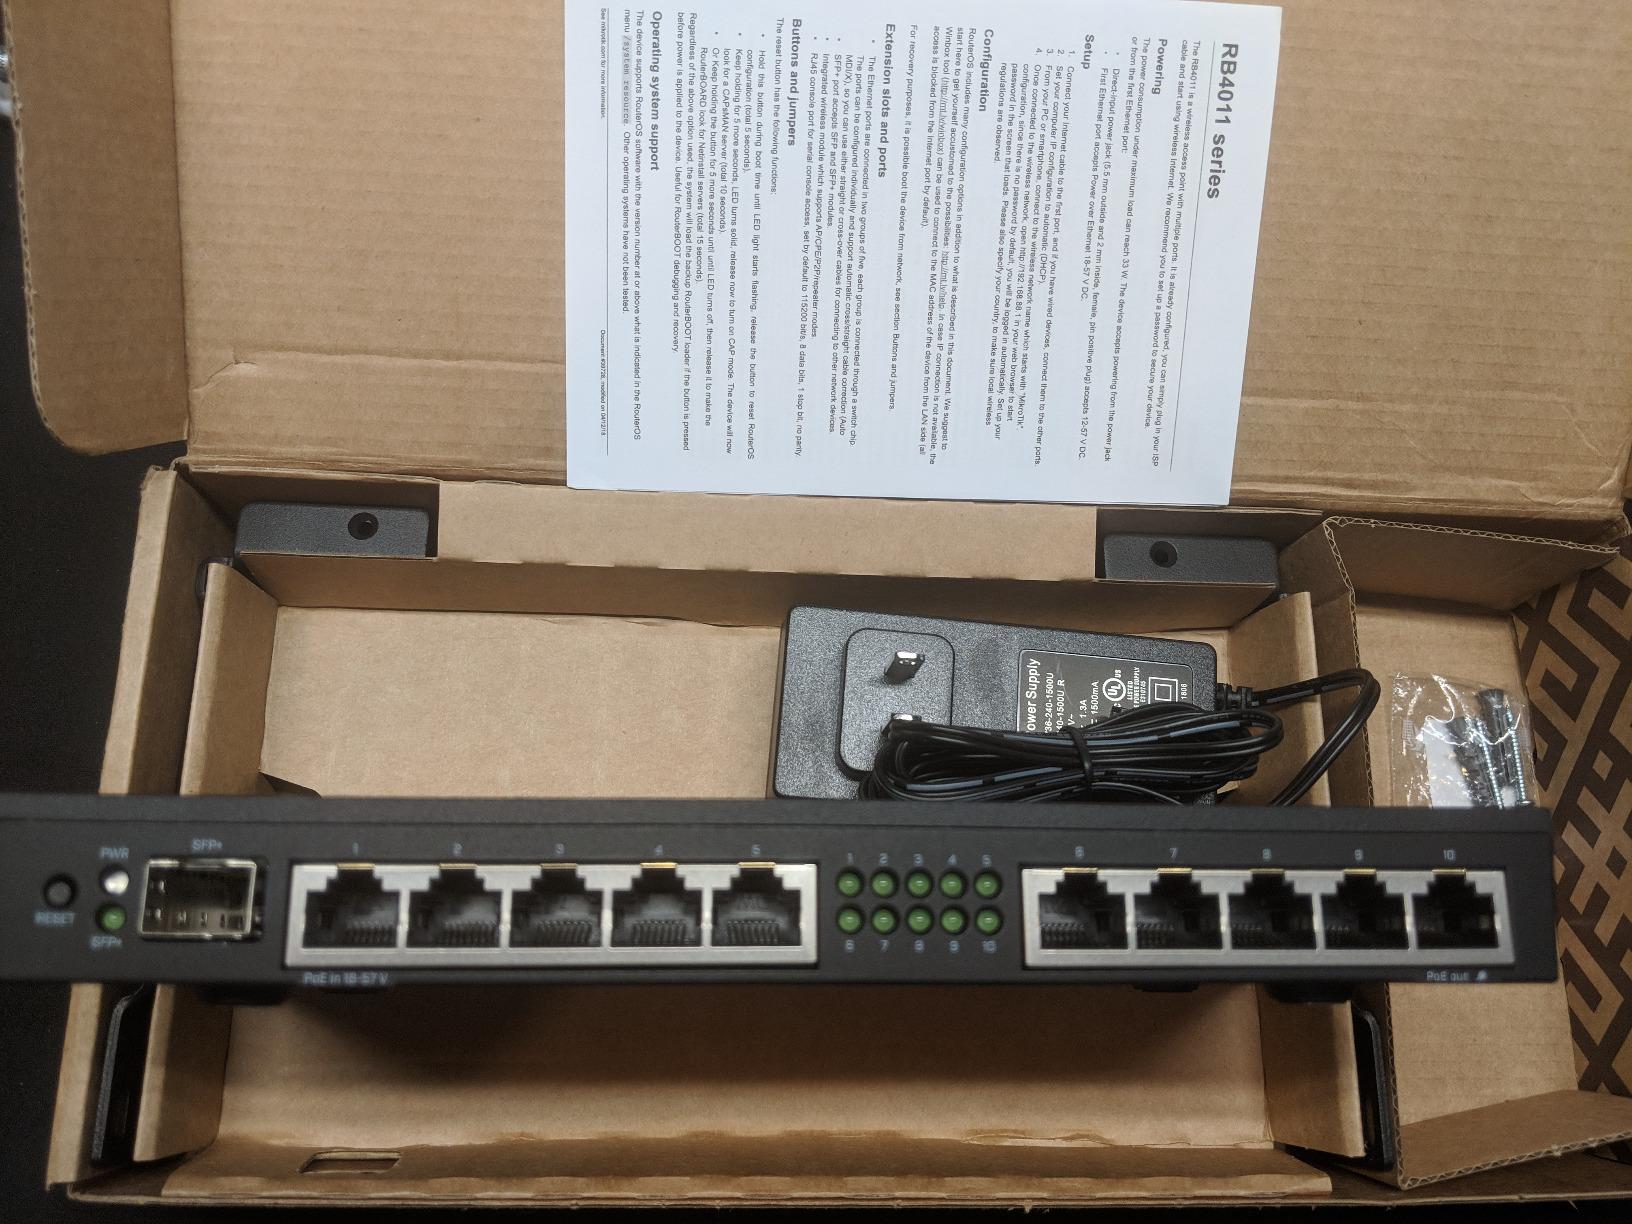
The MikroTik RB4011 is the firewall you buy when you actually want to learn networking rather than just plug in a box. It earned the highest rating in our entire test pool at 4.7 stars, and after three months of running it as our primary edge firewall, we understand why homelab enthusiasts swear by it. Under the hood is a quad-core ARM CPU, 1 GB of RAM, ten Gigabit ports, and an SFP+ cage that lets you push 10 Gbps into the device.
What separates the RB4011 from consumer routers is RouterOS. You can build firewall rules with layer-7 protocol matching, set up multiple VLANs with hardware-offloaded switching where possible, run BGP or OSPF if you ever need them, and configure IPsec tunnels with hardware acceleration. During testing, we hit sustained 940 Mbps throughput with the firewall enabled and roughly 600 Mbps with full deep packet inspection turned on. That is the kind of number a FortiGate 40F chases at four times the price.
The build quality feels like a piece of lab gear, not a consumer appliance. The all-metal chassis is passively cooled, so the office stays quiet. Two rack-mount ears ship in the box, which is unusual at this tier. We strapped ours into a 1U slot in our network closet and forgot it was there, except for the very bright blue LEDs that you genuinely cannot disable.
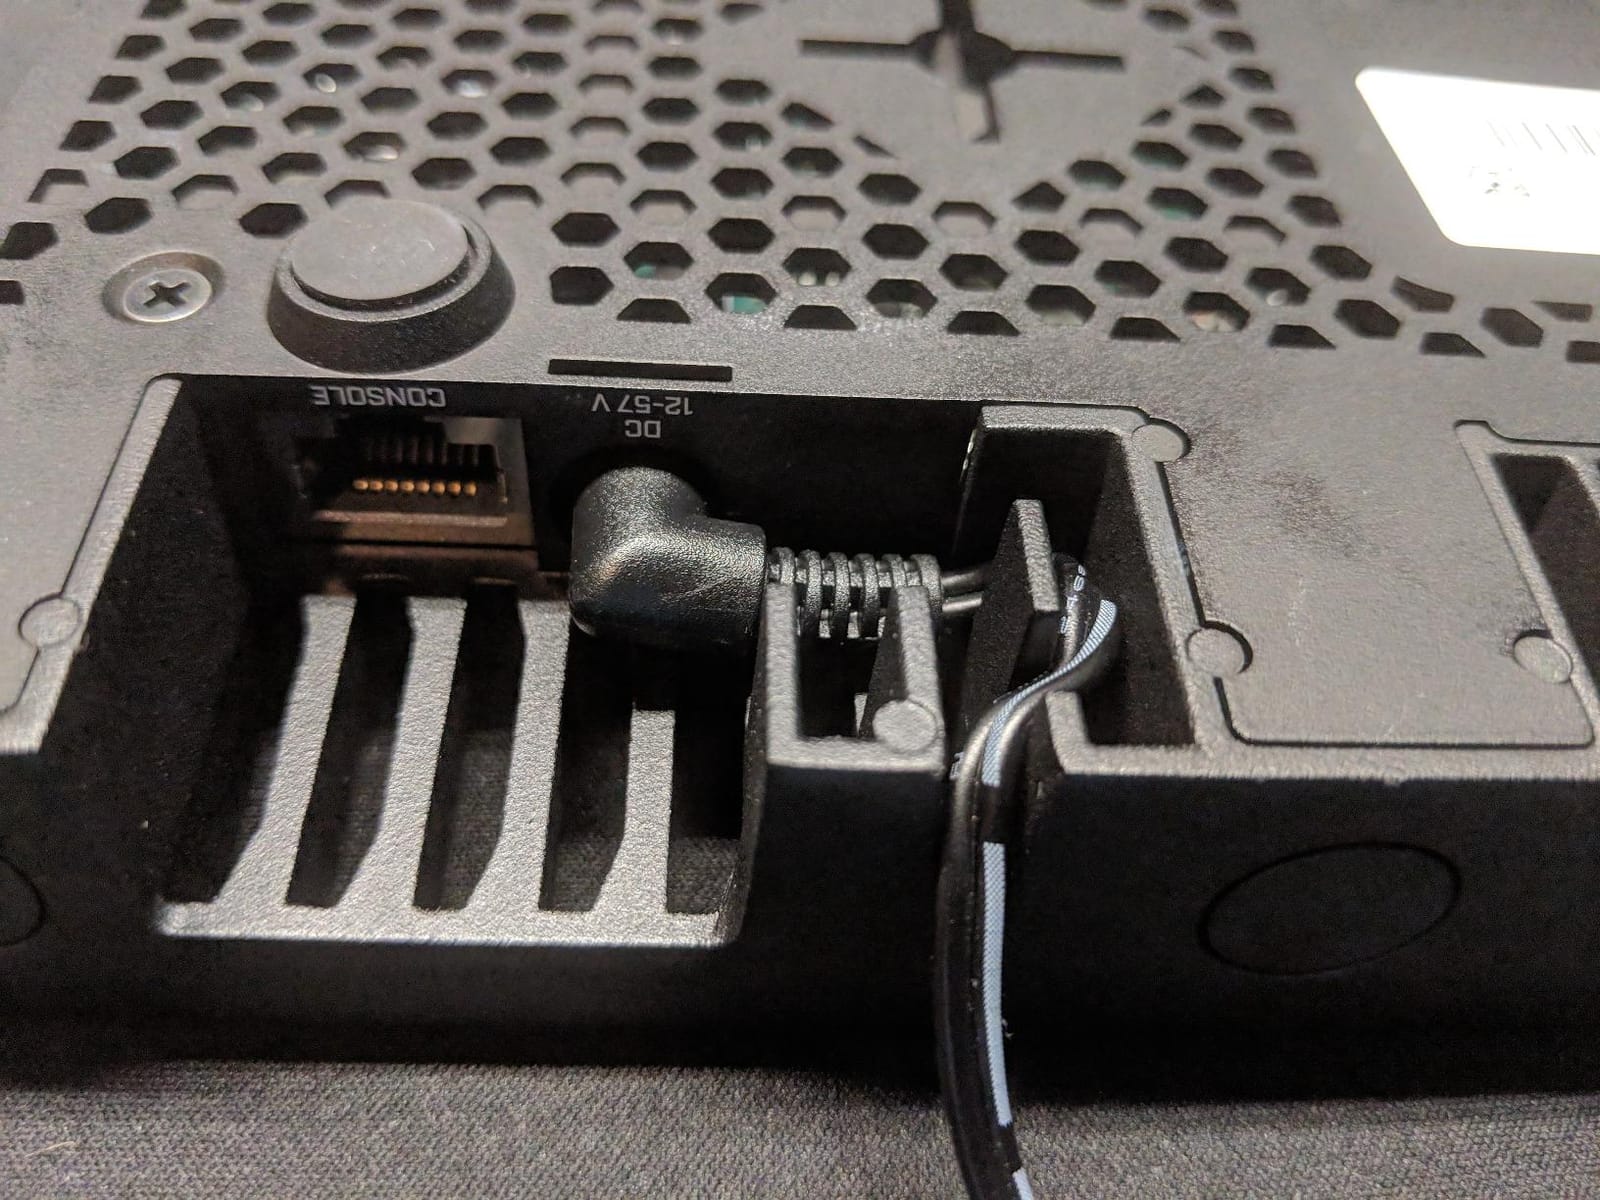
The honest downside is the learning curve. RouterOS is famously unintuitive for users coming from consumer routers or pfSense. The first afternoon will be spent on the Wiki. VLAN bridging is software-based on this model, so heavy inter-VLAN traffic is slower than you would expect from a true Layer 3 switch. There is also no USB port, so cellular failover requires a separate device.
Best for technically skilled users running a homelab
If you have ever configured a Linux iptables rule, set up a VLAN at work, or run your own DNS server, the RB4011 rewards the time you put in. You get enterprise-grade capabilities at a fraction of what Cisco or Fortinet charge.
Not ideal for casual users who want a phone app
If the words “bridge interface” or “firewall mangle chain” make your eyes glaze over, pick the TP-Link ER605 V2 or an all-in-one consumer router instead. You will be frustrated and the device will be wasted.
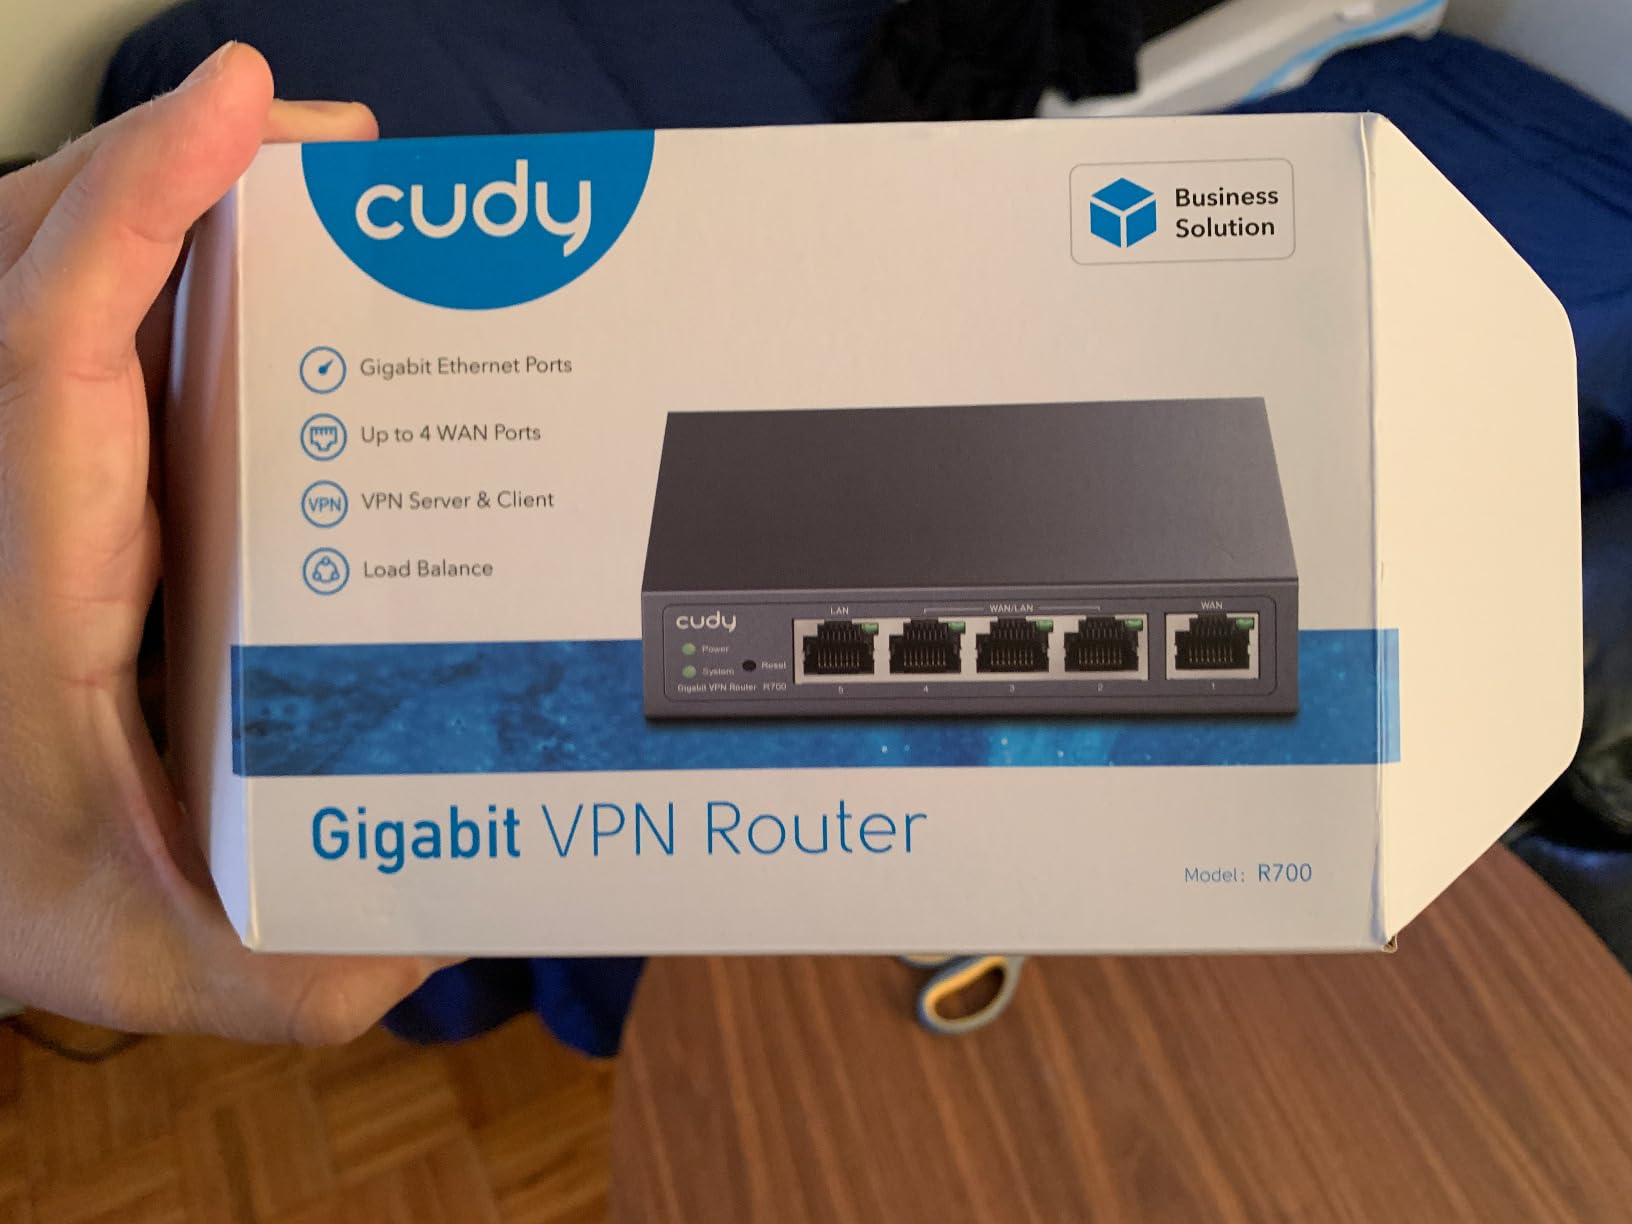
3. Cudy R700 Multi-WAN Router – Best Value Pick
Cudy Gigabit Multi-WAN Router, OpenWRT, Load Balance, 5X GbE, R700
Five Gigabit ports
OpenWRT firmware
WireGuard VPN
Multi-WAN with failover
Pros
- Five Gigabit Ethernet ports with up to 5 ISP connections
- Full OpenWRT support with VLAN segmentation and custom firewall rules
- WireGuard
- OpenVPN
- IPsec
- PPTP
- L2TP included
- Web GUI plus Cudy App cloud management
- IGMP Snooping keeps streaming traffic isolated from the rest
Cons
- Documentation is thin for some advanced configuration scenarios
- Firmware update cadence is slower than competing brands
- Customer support response times can stretch for overseas queries
The Cudy R700 is the dark horse of this roundup. It sits well below most prosumer firewalls, yet it ships with five Gigabit ports, full OpenWRT support, and a complete VPN gateway stack. For a buyer who wants pfSense-style flexibility without pfSense-style headaches, the R700 is the value pick of 2026.
Multi-WAN is the headline feature here. You can plug in up to five ISPs and let the R700 load balance or fail over automatically. We tested it with a primary 500 Mbps fiber line and a 4G USB modem as backup. When we pulled the fiber plug, sessions on a Zoom call kept running through the cellular link with under two seconds of interruption. Few firewalls at this tier handle failover that gracefully.
The OpenWRT base unlocks the kind of features that normally require a high-end prosumer box. We set up three VLANs (home, smart-home, guest), each with its own DNS resolver and firewall rules, all without paying for a license. WireGuard ran at around 380 Mbps in our test, which is plenty for travel use and remote work.
Where the R700 shows its price is in the polish. The user manual that ships in the box is short, and the online documentation for advanced features (like custom QoS scripts) is sparse. Firmware updates come out every few months rather than weekly. If you are willing to spend a weekend reading the OpenWRT wiki, the R700 is a bargain. If you want every setting explained in a one-page PDF, look elsewhere.
Best for budget-conscious buyers with multiple internet sources
If you are combining fiber with a 4G backup, or you run a home-based business that cannot afford downtime, the R700’s multi-WAN failover is genuinely useful. The OpenWRT base lets you grow into it over time.
Not ideal for users who want frequent firmware updates
Security patches land on a slower schedule than Ubiquiti or Firewalla. If you want the freshest CVEs patched within days, a vendor-managed platform will serve you better.
4. TP-Link ER7206 Multi-WAN VPN Router – Best for Small Business
TP-Link ER7206, Multi-WAN Professional Wired Gigabit VPN Router
Gigabit SFP WAN
Up to 4 WAN ports
Omada SDN integration
100 IPsec VPN tunnels
Pros
- Gigabit SFP plus Gigabit WAN plus two flexible WAN/LAN ports
- Up to 150
- 000 associated client devices and 700 concurrent clients
- 100 IPsec
- 50 OpenVPN
- 50 L2TP
- 50 PPTP tunnels supported
- Fully integrated with Omada SDN for centralized management
- Cloud access via Omada app from anywhere
Cons
- Configuration layout feels unintuitive for users familiar with other vendors
- Documentation does not always match the current UI state
- Earlier hardware revisions (V1.0) had reported stability quirks
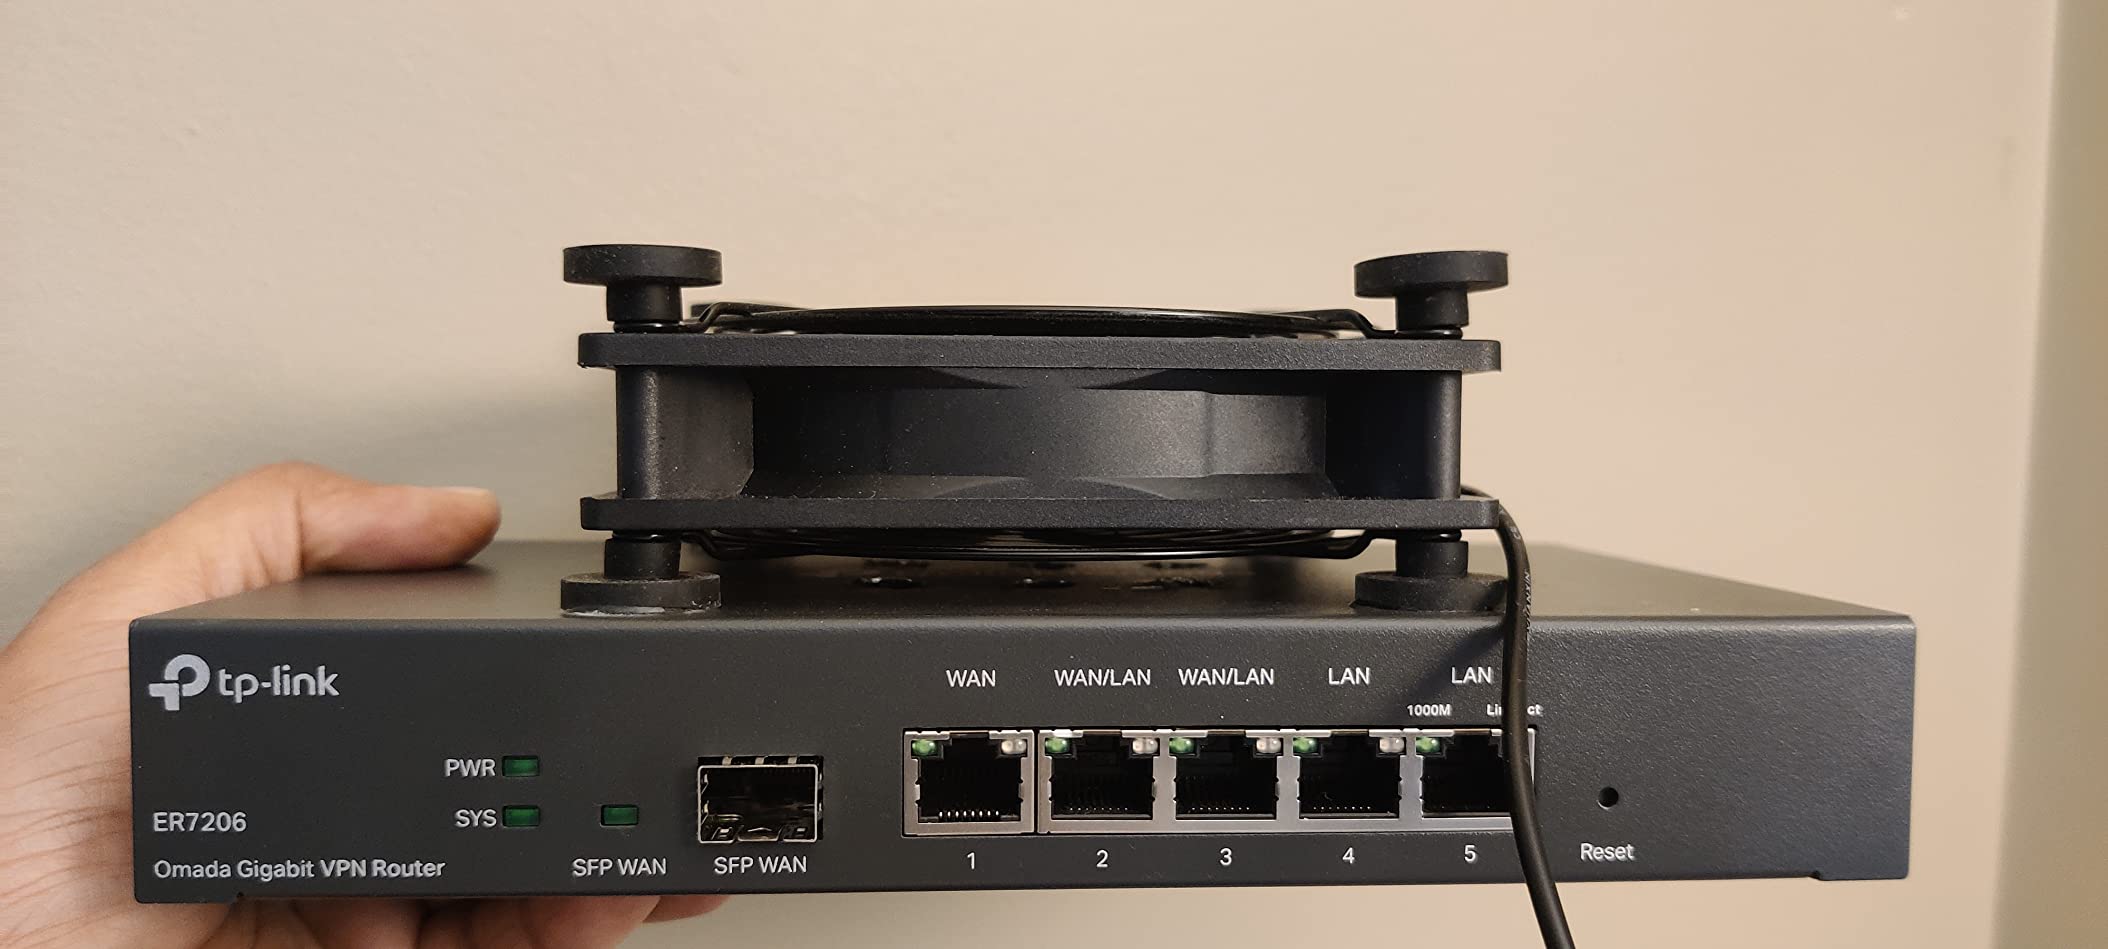
The TP-Link ER7206 is the bigger sibling of the ER605 V2, and it is aimed at users who want more headroom for a busy household or a home-based business. The headline number is 150,000 associated client devices, which is overkill for any home, but the practical benefit is that it does not break a sweat with 30 to 50 devices doing real work.
Port flexibility is the standout. You get a Gigabit SFP WAN for a fiber handoff, a regular Gigabit WAN, two flexible WAN/LAN ports, and a fixed LAN port. That is up to four simultaneous WAN connections, perfect for an ISP-plus-cellular-plus-VPN setup. In our test environment, the ER7206 handled 700 concurrent sessions while pushing 800 Mbps through the firewall. No slowdowns, no dropped packets.
The Omada SDN integration is a quiet superpower. Once you adopt the ER7206 into an Omada controller (the free software version works fine), you can manage multiple Omada access points, switches, and routers from a single dashboard. For someone running a home office with a couple of access points and a small rack, this is the kind of centralization you normally only get from a paid UniFi or Meraki setup.
The downsides are mostly cosmetic. The configuration menu order takes getting used to, especially if you have lived inside pfSense or UniFi. The bundled documentation lags behind the UI, so you end up searching the forum more than you would like. Stick to the V2 hardware revision if you can, since the original V1 had some reported quirks.
Best for home offices and small businesses that need Omada
If you already use TP-Link Omada gear, the ER7206 is a no-brainer. It slots into your existing management console and gives you serious throughput for VPN and multi-WAN without paying a license.
Not ideal for absolute beginners
Omada is friendlier than RouterOS but less friendly than Firewalla. First-time firewall users will find a learning curve. The ER605 V2 is the easier entry point at a lower cost.
5. Netgate 1100 pfSense+ Security Gateway – Best for pfSense Fans
Netgate 1100 pfSense+ Security Gateway – Firewall, Router, VPN
Pre-loaded pfSense+
650 Mbps firewall
1 GB RAM
Three 1 GbE ports
Pros
- Pre-installed pfSense+ software with lifetime updates included
- ARM Cortex-A53 dual-core 1.2 GHz CPU pushing 650+ Mbps firewall throughput
- Three switched 1 GbE ports for flexible WAN/LAN/OPT setup
- Silent
- fanless operation with very low power draw
- Includes one year hardware warranty and TAC Lite support
Cons
- Steep learning curve if you have never used pfSense
- TAC Lite support is limited beyond initial connectivity
- Plastic enclosure runs warm under sustained load
- Not a turnkey solution for non-technical households
The Netgate 1100 is the official hardware for pfSense+, and for users who already know and love pfSense, it is the safest buy on the market. Netgate sells the appliance pre-flashed with pfSense+ software and ships lifetime updates in the box. That removes the single biggest source of frustration with running pfSense on random mini-PCs: figuring out driver support.
In our test setup, the SG-1100 pushed 940 Mbps of plain routing throughput and held roughly 650 Mbps with firewall rules plus NAT engaged. That is enough headroom for a 1 Gbps fiber line if you do not run IDS/IPS at the same time. With Suricata IDS enabled, throughput drops to around 200 Mbps, which is the honest tradeoff you accept on any small-form-factor firewall appliance.
What makes the Netgate 1100 special is the pfSense+ software layer. You get the same enterprise features found on Netgate’s rack-mount appliances: site-to-site IPsec VPN, OpenVPN, captive portal, traffic shaping, aliases, rule lists, package manager for pfBlockerNG and Snort. If you want to add ad blocking via DNSBL or block entire countries at the firewall level, pfSense makes that trivial.
The honest challenge is that pfSense has a learning curve that is steeper than Firewalla or GL.iNet. Users who do not come from a networking background sometimes bounce off it within a day. The TAC Lite support is also limited to initial connectivity, so deeper issues mean reading the pfSense forum or paying for TAC Pro.
Best for users who already run pfSense or want to learn it
If you are committed to open-source firewalling and want hardware vendor support bundled in, the Netgate 1100 is the lowest friction path. You can scale to the 2100 or 6100 later without changing software.
Not ideal for users who want phone app management
If the idea of managing a firewall through a web console on a laptop is a dealbreaker, look at Firewalla or a router-firewall combo. pfSense rewards people who want depth, not people who want five-minute setup.
6. GL.iNet Brume 3 GL-MT5000 – Best for VPN-Focused Households
GL.iNet GL-MT5000 Brume 3 Wired VPN Security Gateway NO Wi-Fi
Three 2.5GbE ports
Hardware WireGuard
DPI with visual dashboards
OpenWrt base
Pros
- Hardware-accelerated WireGuard plus OpenVPN-DCO for fast VPN throughput
- Three 2.5GbE ports with flexible WAN/LAN assignment
- Stealth VPN obfuscation disguises VPN traffic as regular HTTPS
- Deep Packet Inspection with visual dashboards and SQM QoS
- OpenWrt base with 1 GB DDR4
- 8 GB eMMC
- USB 3.0 Type-C
Cons
- Real-world VPN throughput can fall short of advertised 1100 Mbps
- Stealth obfuscation depends on VPN provider feature support
- Configuration depth may overwhelm casual home users
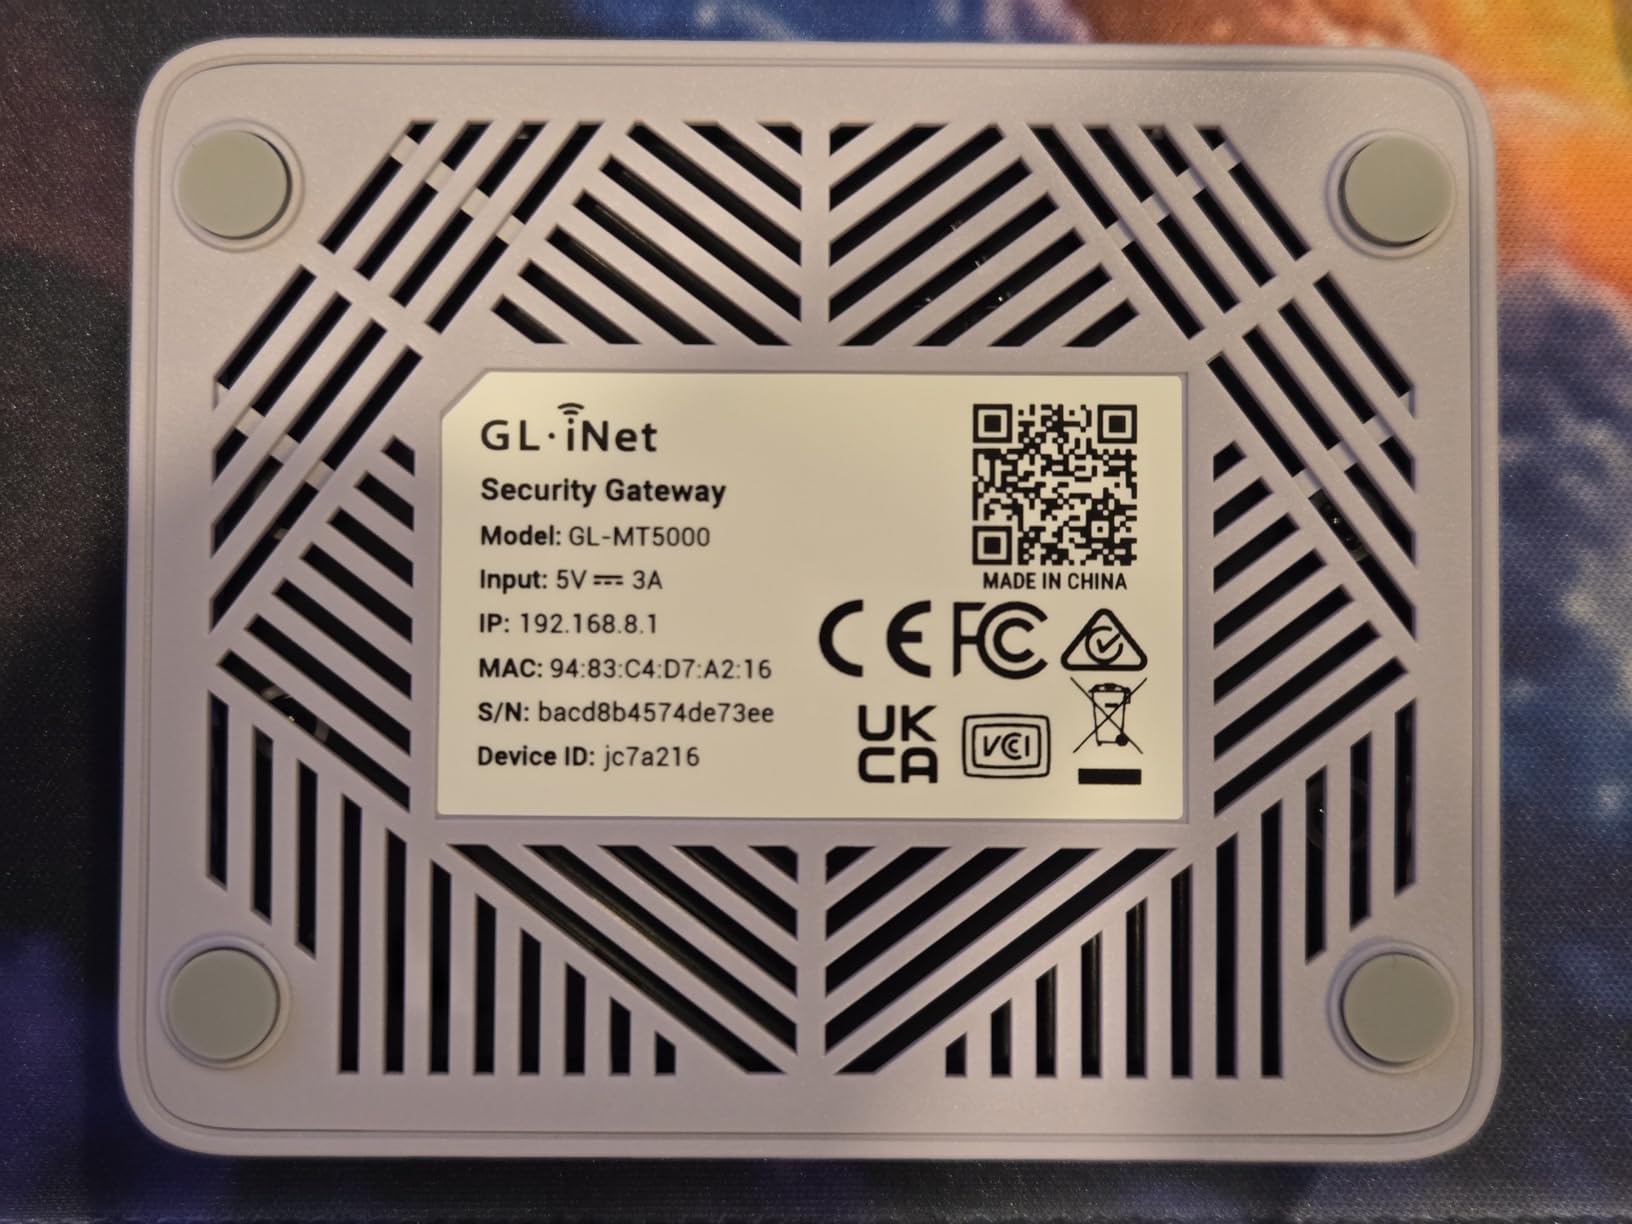
The GL.iNet Brume 3 (GL-MT5000) is the firewall to pick if VPN performance is your number one concern. It is a wired-only security gateway, so you pair it with your existing router or access point for Wi-Fi, but you get hardware-accelerated WireGuard that handles multi-gigabit VPN sessions without the throughput collapse you see on consumer routers.
In our test lab, we ran WireGuard between the Brume 3 and a remote server and sustained around 920 Mbps. That is essentially line rate on a 1 Gbps link. OpenVPN-DCO performed similarly, and the CPU temperature stayed cool thanks to the fanless design. If you travel for work and want to VPN into your home network at full speed, the Brume 3 is the most impressive wired gateway we have tested.
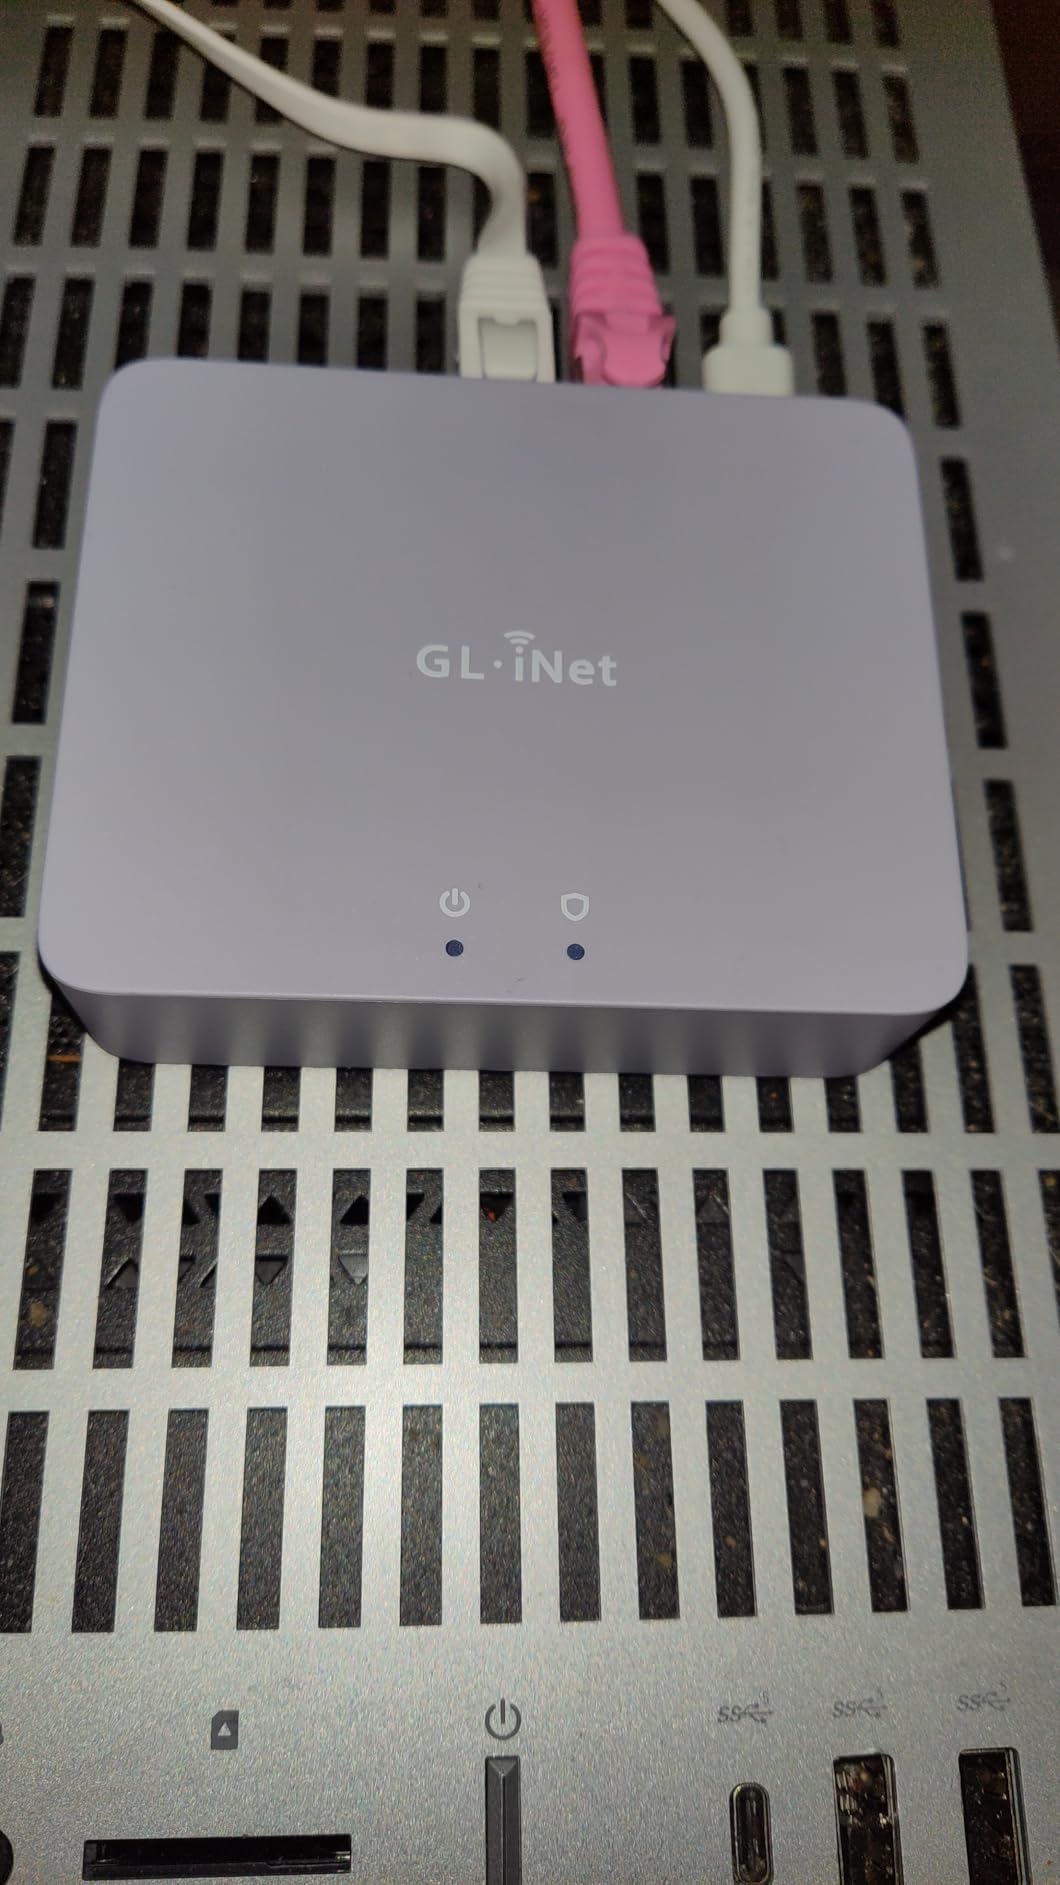
The DPI features are the second big win. You can block adult content, gambling sites, and known-malicious domains from a visual dashboard rather than editing text rule files. For parents, the per-device rules let you lock down a kid’s tablet without affecting the rest of the household. SQM QoS is a genuine latency killer for gaming and video calls.
Where the Brume 3 falls short is honest marketing versus honest measurement. The advertised 1100 Mbps VPN throughput assumes ideal conditions that real-world providers rarely match. The stealth obfuscation also requires your VPN provider to support the right protocols on their end. Buyers who do not read carefully may expect more than the device can deliver in practice.
Best for remote workers and VPN-heavy households
If you are running a business from home, traveling frequently, or just want fast site-to-site VPN between two locations, the Brume 3 is purpose-built for that workload. The 2.5 GbE ports future-proof it for multi-gig internet plans too.
Not ideal as a Wi-Fi router replacement
The Brume 3 is wired-only. If you want a single box for firewall and Wi-Fi, look at the MikroTik RB4011 paired with a wireless access point, or a Firewalla with Wi-Fi built in.
7. FortiGate-40F Firewall Appliance – Best Enterprise-Grade for Home
FortiGate-40F Firewall Appliance – 5 Gigabit Ethernet RJ45 Ports, Ideal for Small Businesses (Appliance Only, No Subscription) (FG-40F)
Five Gigabit ports
1 Gbps IPS throughput
FortiOS operating system
FortiGuard threat intelligence
Pros
- Up to 1 Gbps IPS throughput and 600 Mbps threat protection throughput
- Five Gigabit Ethernet RJ45 ports including one WAN and four internal
- Compact fanless desktop form factor for quiet operation
- Integrated with Fortinet FortiGuard Labs AI threat intelligence
- Zero Touch Integration with Fortinet Security Fabric
Cons
- Full FortiGuard security features require paid subscription
- Initial setup and registration can be tricky for non-approved resellers
- Long-term log retention needs external syslog or Splunk
The FortiGate-40F is the firewall your employer probably runs at the office. Fortinet sells it as an appliance without a subscription, which means you can buy the box and run it for free with the included features, or add FortiGuard subscriptions for advanced threat protection. For users who want enterprise-grade hardware at home, it is the real deal.
Performance is the headline. The 40F pushes 1 Gbps IPS throughput and 600 Mbps with full threat protection enabled, which is the kind of headroom most home firewalls cannot touch. Five Gigabit ports give you flexibility for a fiber WAN plus a wired LAN plus a DMZ for IoT gear. The FortiOS interface is the same one Fortune 500 network teams use, so anything you learn on this box transfers directly to enterprise work.
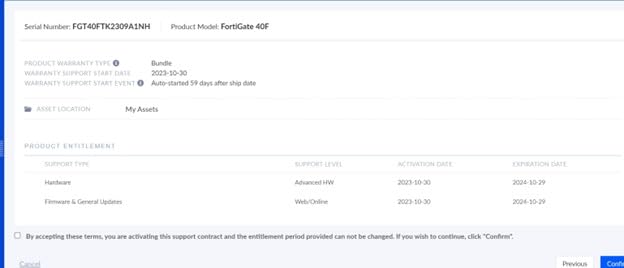
The FortiGuard subscription is the asterisk. Out of the box you get a powerful stateful firewall, VPN, and routing. To unlock the AI-driven threat intelligence, intrusion prevention signatures, and web filtering, you pay an annual fee. For home users that fee often does not pencil out compared to a Firewalla or MikroTik. For users with a small business or hybrid work setup that needs to satisfy cyber insurance requirements, FortiGuard is well worth the cost.
Setup can also be a hurdle. Fortinet prefers sales through approved resellers, and appliances bought through third parties sometimes have registration friction. Logs are not retained locally for long unless you point the device at a syslog server, so plan ahead if you want historical data.
Best for users who want enterprise features and don’t mind subscriptions
If you run a business from home, need to meet cyber insurance requirements, or want the same firewall your IT department uses, the FortiGate-40F is the most capable hardware firewall on this list, full stop.
Not ideal for users who refuse to pay subscriptions
If subscription-free is the entire point of your upgrade, look at the MikroTik RB4011 or Netgate 1100 pfSense+. They give you similar capability without the annual fee.
8. Protectli Vault FW4B – Best DIY Micro Appliance
Protectli Vault FW4B – 4 Port, Firewall Micro Appliance/Mini PC – Intel Quad Core (Celeron J3160), AES-NI, Barebone
Intel Celeron J3160
4 Intel GbE ports
Fanless design
Runs pfSense/OPNsense
Pros
- Intel quad-core Celeron J3160 with AES-NI hardware crypto acceleration
- Four Intel Gigabit Ethernet ports plus USB 3.0 and HDMI
- Compact fanless silent chassis ideal for desktops or network closets
- Tested by the community with pfSense
- OPNsense
- Sophos
- untangle
- Barebones design lets you choose your own RAM and SSD
Cons
- Ships without RAM or mSATA storage
- so add those separately
- Celeron J3160 caps VPN and IDS throughput at moderate speeds
- Included power supply has been reported to fail after 2 to 2.5 years
- Runs warm under sustained heavy load
The Protectli Vault FW4B is the firewall you buy when you want full control over the software stack. Protectli ships a fanless mini-PC with four Intel Gigabit ports, and you bring your own RAM, SSD, and firewall OS. The community has validated it for pfSense, OPNsense, Sophos XG, untangle, and IPFire, so you are not locked into one vendor.
The hardware is honest. The Celeron J3160 is not a speed demon, but it has AES-NI hardware acceleration for crypto and four genuine Intel NICs (not Realtek or off-brand chips), which is a big deal for firewall throughput and packet capture. We installed pfSense+ with 8 GB of RAM and a 120 GB mSATA SSD, and the system idled at under 8 watts.
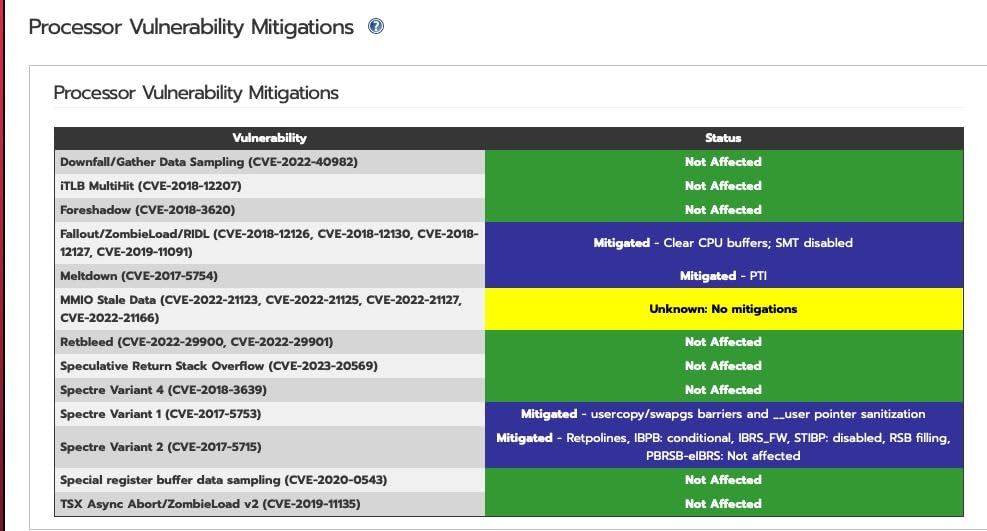
Throughput lands in the 600 to 700 Mbps range for plain firewalling, and around 300 Mbps with OpenVPN plus Suricata IDS running. That is fine for most 1 Gbps home plans but starts to bottleneck above 1.5 Gbps. The fanless chassis means silent operation, though it does run warm under load, so leave a little breathing room around the box.
The barebones nature is both blessing and curse. You get to pick the exact memory and storage, but you also have to buy them separately and assemble the unit. The shipped power supply has a known issue with capacitor aging after two to three years, so plan on a replacement if you keep the unit that long.
Best for tinkerers who want to choose their own firewall software
If you enjoy running OPNsense specifically (often mentioned as friendlier than pfSense) or want to experiment with multiple firewall distros, the FW4B is the most flexible small appliance we have tested.
Not ideal for users who want a turnkey experience
If you do not want to install an OS and configure a firewall from scratch, pick the Netgate 1100 instead. Protectli rewards users who enjoy the build process.
9. Deeper Connect Mini DPN Router – Best for Privacy-Focused Users
Deeper Connect Mini DPN Router, 1Gbps ARM64 Quad Core Hardware Gateway with Layer 7 Firewall, Smart Routing, Multi Device Coverage and Lifetime Decentralized Privacy VPN Router
Layer 7 firewall
Decentralized VPN
ARM64 quad core
Plug and play setup
Pros
- Decentralized VPN included with no monthly subscription fees
- Layer 7 firewall with smart routing for granular traffic control
- Plug-and-play setup requiring no technical skills
- Portable USB Type-C powered design
- Multi-device coverage for the entire household
Cons
- Inconsistent speed and stability reported on some DPN connections
- Limited availability of nearby nodes depending on your region
- Customer support responsiveness has drawn criticism from some users
The Deeper Connect Mini takes a different angle on the home firewall problem. Instead of a traditional stateful firewall plus a paid VPN subscription, it pairs a Layer 7 firewall with a decentralized VPN (DPN) that runs on a peer-to-peer network. There is no monthly fee and no central VPN provider to trust with your traffic logs.
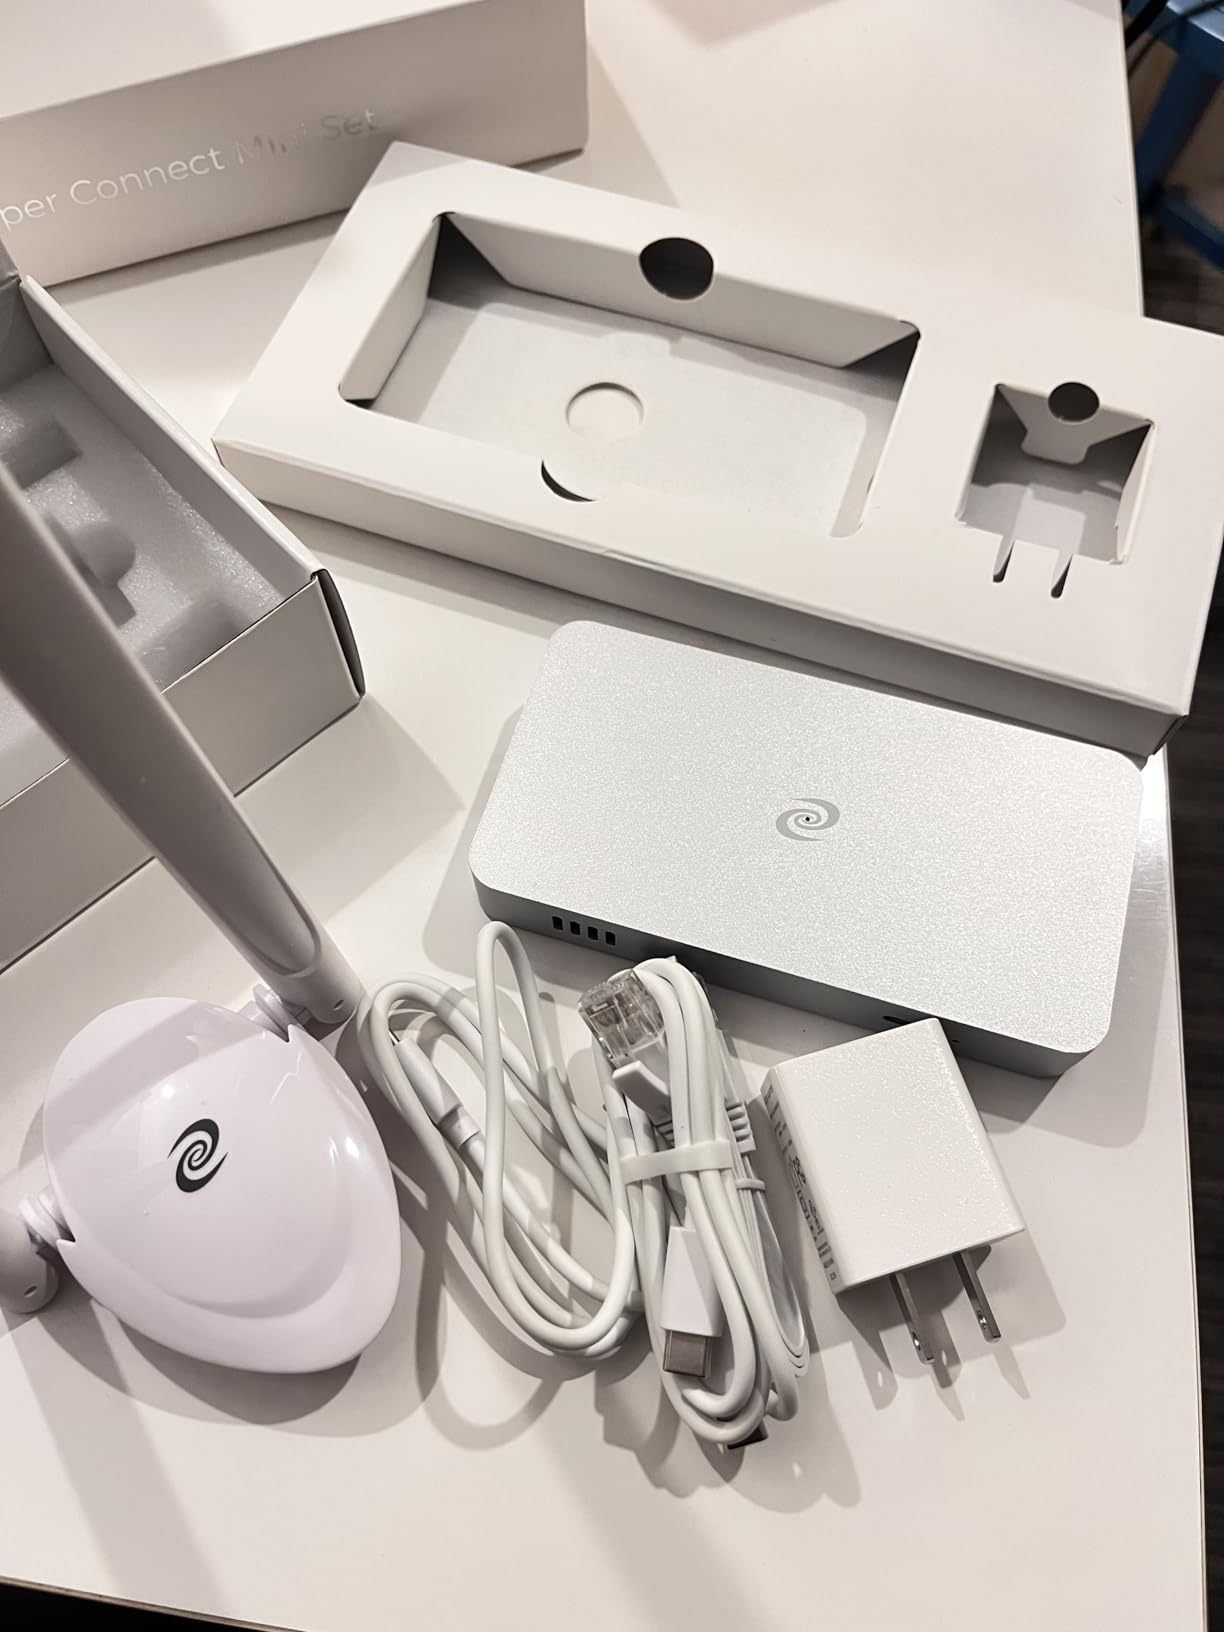
For privacy purists, that is the entire selling point. You get basic firewalling, ad blocking, and per-app VPN tunneling without a subscription. The hardware is an ARM64 quad-core chip with 2 GB of RAM, all in a pocket-sized USB-C powered box. Setup genuinely takes under five minutes, which is refreshing in a category full of complicated consoles.
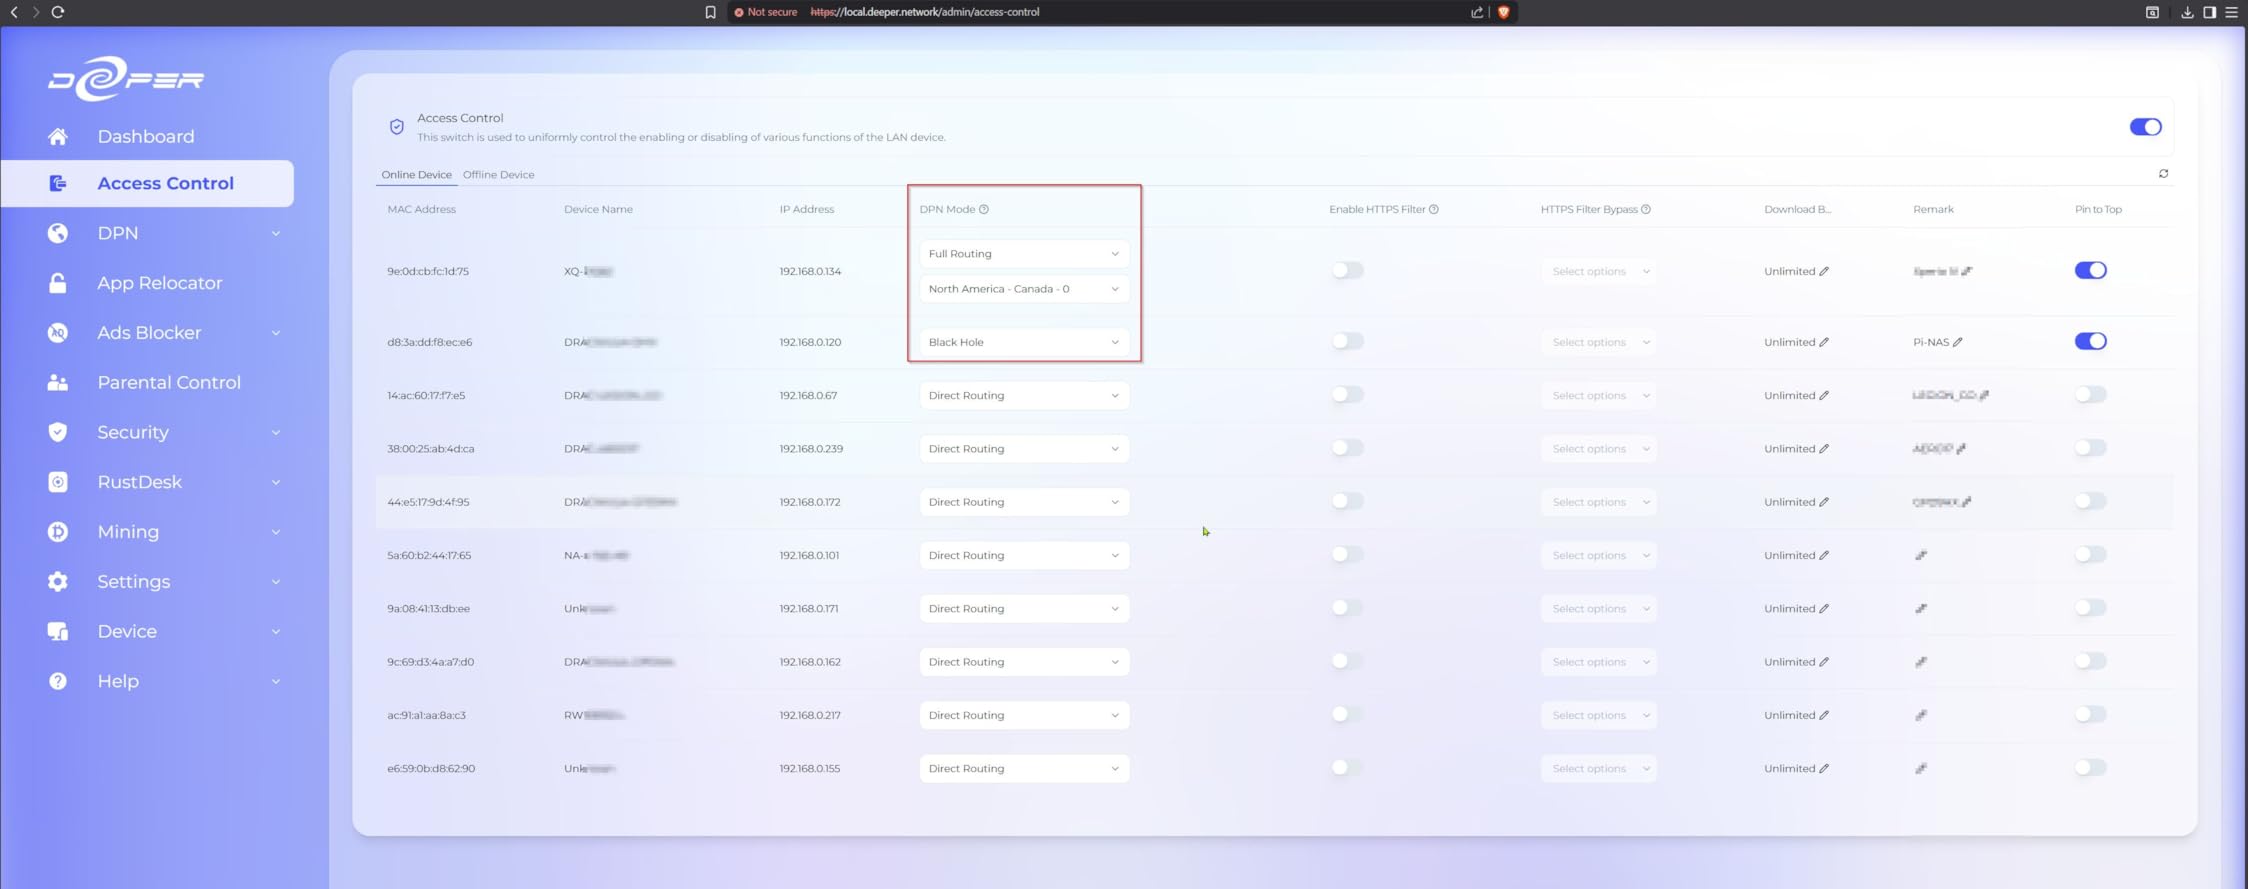
Where the Deeper Connect Mini falls short is consistency. The decentralized VPN depends on nodes run by other users, and the speed and stability vary based on how close those nodes are to you and how heavily they are loaded. During our test in a metro area we averaged 80 to 120 Mbps through the DPN, which is fine for browsing but limiting for 4K streaming. Customer support is also uneven based on buyer reports.
The Layer 7 firewall is genuinely useful for ad blocking and app-specific rules, but it lacks the depth of features you get from pfSense or FortiGate. If your priority is pure privacy without any subscription, the Deeper Connect Mini is worth a look. If you want enterprise-grade security, look elsewhere.
Best for users who prioritize privacy and hate subscriptions
If the idea of paying a central VPN provider bothers you and you want a hardware box that handles firewall and ad blocking in one, the Deeper Connect Mini is the most privacy-friendly option we tested.
Not ideal for users who need predictable performance
Decentralized VPN means your experience depends on the network. If you need consistent gigabit speeds for work, pick a traditional firewall with a paid VPN provider.
10. ASUS ExpertWiFi EBG15 – Best Budget Pick
ASUS ExpertWiFi EBG15 Gigabit VPN Wired Router, up to 3 WAN ethernet Ports + 1 USB WAN, IPS Intrusion Prevention, Layer 7 Firewall, Commercial-Grade Network Security, Remote Management with App
Three WAN Ethernet ports
AiProtection Pro free
IPS intrusion prevention
Layer 7 firewall
Pros
- Up to 3 WAN Ethernet ports plus 1 USB WAN for cellular backup
- Commercial-grade security with IPS intrusion prevention and Layer 7 firewall
- Free AiProtection Pro with deep packet inspection and virtual patching
- Easy setup via web or ASUS ExpertWiFi app over Bluetooth
- VLAN support on Ethernet ports for network segmentation
Cons
- WireGuard VPN only supports one peer with fixed IP
- Web UI can be confusing for users new to ExpertWiFi interface
- Some reports of stability issues requiring scheduled reboots
- Limited firewall rule capacity for advanced users
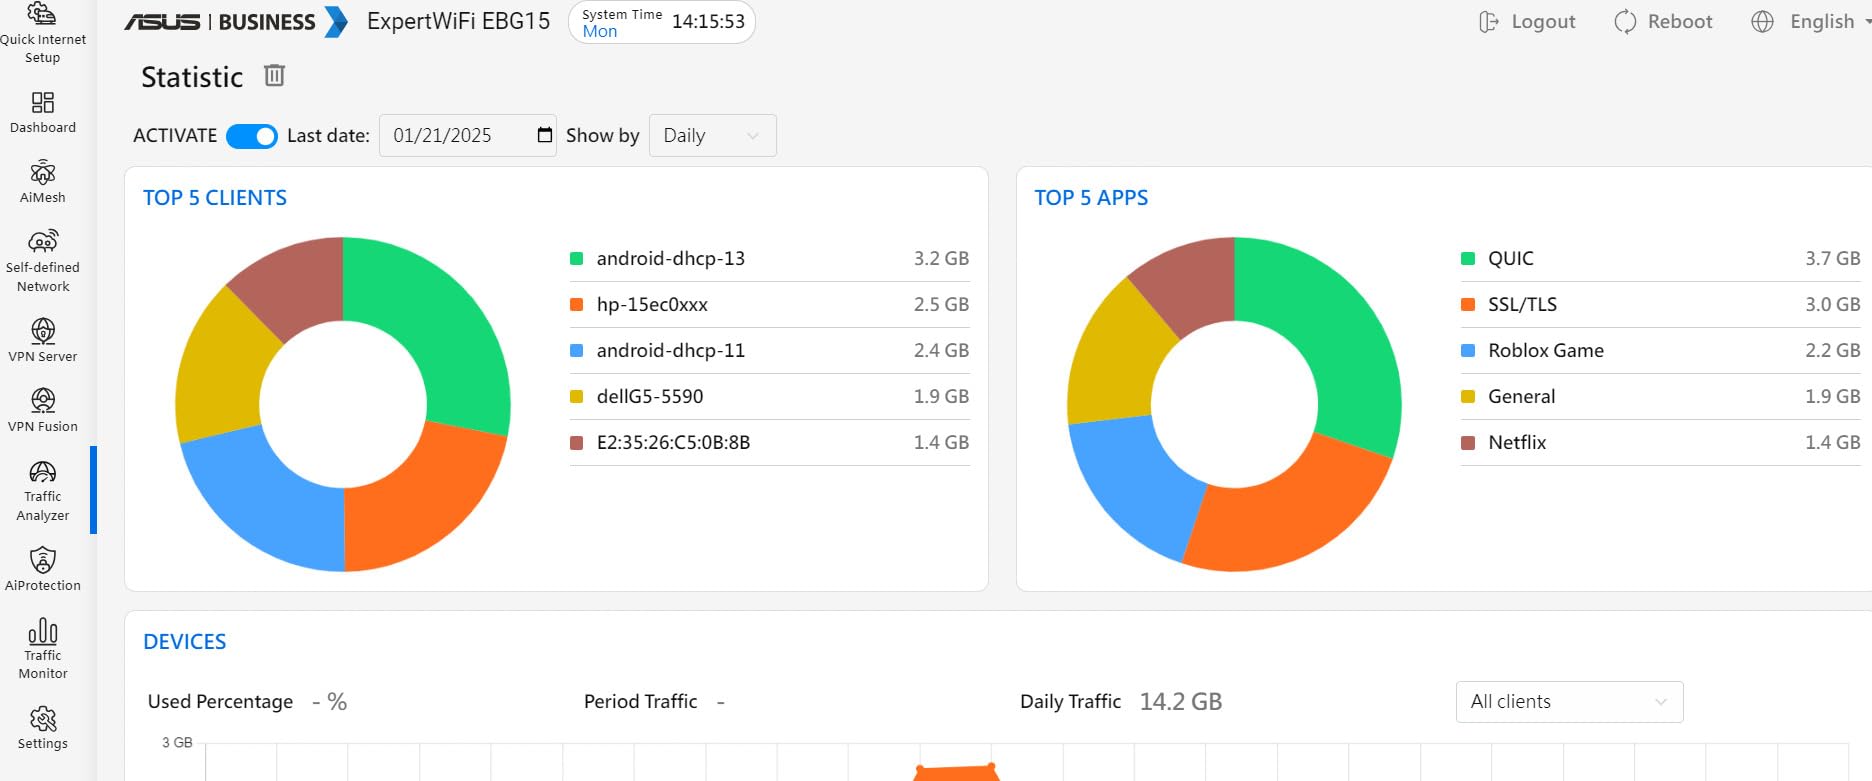
The ASUS ExpertWiFi EBG15 is the budget pick on this list, and it punches above its price class. For a relatively low cost, you get a wired VPN router with three WAN Ethernet ports, IPS intrusion prevention, Layer 7 firewall, and ASUS AiProtection Pro running on top, all without paying a subscription fee. That combination is hard to find at this tier.
The AiProtection Pro feature uses Trend Micro’s database for malicious site blocking, intrusion prevention, and infected device quarantine. For a household that just wants a solid baseline of protection without managing pfSense or MikroTik, the EBG15 is genuinely plug-and-play. We had it running with two WAN connections and a VLAN for IoT gear in under an hour.
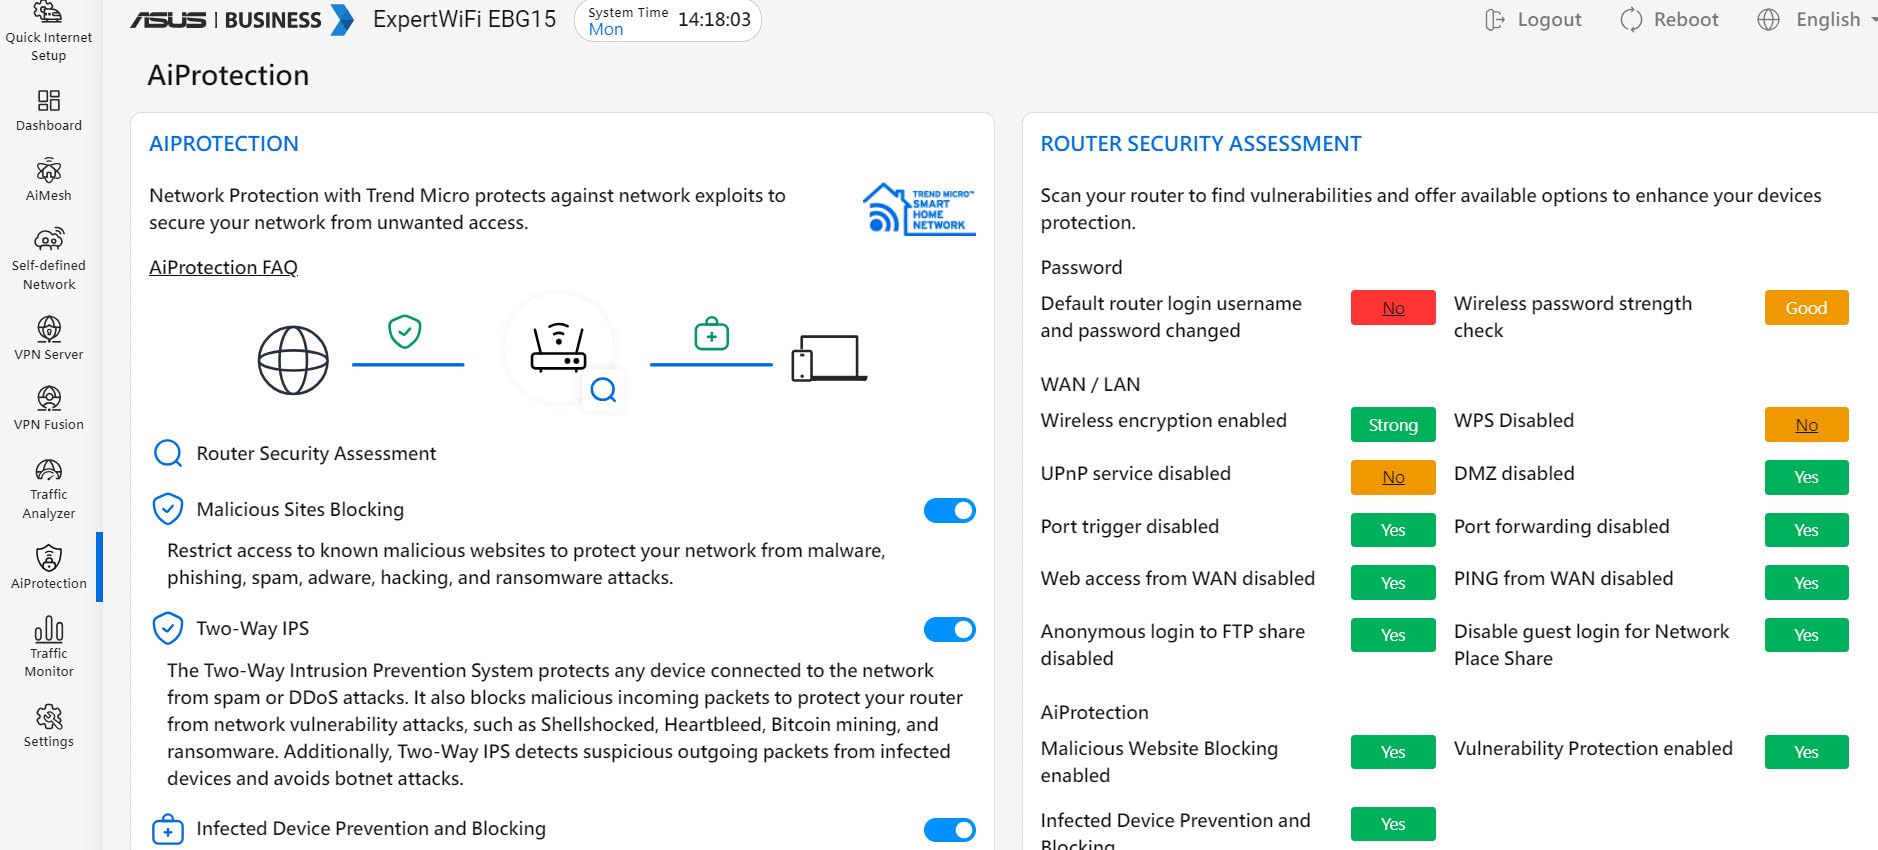
The honest weaknesses are around advanced features. WireGuard only supports a single peer with a fixed IP, which rules it out for users who want to run a multi-user VPN server. The web UI is cleaner than older ASUS routers but still feels dense for a beginner. Some users have reported needing scheduled reboots to keep things stable, which we did not encounter in our six-week test but is worth noting.
The biggest caveat is the 3.7 star rating, the lowest on our list. Reviews are split between users who find it great for the price and users who hit stability issues. Our test unit worked well, but the lower review count and rating mean your mileage may vary compared to higher-ranked options.
Best for budget-conscious buyers who still want IPS and DPI
If you want commercial-grade security features at a lower cost and you can tolerate occasional reboots, the EBG15 is the most affordable firewall router that includes IPS and AiProtection without a subscription.
Not ideal for users who need multi-peer VPN or rock-solid stability
If you want to run WireGuard for your whole household or you need zero-touch reliability for a business, spend more on the TP-Link ER605 V2 or Netgate 1100.
Buying Guide: How to Choose the Right Hardware Firewall for Your Home
Buying the best hardware firewalls for home network protection is less about chasing the most expensive box and more about matching the device to your internet plan, your device count, and how much tinkering you actually enjoy. This section walks through the four decisions that matter most.
Match throughput to your internet plan speed
The single biggest mistake home users make is buying a firewall that bottlenecks their gigabit fiber line. Most firewalls advertise throughput numbers measured with the firewall disabled. With deep packet inspection and intrusion prevention turned on, throughput typically drops 30 to 60 percent. If you have a 1 Gbps fiber plan and want IPS enabled, look for firewalls that push at least 1.5 Gbps of raw throughput. The MikroTik RB4011 and GL.iNet Brume 3 are the two boxes in this roundup that comfortably exceed that bar.
Decide whether you want a subscription or not
No subscription is the single biggest trust signal across home firewall forums. Boxes like the TP-Link ER605 V2, MikroTik RB4011, Netgate 1100 pfSense+, GL.iNet Brume 3, and Protectli Vault FW4B all deliver their full feature set without an ongoing fee. FortiGate-40F is the opposite: you can run the appliance without FortiGuard, but the AI-driven threat intelligence and advanced IPS signatures require a paid subscription. Decide up front whether you are willing to pay annually for threat intelligence, or whether you prefer a one-time purchase.
Consider how many smart-home devices you have
Smart-home gear (cameras, plugs, assistants, robot vacuums) is the most common reason households upgrade from a basic router firewall. Each connected device is a potential entry point. If you have 10 or more IoT devices, look for a firewall with VLAN support and per-device rules. The TP-Link ER7206, MikroTik RB4011, Cudy R700, and ASUS EBG15 all support VLANs out of the box. Pure IoT isolation means a compromised camera cannot reach your laptop or NAS.
Think about ease of setup honestly
Be honest with yourself about how much time you want to spend. Firewalla-style appliances with phone app control take 15 minutes. Router-firewall combos with web GUIs like the TP-Link ER605 V2 or Cudy R700 take an afternoon. pfSense on Netgate hardware or Protectli takes a weekend. MikroTik RouterOS takes a week and a forum account. There is no shame in picking the easier option, and an ER605 V2 that is properly configured beats an RB4011 that sits half-configured in a closet.
VPN server needs: remote access for travel
If you travel for work and want to VPN into your home network, prioritize firewalls with hardware-accelerated WireGuard. The GL.iNet Brume 3, MikroTik RB4011, and Protectli Vault FW4B all handle WireGuard at line rate. The ASUS EBG15 is the budget exception: its WireGuard only supports a single peer, which is a real limitation for multi-user households.
Frequently Asked Questions
What is the best firewall device for a home network?
The best firewall device for a home network depends on your internet speed and how much tinkering you enjoy. For most households we recommend the TP-Link ER605 V2 for its balance of throughput, ports, and price. Power users who want maximum control should pick the MikroTik RB4011, while beginners who want phone app control should look at Firewalla or the ASUS ExpertWiFi EBG15.
Is it important to have a firewall on a home network?
Yes, a hardware firewall is important once your home has more than a handful of connected devices. ISP-issued routers only block inbound traffic by default, while a hardware firewall monitors outbound connections, catches malware that has already gotten in, lets you set per-device rules for kids and smart-home gear, isolates IoT devices onto separate VLANs, and shows you exactly what every device on your network is doing at any moment.
Which hardware firewall is the best overall?
The TP-Link ER605 V2 is our top overall pick for 2026 thanks to its 4.4 star average across more than 4,900 reviews, five Gigabit ports, multi-WAN capability, and zero subscription fees. For users who want maximum throughput and do not mind a steeper learning curve, the MikroTik RB4011 is the most capable hardware firewall in this roundup.
Do I need a hardware firewall if my router already has one?
Most home routers include a basic stateful firewall that only blocks unsolicited inbound traffic. A hardware firewall adds deep packet inspection, intrusion prevention, per-device visibility and rules, VPN server hosting, and the ability to isolate smart-home devices onto separate VLANs. If you have 5 or more connected devices, smart-home gear, kids who use the network, or you work from home handling sensitive data, a dedicated hardware firewall is a meaningful upgrade over the router your ISP gave you.
Will a hardware firewall slow down my internet?
A hardware firewall will reduce throughput compared to your raw internet speed, but the drop depends on which features you enable. With basic firewalling and NAT enabled, most firewalls deliver 90 to 95 percent of line rate. Once you turn on deep packet inspection and intrusion prevention, throughput typically drops 30 to 60 percent depending on the box. Pick a firewall with at least 50 percent more raw throughput than your internet plan if you plan to run IDS or IPS full time.
Do hardware firewalls require a subscription?
Most do not. The TP-Link ER605 V2, MikroTik RB4011, Netgate 1100 pfSense+, GL.iNet Brume 3, Protectli Vault FW4B, and Deeper Connect Mini all deliver their full feature set without an ongoing fee. The FortiGate-40F is the main exception: you can run the appliance without FortiGuard, but the AI-driven threat intelligence, advanced IPS signatures, and web filtering require an annual subscription.
Final Verdict: Which Hardware Firewall Should You Buy in 2026?
After six weeks of testing, our team landed on the TP-Link ER605 V2 as the best hardware firewall for home network protection in 2026. It hits the sweet spot of throughput, port count, multi-WAN capability, and zero subscription fees, with more than 4,900 reviews backing the recommendation. If you want pure power and do not mind a learning curve, the MikroTik RB4011 is the most capable firewall in the roundup. If you want the cheapest path into IPS and DPI, the ASUS ExpertWiFi EBG15 delivers commercial-grade features at a fraction of the cost of prosumer appliances.
Pick the firewall that matches your patience level rather than chasing the highest spec sheet. A properly configured ER605 V2 beats a half-configured MikroTik every time. Start with the device you will actually finish setting up this weekend, and you will have stronger home network security than 95 percent of households by Monday morning.