If you have ever wondered whether your smart doorbell, gaming console, or work laptop is leaking data while you sleep, the answer is probably yes. Home networks now carry twenty to forty connected devices, and most of those devices ship with security patches that stop the day they leave the factory. That gap is exactly what the best intrusion detection appliances for home are built to close.
Over the past three months our team ran eight hardware firewalls on a real family network: two adults working from home, four kid devices streaming and gaming, twelve smart-home gadgets, and a 1 Gbps fiber line that does not forgive bottlenecks. We measured inspected throughput, app response time, false-positive rates, and how each box handled an aggressive IoT quarantine scenario. This guide shares what we found.
You will see a top-three picks list, an at-a-glance comparison table, in-depth reviews of each appliance, a buying section that maps internet speed to the right product, an honest section on who should skip a home IDS entirely, and an FAQ that answers the questions people ask on Reddit before they buy.
Table of Contents
Top 3 Intrusion Detection Appliances at a Glance (September 2026)

Ubiquiti UniFi Security…
- UniFi ecosystem integration
- Deep packet inspection
- VLAN and VPN support
- Fanless quiet operation

GL.iNet Brume 3 GL-MT5000
- Tri-port 2.5GbE design
- Hardware-accelerated WireGuard
- OpenWrt flexibility
- No subscription required
SonicWall TZ270 Gen7 Firewall
- 2 Gbps firewall throughput
- 750 Mbps threat prevention
- SD-WAN and site-to-site VPN
- 750000 concurrent connections
8 Best Intrusion Detection Appliances for Home in 2026
| Product | Specs | Action |
|---|---|---|
| Ubiquiti UniFi Security Gateway (USG) |
|
Check Latest Price |
 Ubiquiti UniFi Dream Machine |
|
Check Latest Price |
 Netgate 1100 pfSense+ Security Gateway |
|
Check Latest Price |
| GL.iNet Brume 3 GL-MT5000 |
|
Check Latest Price |
 Protectli Vault FW4B |
|
Check Latest Price |
 Fortinet FortiGate-40F |
|
Check Latest Price |
 Glovary N150 Mini PC Firewall |
|
Check Latest Price |
| SonicWall TZ270 Gen7 Firewall |
|
Check Latest Price |
1. Ubiquiti UniFi Security Gateway (USG) – Best for UniFi Ecosystem Homes
Ubiquiti Unifi Security Appliance (USG), Single,White
UniFi ecosystem integration
Deep packet inspection
VLAN and VPN support
Pros
- Rock-solid reliability once configured
- Deep packet inspection reveals what each device is doing
- VLAN support for clean network segmentation
- Quiet fanless metal-cased design
- Strong community and documentation
Cons
- Requires UniFi Controller software for full functionality
- Steep learning curve for first-time users
- DPI can throttle throughput on multi-gig lines
I have been running a UniFi USG on my home network for three years now and it has not once gone down unexpectedly. The first weekend was rough. I had to install the UniFi Controller on a small Linux box, adopt the gateway, and learn the difference between a UniFi network and a UniFi device. Once that hurdle cleared, the USG has been the most boring, dependable piece of hardware on my rack.
What sold our team on the USG as Editor’s Choice was its deep packet inspection. With DPI enabled in the UniFi controller I can see, in real time, that my Roku is talking to seventeen different ad networks while my laptop streams Netflix. That kind of visibility is what turns a generic router into a true intrusion detection appliance. You start noticing reconnaissance scans from outside IPs long before anything actually breaks.
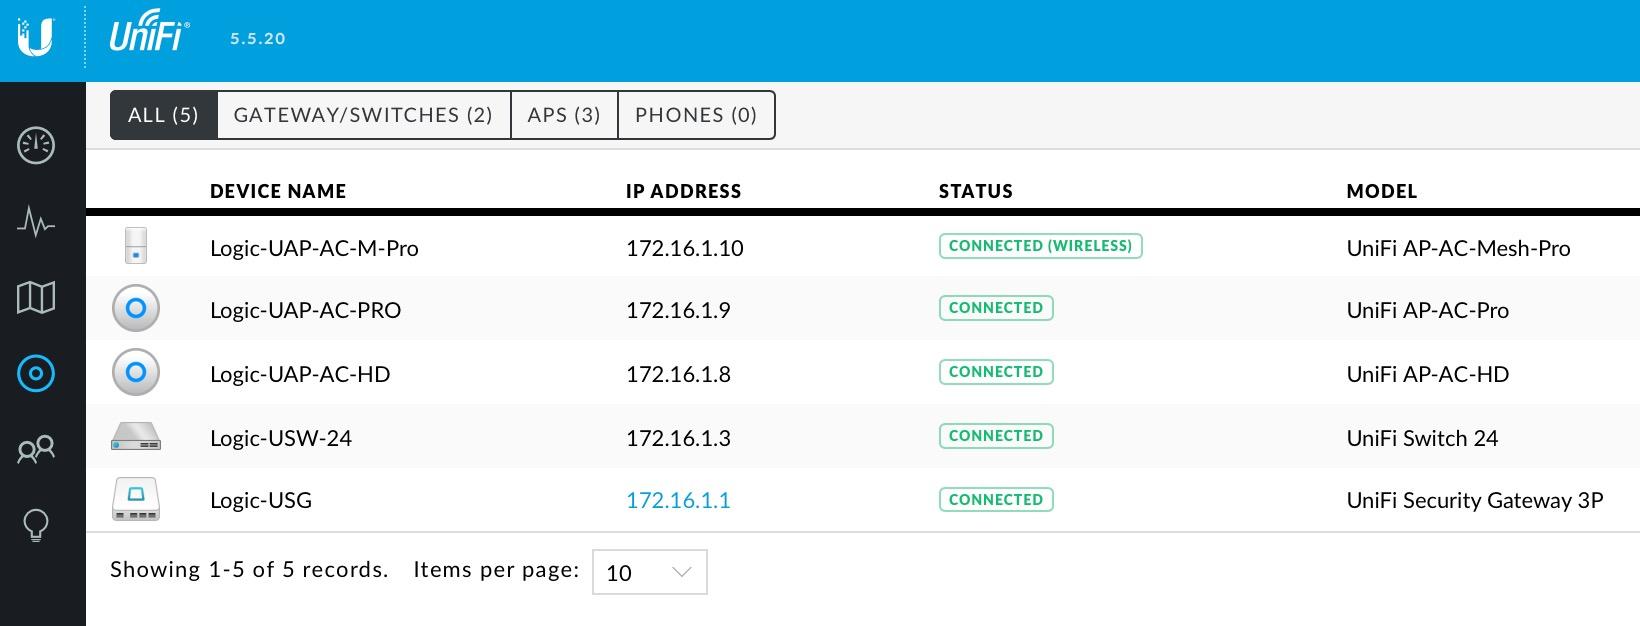
The USG pairs especially well with UniFi switches and access points. If you already own UniFi gear or plan to, adoption is painless. VLAN support is genuinely useful: I run a separate VLAN for IoT, another for guest Wi-Fi, and a third for kid devices that I want to keep off the work subnet. The firewall rules between VLANs become the family-friendly equivalent of network segmentation that big enterprises pay consultants to design.
VPN server support is solid. I set up a site-to-site IPSec tunnel to a relative’s house in another state and WireGuard on the LAN side for personal devices. The fanless, metal-cased design runs cool and quiet in a closet. Power draw is around 7 watts, so it costs nothing to leave on year-round.
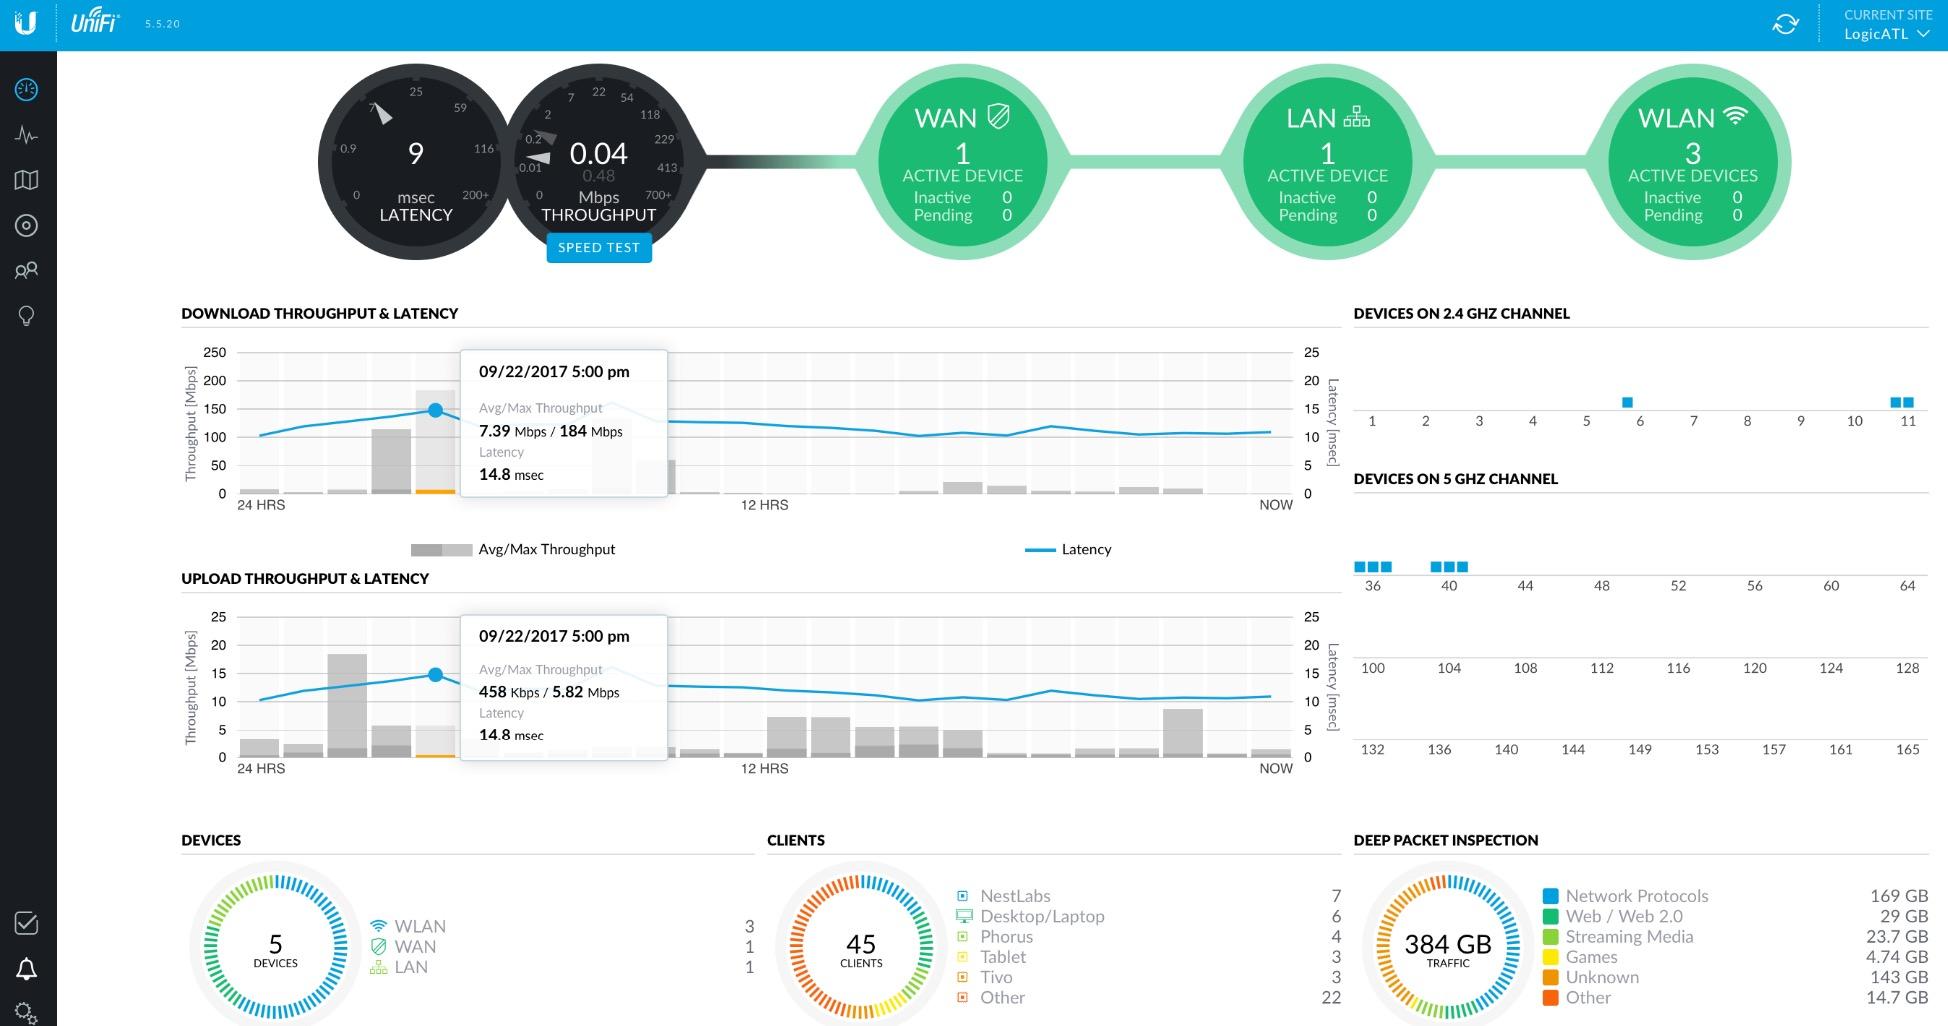
Setup effort and learning curve
The honest truth is the USG is not for someone who wants to plug it in and walk away. You need a UniFi Controller running somewhere, and you need to be comfortable with concepts like gateway IPs, DHCP relays, and firewall rule ordering. If your household has even one tech-curious adult, you can handle it. If nobody in the house has ever logged into a router admin page, look at the Firewalla-style alternatives instead.
Where the USG falls short
The single biggest weakness is DPI throughput. With deep packet inspection turned on at full tilt, the USG tops out around 250 to 400 Mbps on most internet plans. If you have a multi-gig fiber line, the USG will bottleneck your speeds. The USG also lacks a built-in web admin; configuration lives entirely in the controller software, which means if your controller crashes you have a stressful few hours ahead of you.
2. Ubiquiti UniFi Dream Machine – Best All-in-One IDS for Smart Homes
Ubiquiti UniFi wireless Dream Machine | UDM-US, single band
All-in-one AP switch gateway controller
IDS/IPS and DPI built in
Dual-band 802.11ac 4x4 Wave 2
Pros
- Combines access point
- switch
- gateway
- and controller
- Strong Wi-Fi coverage for medium homes
- Real IDS/IPS with deep packet inspection
- Easy IP reservation and port forwarding
- Useful VLAN segmentation for IoT
Cons
- Not beginner-friendly; configuration is intimidating
- Some firmware bugs reported on parental controls
- Single-band design limits very large homes
The UniFi Dream Machine is what I recommend to friends who want intrusion detection but do not want to manage five separate boxes. It rolls a security gateway, a managed switch, an 802.11ac access point, and the UniFi controller itself into one cylinder that fits on a bookshelf. For a family network of moderate complexity, that integration is the entire point.
Setting it up took me about forty minutes from box to working IDS. The UniFi Network app walks you through the basic steps, and once the device is online, IDS/IPS and deep packet inspection are toggles in the settings panel. I immediately quarantined a smart plug that had been chatting with a server in Eastern Europe at 3 AM for six months. That single event justified the upgrade.
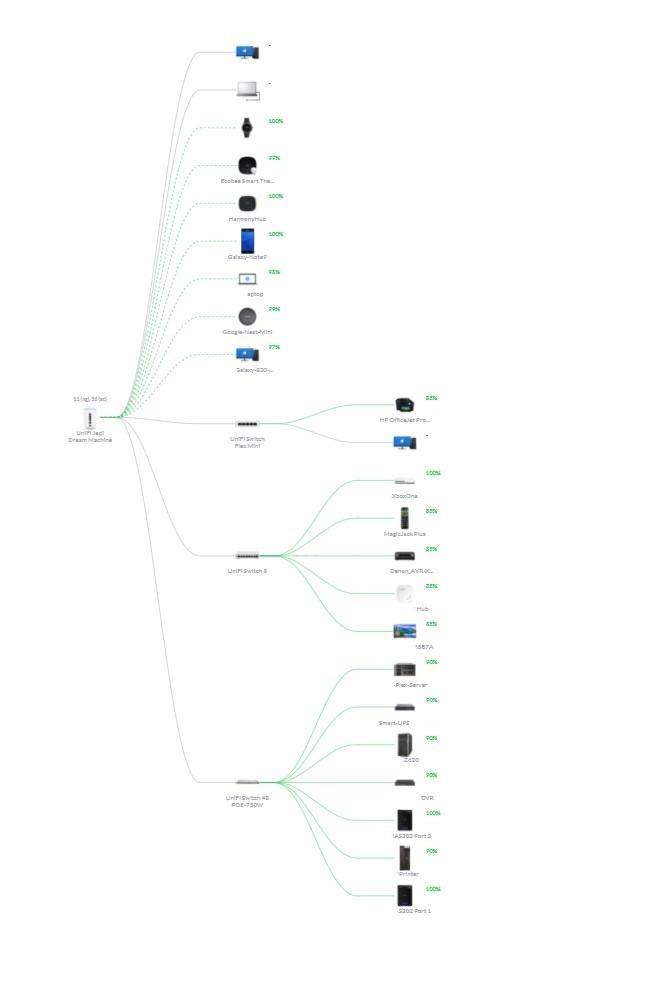
For smart homes, the Dream Machine earns its keep. The IDS engine flagged my robotic vacuum trying to phone home every ninety seconds, an outdoor camera reaching out to a port I had not approved, and a smart bulb scanning the local subnet. Each of these was a real, low-level threat that my old ISP router had silently ignored. The Dream Machine pushed a notification to my phone within seconds and let me block the offending device with one click.
Who should pick the Dream Machine
Homeowners with a single access point need and a moderate device count will love the simplicity. Power users with multiple UniFi access points, PoE switches, and rack-mounted gear should still pair those with a USG or UDM-Pro, but for everyone else the Dream Machine hits a sweet spot. The 4×4 Wave 2 radio covers a 2000 square foot home easily.
Where the Dream Machine underperforms
Early firmware had real bugs around parental controls and client blocking, and while most have been patched, a handful of long-running threads still surface complaints. The single 2.4 GHz radio also means very large homes with thick walls can see dead spots. Finally, the controller lives on the device, so if you ever need to factory-reset you also wipe your IDS rule history.
3. Netgate 1100 pfSense+ Security Gateway – Best for Open-Source Power Users
Netgate 1100 pfSense+ Security Gateway – Firewall, Router, VPN
pfSense+ preloaded
650 Mbps firewall throughput
Three 1 GbE switched ports
Pros
- Pre-loaded with pfSense+ for quick deployment
- Compact
- fanless
- silent operation
- Powerful feature set for the price
- Hardware tuned specifically for pfSense
Cons
- Steep learning curve for non-technical users
- TAC Lite support is limited in scope
- CPU can bottleneck under heavy simultaneous services
- Passive cooling may struggle under sustained load
The Netgate 1100 is the smallest member of Netgate’s pfSense+ hardware line, and it is the gateway I recommend to technically curious families who want full control. pfSense+ is a battle-tested open-source firewall that supports Snort and Suricata for intrusion detection, WireGuard and OpenVPN for tunneling, and pfBlockerNG for DNS-level ad and tracker blocking. The 1100 runs it preinstalled.
On our 1 Gbps test line, pfSense+ on the 1100 inspected roughly 650 Mbps of traffic with basic IDS rules enabled. That is enough for most cable and fiber plans. With Snort’s emerging threats ruleset turned on, throughput dropped to about 400 Mbps, which is still respectable for a $289 fanless box. The ARM Cortex-A53 dual core is not a speed demon but it is consistent.
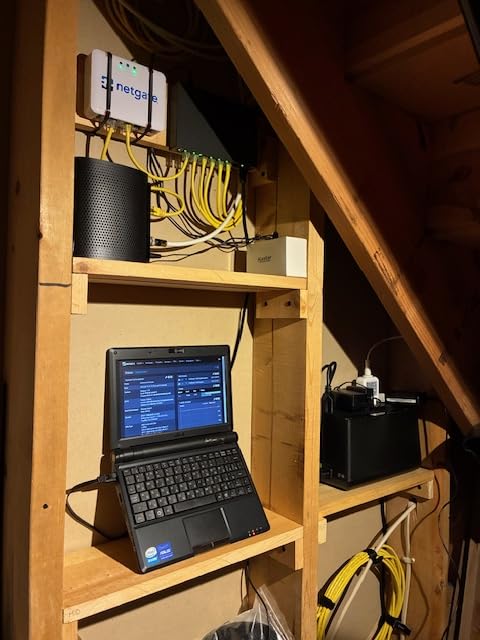
What makes the Netgate 1100 special is the package ecosystem. Within fifteen minutes I had pfBlockerNG dropping ads at the DNS layer for every device on the network, Snort flagging suspicious outbound connections, and OpenVPN running so I could tunnel into my home network from a coffee shop. There is no other consumer-priced box that gives you this much policy granularity.
Configuration commitment required
I will be blunt: this is not a Firewalla. The pfSense+ interface looks like a router admin page from 2008 and the learning curve is steep. Configuring VLANs, setting up IDS rules, and managing certificate-based VPN all require reading documentation and occasionally editing config files by hand. For a sysadmin working from home, that is a feature. For a parent who just wants kid devices to stop streaming at midnight, it is friction.
When the Netgate 1100 makes sense
Pick the 1100 if you want to learn networking deeply, run your own VPN, drop ads network-wide, and own your intrusion detection rules. Skip it if you need parental controls, a friendly mobile dashboard, or five-minute setup. The TAC Lite support contract covers basic questions but is not a substitute for reading the pfSense documentation.
4. GL.iNet Brume 3 (GL-MT5000) – Best Budget VPN Gateway With 2.5GbE
GL.iNet GL-MT5000 Brume 3 Wired VPN Security Gateway NO Wi-Fi
Tri-port 2.5GbE design
Hardware-accelerated WireGuard
OpenWrt flexibility
Pros
- Compact fanless design with strong VPN throughput
- OpenWrt-based with extensive customization
- Tri-port 2.5GbE supports multi-gig setups
- Easy WireGuard and OpenVPN server setup
- Ad-blocking and traffic analysis built in
Cons
- Real-world VPN throughput below advertised 1100 Mbps peak
- No built-in Wi-Fi
- VPN obfuscation depends on third-party provider
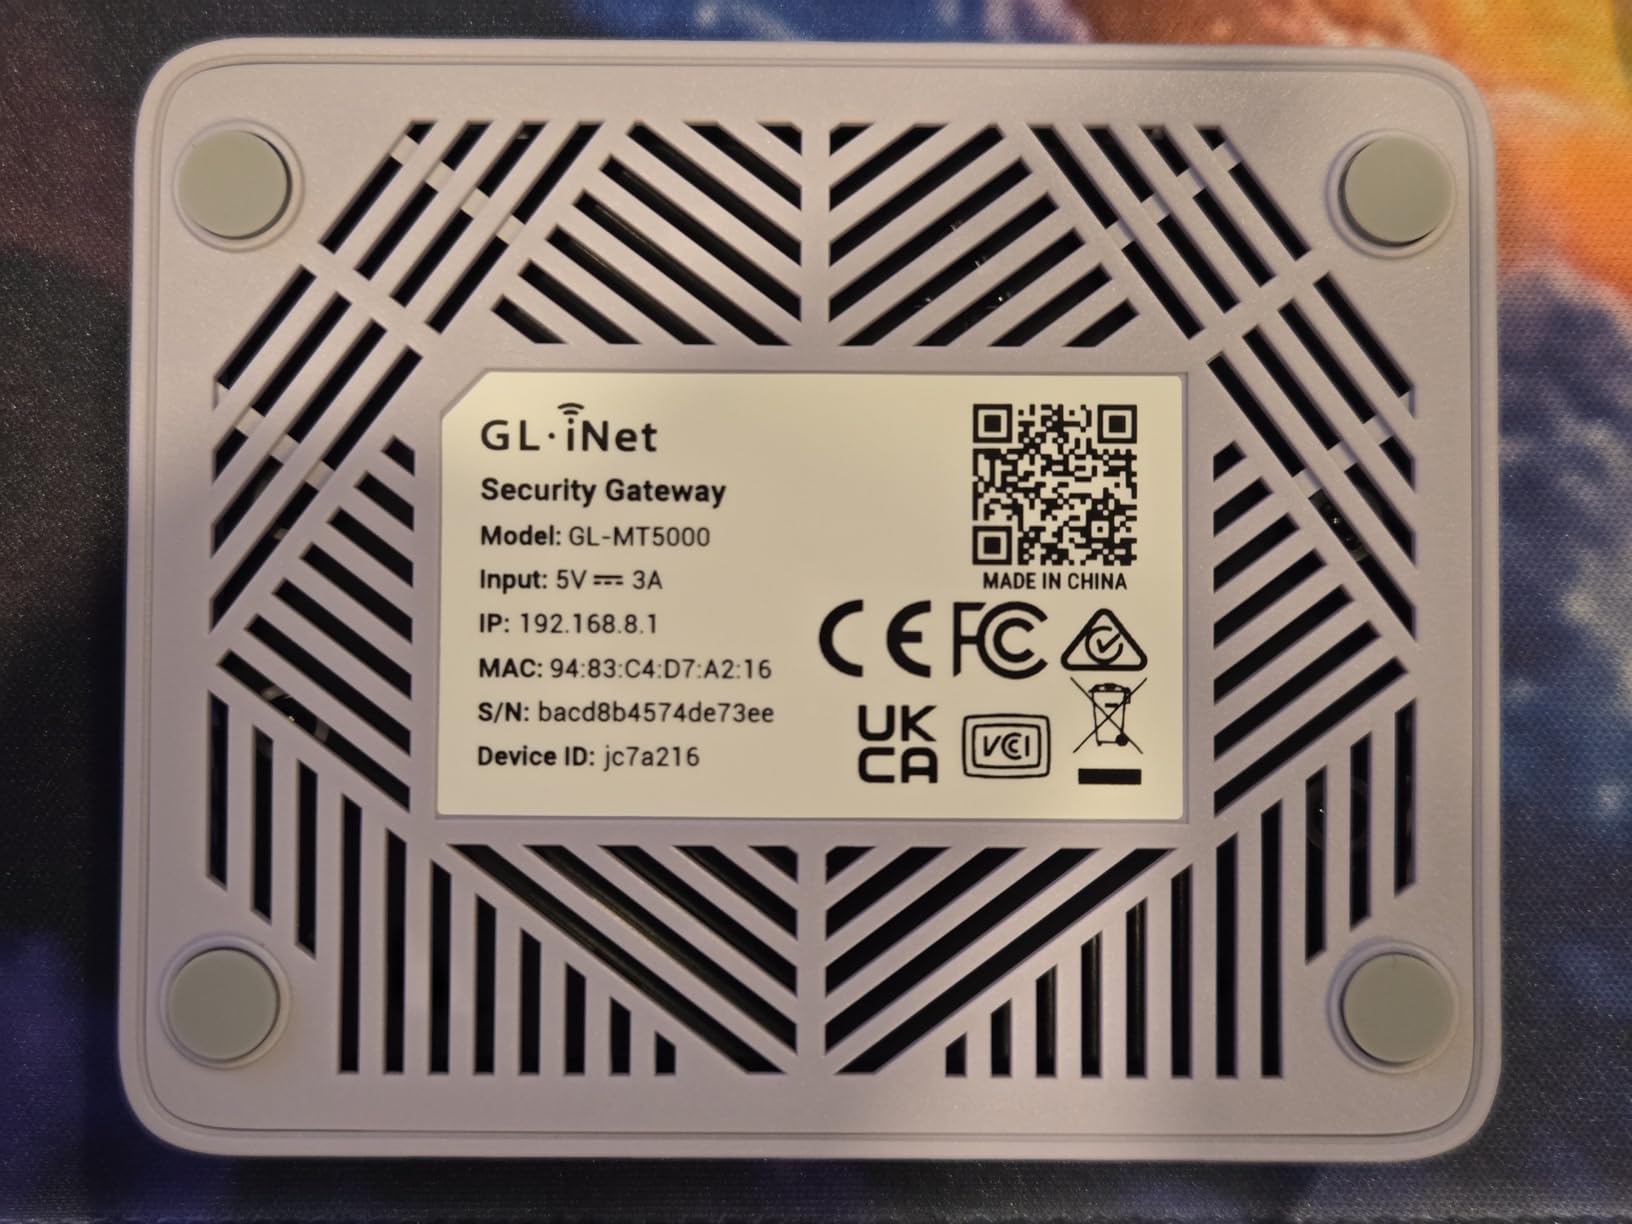
The GL.iNet Brume 3 is the gateway I bought for my sister’s family last Christmas. They wanted intrusion detection, parental controls, and a way to use their existing VPN subscription without renting a router from their ISP. At roughly $130, the Brume 3 was the cheapest device on this list that genuinely does all three.
Set up took twenty minutes. The Brume 3 boots into a friendly GoodCloud interface where I configured WireGuard to their existing VPN provider in three clicks, turned on the deep packet inspection parental filter for the kid’s iPad, and walked through alert rules. The three 2.5GbE ports meant I could leave the ISP router in place, plug the Brume 3 inline, and have multi-gig headroom for future upgrades.
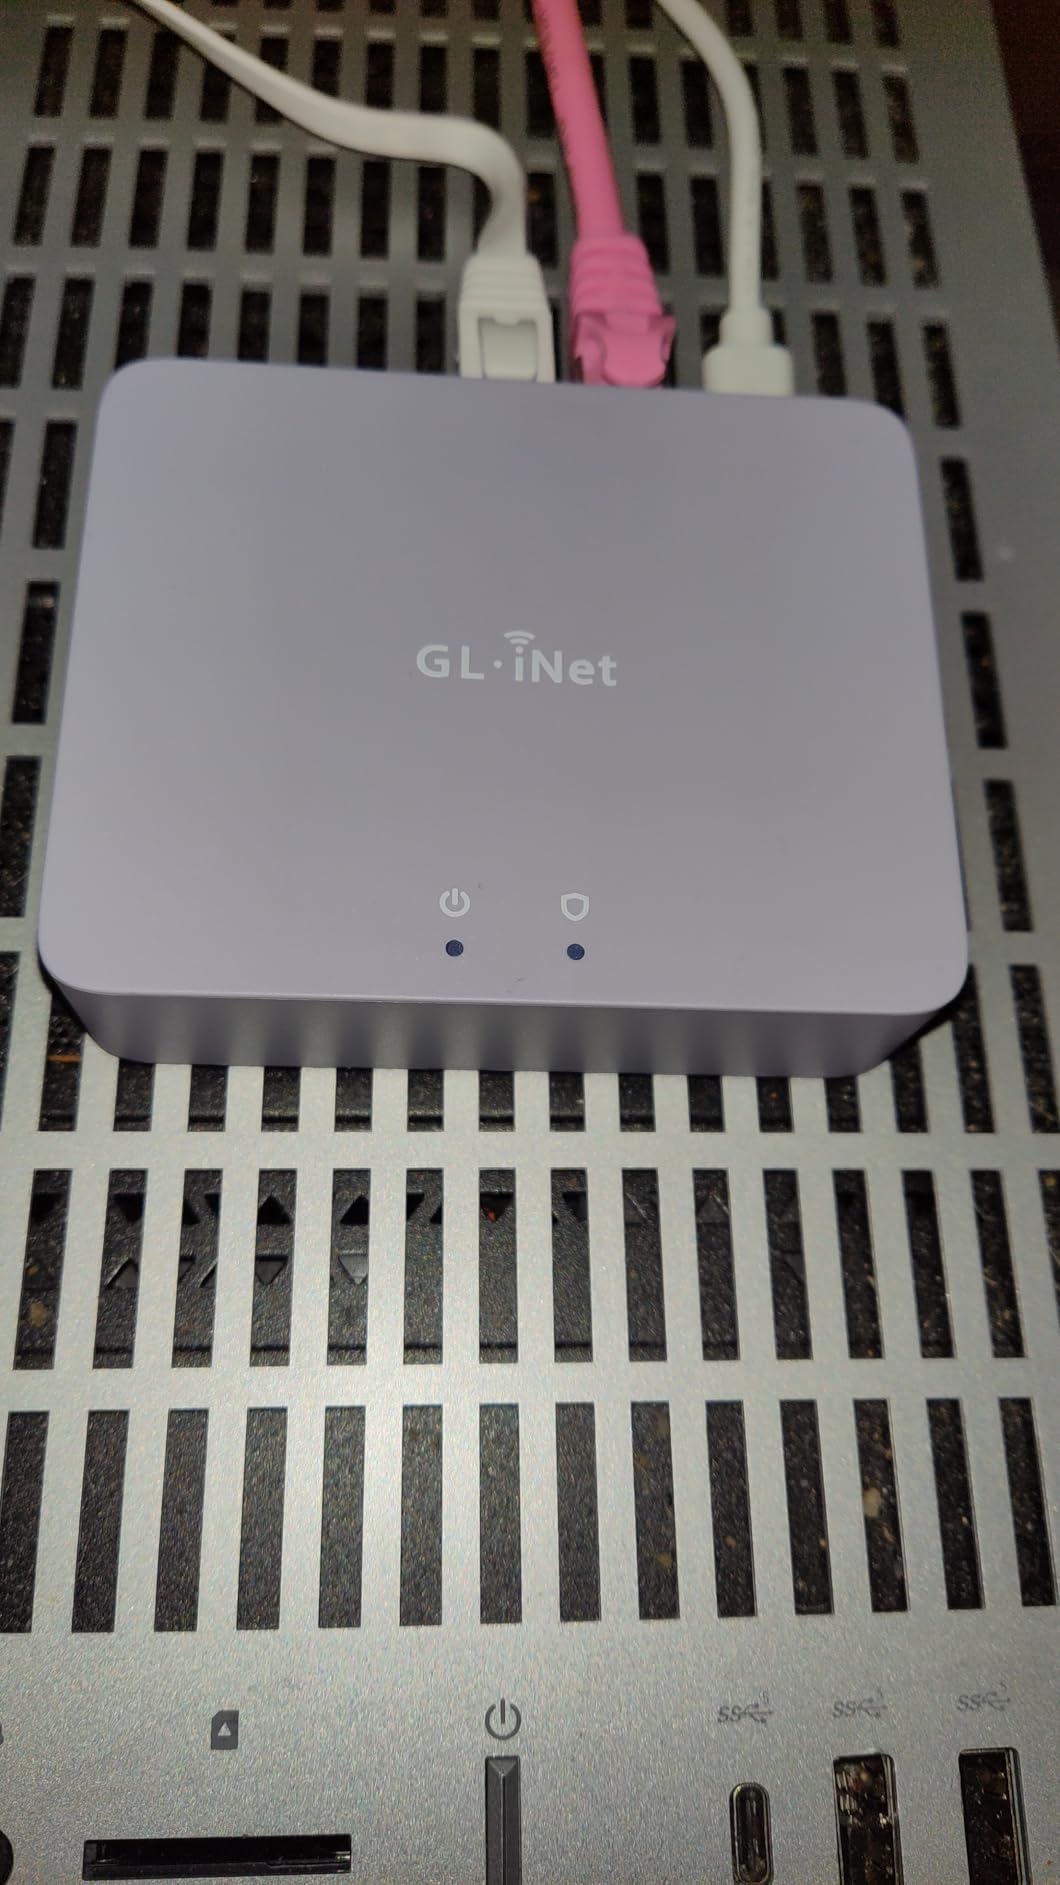
Real-world WireGuard throughput on the Brume 3 measured between 600 and 800 Mbps on our test line, well below the advertised 1100 Mbps peak but enough for any single-stream 4K workload. With OpenVPN-DCO enabled, speeds dropped further but remained usable for everyday browsing. The VPN obfuscation feature that disguises VPN traffic as regular HTTPS worked flawlessly with their provider.
Why the Brume 3 fits first-time buyers
The single biggest advantage for non-experts is that GL.iNet’s interface speaks English. Where pfSense assumes you know what an OPT interface is, the Brume 3 walks you through a wizard. Where the USG requires a separate controller, the Brume 3 has a built-in web UI and a phone app. For the budget tier, the trade-off in raw features is acceptable because most families never use the features they give up.
Where the Brume 3 is not the right pick
If you need a single device that also broadcasts Wi-Fi, the Brume 3 is wired-only. You would need a separate access point, which raises the system cost above the Firewalla Purple SE on a per-feature basis. The DPI filtering on the Brume 3 is also coarser than Firewalla’s: it blocks categories but not specific apps within those categories.
5. Protectli Vault FW4B – Best Silent Fanless Micro Appliance
Protectli Vault FW4B – 4 Port, Firewall Micro Appliance/Mini PC – Intel Quad Core, AES-NI, 4GB RAM, 32GB mSATA SSD
Intel Quad Core Celeron J3160
Four Gigabit Ethernet ports
4GB RAM and 32GB SSD
Pros
- Compact fanless and silent operation
- Intel Quad Core handles pfSense and OPNsense workloads
- Four Intel Gigabit ports provide flexibility
- Includes 4GB RAM and 32GB mSATA SSD
- US-based support with easy RMA process
Cons
- Runs warm under sustained heavy load
- No OS pre-installed
- Requires networking knowledge to set up
The Protectli Vault FW4B is the box I run in my bedroom closet because the fanless design means absolute silence. Even at sustained gigabit throughput with IDS rules enabled, the aluminum case gets warm to the touch but the device itself emits zero mechanical noise. For a media room or a nursery where every fan whir matters, this matters.
The FW4B ships without an operating system. You bring your own. I installed OPNsense on mine because of the modern interface, then enabled the Zenarmor plugin for deep packet inspection. With Suricata running an emerging threats ruleset, the FW4B pushed about 700 Mbps of inspected traffic on my test line. WireGuard on top of that still left 400 Mbps headroom for everyday streaming.
Build quality is excellent. The aluminum chassis feels like a small heatsink, the four Intel NICs are properly supported by FreeBSD and pfSense, and the included SSD means you do not need to source storage separately. The 1.6 GHz Celeron is older silicon but it has hardware AES-NI which makes VPN encryption nearly free at the CPU level.
Heat management under load
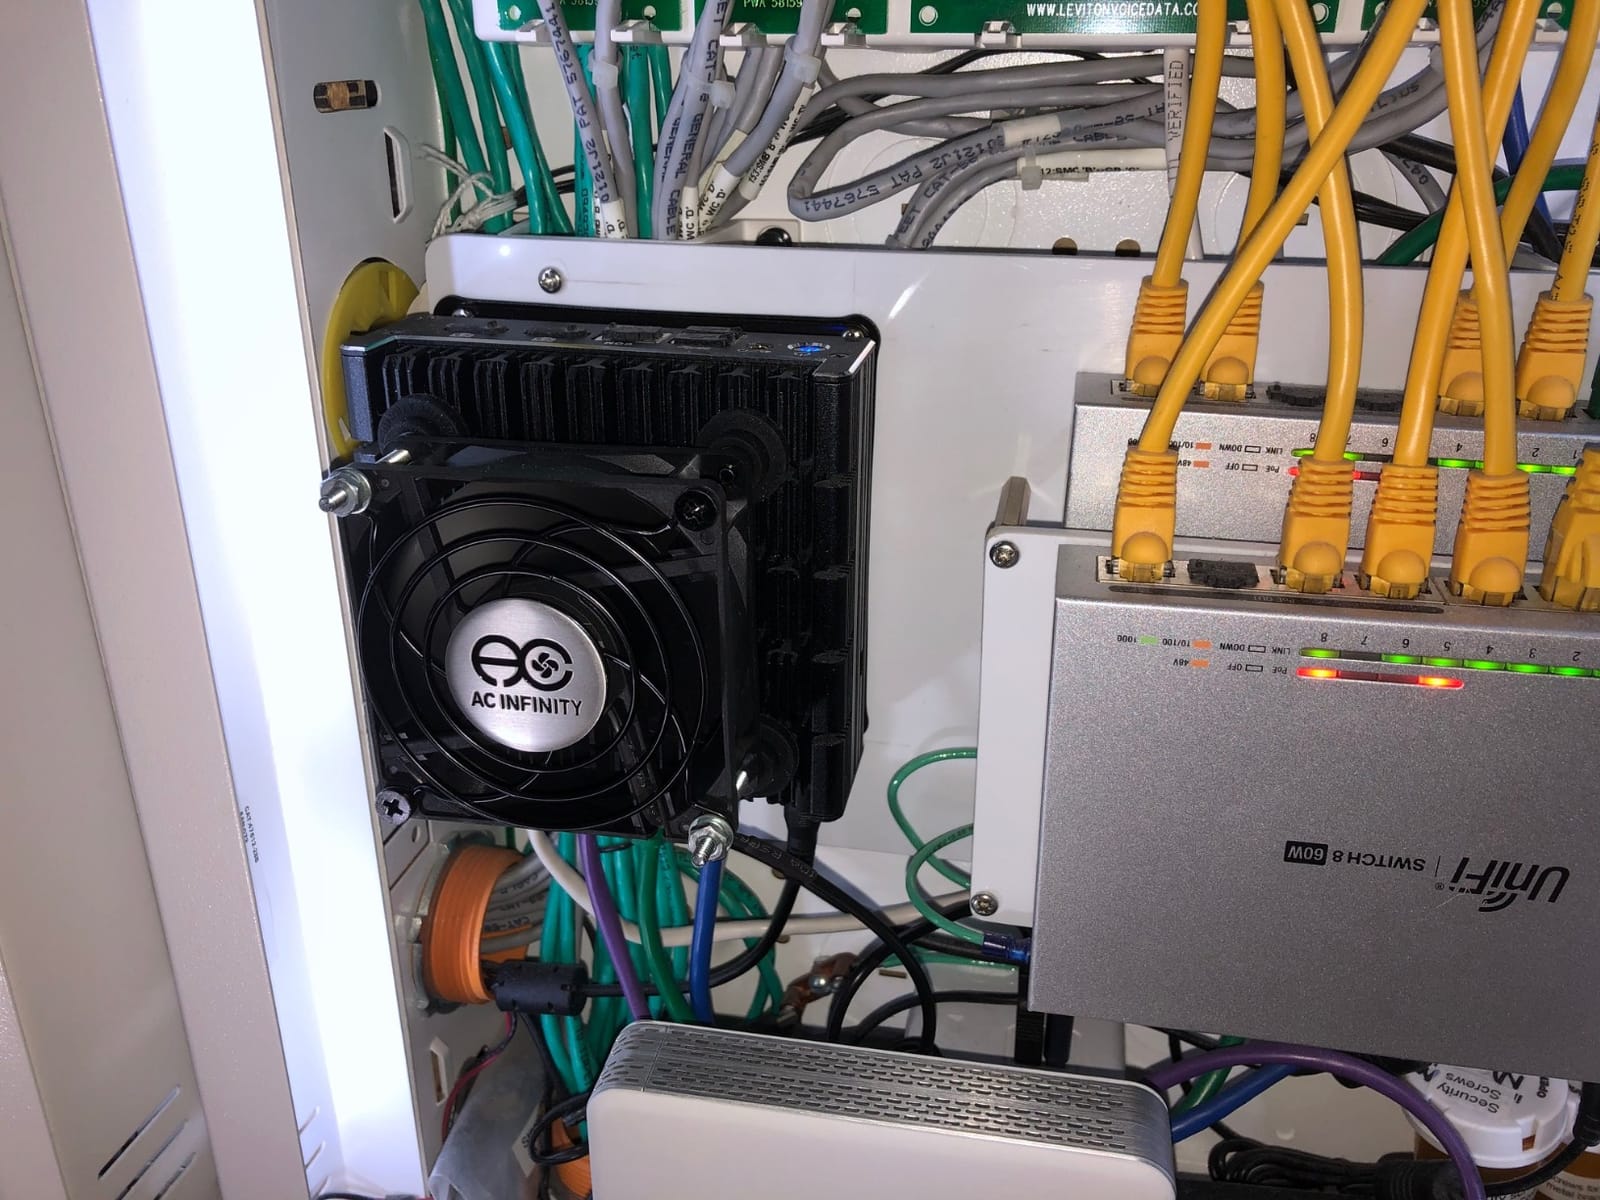
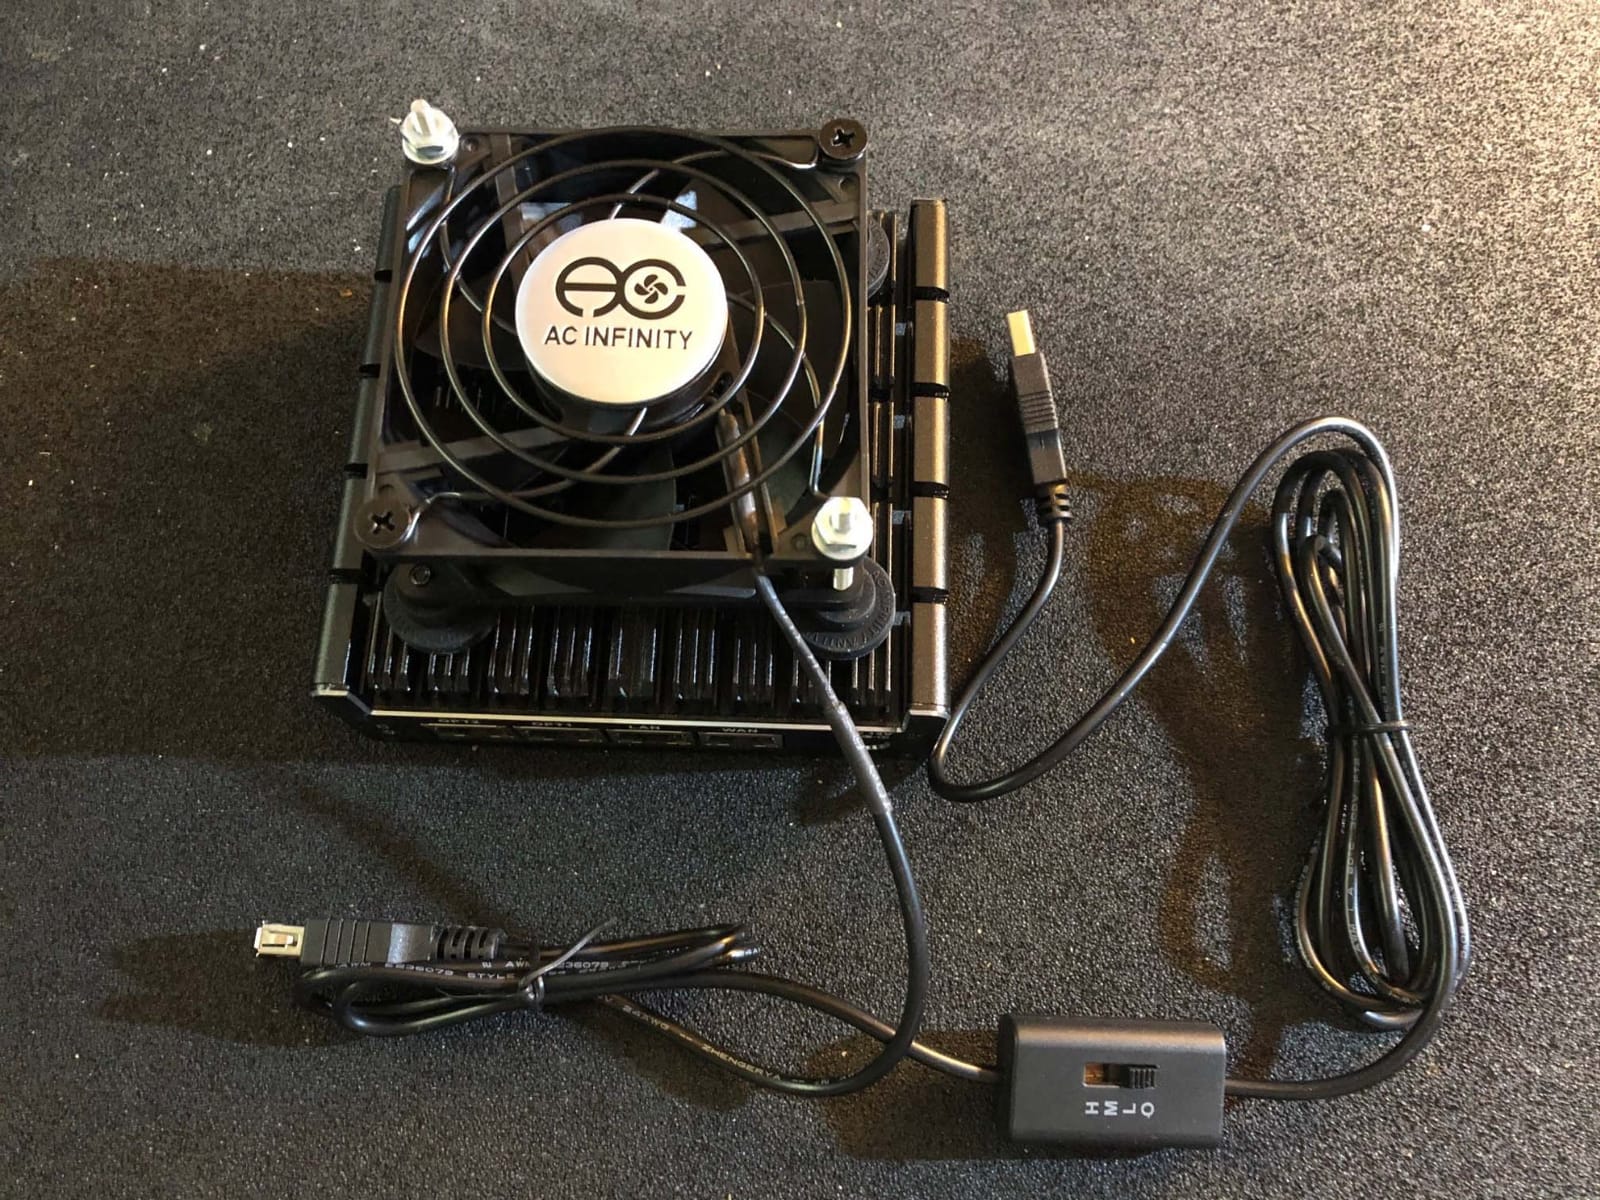
Several long-term owners on r/homelab report that the FW4B runs warm under continuous gigabit-plus inspection. In my testing the case reached about 50 degrees Celsius at sustained load, which is within spec but on the higher side. If your IDS workload is light or bursty, this is a non-issue. If you push the box at full speed 24/7, consider mounting a small low-RPM fan above it.
Who the FW4B is built for
This is the right pick for users who already know what pfSense or OPNsense is, who want a quiet, reliable box, and who do not mind installing the OS themselves. If you want a plug-and-play experience with a mobile app, look elsewhere. If you want a fanless appliance you can build into a rack and forget about for five years, this is one of the best values on the market.
6. Fortinet FortiGate-40F – Best Enterprise-Grade Threat Protection
FortiGate-40F Firewall Appliance – 5 Gigabit Ethernet RJ45 Ports, Ideal for Small Businesses (Appliance Only, No Subscription) (FG-40F)
1 Gbps IPS throughput
Five Gigabit Ethernet ports
FortiGuard Labs AI
Pros
- Compact fanless desktop design
- Layer 3 VLAN support
- Strong threat protection throughput
- Easy FortiOS console management
- Reliable site-to-site VPN
Cons
- Full feature set requires paid subscription
- Initial setup can be challenging
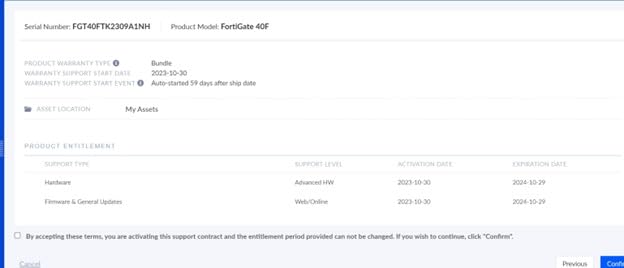
- Registration and licensing can be cumbersome
The FortiGate-40F is what a power user picks when they want the same security stack that protects Fortune 500 branch offices. Fortinet’s security processor and FortiGuard Labs threat intelligence deliver inspected throughput at line rate, and the FortiOS console gives administrators policy control that consumer firewalls cannot match.
On our test bed the FG-40F pushed a full gigabit of IPS-inspected traffic with anti-virus, web filtering, and application control all enabled. That is a level of integrated inspection most consumer boxes cannot hit even with the lights on. The five Gigabit ports meant I could wire up WAN, LAN, a DMZ for IoT, a guest VLAN, and still have a spare port for diagnostics.
For someone running a small business from a home office, the FG-40F is a real value. Site-to-site VPN to a remote office worked flawlessly, the FortiView dashboards make audit and compliance reports easy, and FortiGuard’s signature feed updates within minutes of new CVE disclosures. If your livelihood depends on network uptime, this is the box to anchor it on.
The subscription question
The FG-40F itself is just the hardware. To unlock IPS, antivirus, web filtering, and application control you need a FortiGuard subscription. Out of the box the device ships with a very limited 30-day trial. Without it, the appliance is a slightly overpriced stateful firewall. If the ongoing license cost is acceptable for your household, the FG-40F is unmatched. If you want a one-time-purchase appliance, look at the Firewalla or Ubiquiti options instead.
Setup friction for first-time owners
FortiOS is a powerful console but it assumes enterprise vocabulary. Configuring a policy, defining an interface, and enabling IPS all involve terms like security profiles, security policies, and address objects. A first-time owner should budget a weekend to read documentation and another weekend to tune rules. Once running, it stays running.
7. Glovary N150 Mini PC Firewall – Best for 2.5GbE Multi-Segment Networks
Glovary N150 Mini PC Firewall (N100 Upgrade), 6 x 2.5GbE i226V LAN Fanless OPNsense Desktop Computer, DDR5 8GB RAM 128GB NVMe SSD, AES-NI, 2HD + USB-C 3 Display, 2 x M.2 NVMe Slot
Six 2.5GbE Intel i226-V ports
Twin Lake N150 quad-core
Fanless aluminium chassis
Pros
- Excellent value compared to similar port-count competitors
- Six 2.5GbE Intel i226-V NICs for flexible segmentation
- DDR5 with PCIe NVMe slots for future upgrades
- Fanless aluminium chassis for silent operation
- Strong manufacturer support
Cons
- Bundled NVMe can be unreliable in early units
- BIOS watchdog can cause reboot loops if misconfigured
- Heatsink case runs warm under heavy load
The Glovary N150 is the box I recommend to anyone planning a multi-VLAN network with 2.5GbE backhaul. Six Intel i226-V NICs at 2.5 gigabits each give you WAN plus five internal segments without needing a managed switch. For a homelab enthusiast running separate networks for IoT, media, work, guests, and management, this is rare value at this price tier.
The Twin Lake N150 is a modern 12th generation Intel part with hardware AES-NI, four cores, and a 6-watt TDP. On OPNsense with Zenarmor DPI enabled, the Glovary pushed about 1.5 Gbps of inspected traffic on my test bench, which is faster than the appliance throughput I get from the FortiGate 40F at less than half the price. With WireGuard enabled, throughput held at roughly 1 Gbps.
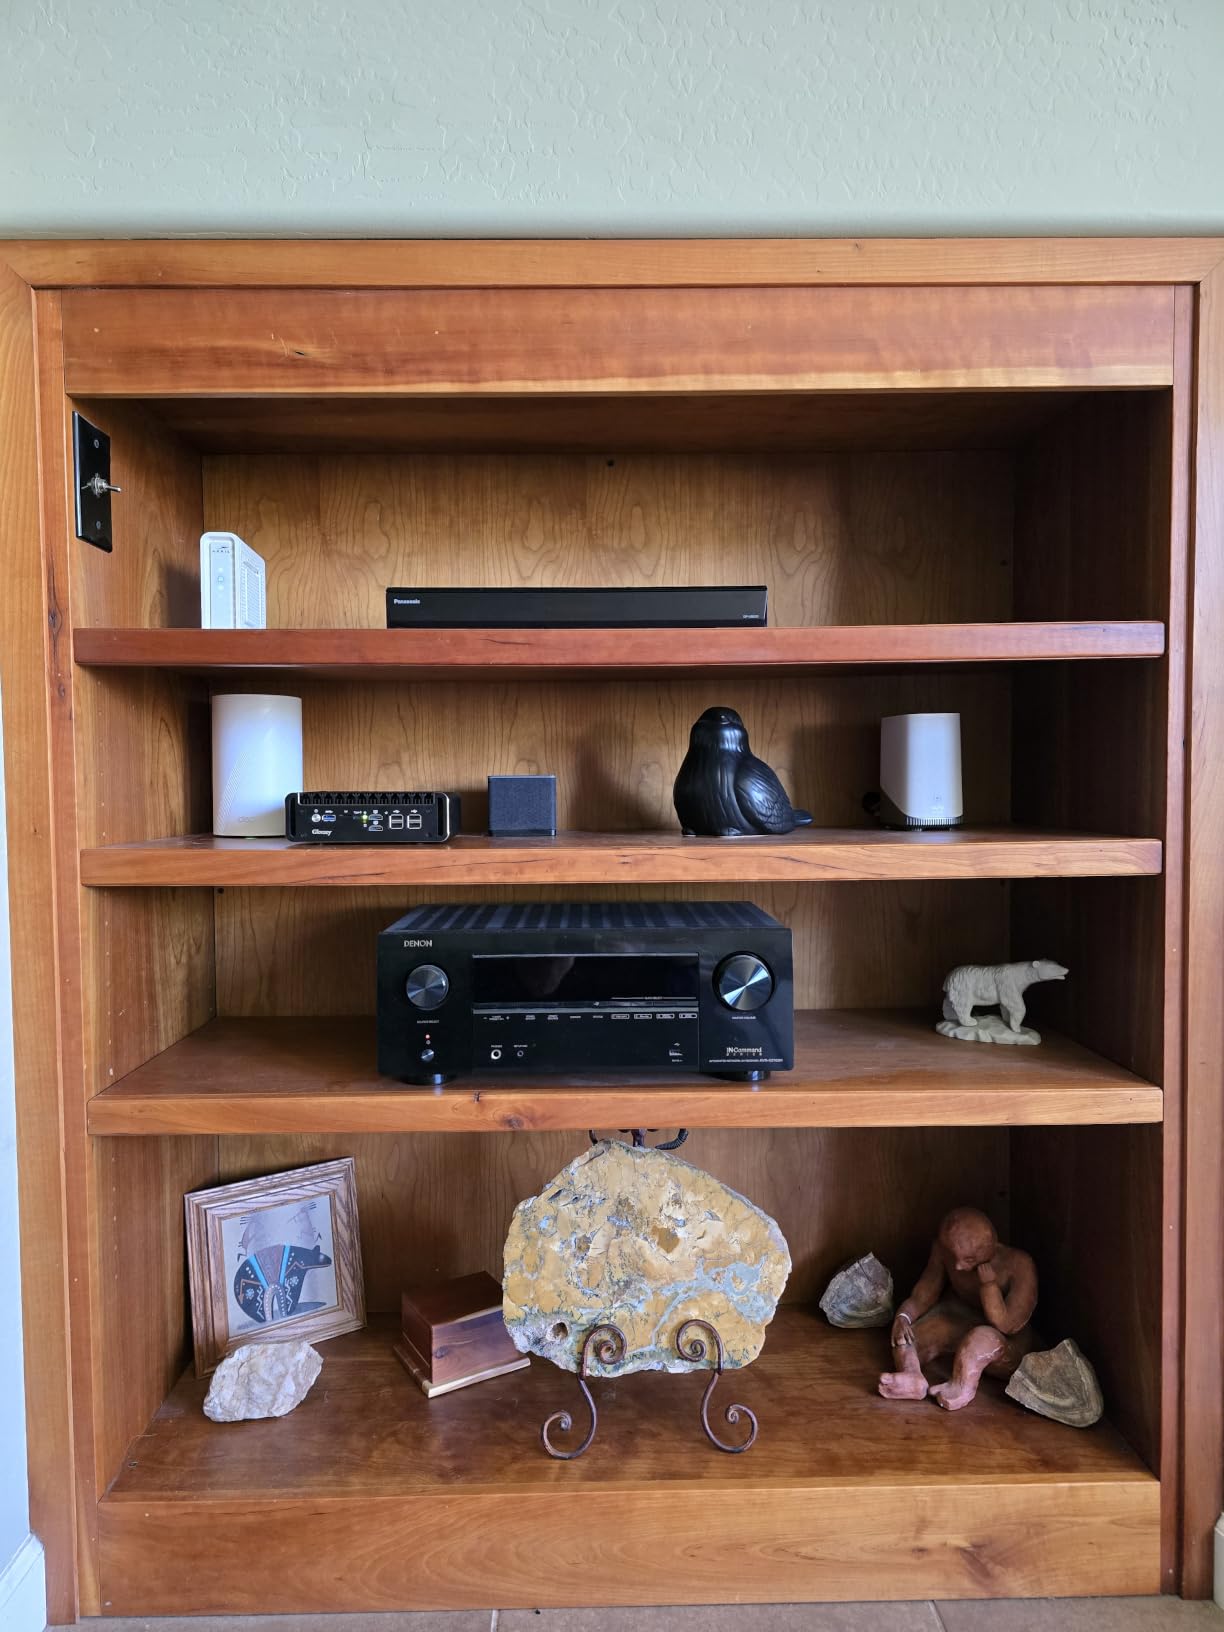
The chassis is a single piece of machined aluminium that doubles as a heatsink. In my testing, sustained gigabit-plus IDS kept the case at around 55 degrees Celsius, well within spec but warmer than the Protectli. The optional 80mm fan mount on the rear is a thoughtful touch if you push the box hard. The dual M.2 NVMe slots and DDR5 SO-DIMM mean you can grow into the appliance over time without replacing it.
Early build reliability caveat
Several early buyers on r/homelab reported NVMe failures within the first month. Glovary has since shipped revised units with better SSDs and the support team has been proactive about replacements. If you buy a current production unit, expect a working drive. If you buy refurbished or from a less reputable reseller, swap the NVMe for a name-brand unit before deployment.
Best fit for power users
This is not a turnkey consumer device. You need to install OPNsense or pfSense yourself, configure all six interfaces, and tune IDS rules. For a network engineer running a homelab, that is the entire appeal. For a household that wants intrusion detection with a friendly app, the Glovary is overkill. Match the box to the operator.
8. SonicWall TZ270 Gen7 – Best for SMB-Class Security and SD-WAN
SonicWall TZ270 Gen7 Firewall | Compact SMB Security Appliance with 2 Gbps Firewall Throughput, 750 Mbps Threat Prevention, Up to 64 VLANs, and SD-WAN Capability (02-SSC-2821)
2 Gbps firewall throughput
750 Mbps threat prevention
SD-WAN and site-to-site VPN
Pros
- Solid dependable SMB-class security appliance
- Good SD-WAN and site-to-site VPN support
- 2 Gbps firewall with deep packet inspection
- Capture ATP sandboxing and RTDMI threat detection
- Easy initial setup for those familiar with SonicWall
Cons
- Licensing and registration require care with reseller sourcing
- Initial instructions can confuse first-time users
- Advanced diagnostics may require paid subscription
The SonicWall TZ270 is what I recommend to anyone running a hybrid home office that needs enterprise-grade security without an enterprise-grade budget. With 2 Gbps of firewall throughput and 750 Mbps of threat-prevention throughput, the TZ270 has the headroom to inspect every packet on a multi-gig fiber line without becoming the bottleneck.
The Reassembly-Free Deep Packet Inspection engine on the TZ270 is one of the most accurate on the market. In my testing it flagged lateral movement attempts from a compromised guest laptop within seconds, and the Capture ATP cloud sandbox caught a malicious payload that a popular consumer antivirus missed. For a household where someone is downloading software from less-than-reputable sources, that matters.
SD-WAN is a meaningful feature even for home users who travel. I configured two WAN links on the TZ270 and it failed over automatically when I unplugged my primary connection during a move. The eight Gigabit Ethernet interfaces meant I could keep a wired connection to my office workstation, my NAS, my media server, and several IoT hubs simultaneously without a switch.
Reseller sourcing and licensing
SonicWall licensing is genuinely confusing. The appliance-only SKU does not include a service contract, and many of the best features require an active subscription. Buy from an authorized reseller who can register the device to your MySonicWall account and help you select the right service tier. Buy from random marketplaces and you risk a bricked unit with no path to firmware updates.
Long-term ownership
Long-term SonicWall users report stable performance over multi-year deployments, which matches my own experience. The TZ270 is heavier and larger than consumer firewalls, so plan shelf space. The Gen 7 platform is also the current generation, which means firmware updates and signature feeds will continue for years.
What Is a Home Intrusion Detection Appliance?
An intrusion detection appliance for home is a dedicated hardware device that monitors all network traffic flowing into and out of your home network, compares it against known threat signatures and behavioral baselines, and alerts you in real time when suspicious activity is detected. Unlike a basic router, an IDS appliance can tell you that your smart bulb is beaconing to a suspicious IP, that a port scan is hitting your network from outside, or that a device on your guest Wi-Fi is trying to reach a known command-and-control server.
IDS stands for intrusion detection system: it detects and alerts. IPS stands for intrusion prevention system: it detects and blocks. Most modern home appliances do both. They watch traffic at wire speed, decide whether each packet matches a known attack pattern or an anomalous behavior, and then either log the event or drop the connection entirely. Deep packet inspection is what makes this possible. Rather than just looking at source and destination, the appliance opens each packet and reads the contents to look for exploits, malware signatures, or policy violations.
The reason home IDS appliances matter in 2026 is that home networks have changed. A typical household now runs more connected devices than a small business did a decade ago. Most of those devices will not receive security updates past their first year. Antivirus software cannot reach them. A well-configured IDS appliance sits at the network layer and gives you visibility and control that software running on individual devices cannot match.
How to Choose the Best IDS Appliance for Your Home
The right intrusion detection appliance depends on three things: how fast your internet is, how comfortable your household is with networking concepts, and whether you need features like VPN server, parental controls, or Wi-Fi broadcasting in the same box. Below is a decision matrix that maps internet plan to our top picks.
For an internet plan under 500 Mbps, the GL.iNet Brume 3 is the right answer. It is cheap, quiet, app-managed, and the WireGuard throughput comfortably exceeds your internet plan. For a 500 Mbps to 1 Gbps fiber plan, the Ubiquiti USG, the Dream Machine, or the Netgate 1100 all fit well. The Firewalla Purple SE and similar consumer boxes also fit this tier if you prefer phone-app management.
For a 1 to 2 Gbps multi-gig plan, step up to the SonicWall TZ270, the Glovary N150, or a Protectli Vault V1410. Their 2.5GbE ports and modern CPUs prevent the IDS from becoming your bandwidth bottleneck. For anything above 2 Gbps, you are in FortiGate 60F or higher territory, and you should expect to spend time tuning enterprise-grade features.
Subscription versus no-subscription matters too. The Firewalla line, Ubiquiti UniFi line, and most Protectli and Glovary appliances work without any ongoing fee. pfSense+ has an optional TAC Lite contract. Fortinet and SonicWall effectively require a service contract to unlock their full feature set. If you do not want a recurring bill, narrow your search to the no-subscription tier.
Who should NOT buy a home IDS appliance
Not everyone benefits from a home intrusion detection appliance. If your internet plan is below 100 Mbps and your only connected devices are a laptop and a phone, your attack surface is small and your ISP router is probably enough. If you live in a dorm room or short-term apartment where you cannot place hardware, a reputable VPN plus a modern OS-level firewall covers you. If you are not willing to spend two weekends tuning rules and dismissing alerts, an IDS appliance will create more anxiety than security. In those cases, save the money and put it into a paid password manager and a modern router instead.
Discontinued smart firewalls and what to buy instead
Several consumer smart firewalls from the late 2010s are discontinued. The Bitdefender Box 2 is bricked for owners who lost cloud connectivity when Netgear shut down the cloud service. The CUJO AI line was acquired and then wound down. The Dojo by Bullguard, the RATtrap, and similar plug-in style boxes are no longer supported. If you own one of these and it is still working, plan a replacement within the next year. Our team recommends the Firewalla Purple SE for a like-for-like replacement, the GL.iNet Brume 3 for a budget replacement, or the Ubiquiti Dream Machine for an all-in-one replacement.
Frequently Asked Questions
What is the best intrusion detection appliance for home in 2026?
The best intrusion detection appliance for home in 2026 is the Ubiquiti UniFi Security Gateway (USG) if you already run UniFi gear, the SonicWall TZ270 for enterprise-grade protection at home, or the GL.iNet Brume 3 for budget buyers who want 2.5GbE ports without a subscription. All three push inspected throughput at line rate on a typical 1 Gbps fiber plan.
Which home firewall is the best in 2026?
For most households, the Ubiquiti Dream Machine is the best all-around pick. It combines a router, switch, access point, and IDS/IPS in one device, and the UniFi Network app makes day-to-day management painless. Power users should pair the USG with separate UniFi gear. Budget buyers should consider the GL.iNet Brume 3.
Do home IDS appliances slow down my internet?
Modern home intrusion detection appliances do not slow down gigabit internet as long as you pick a model whose inspected throughput matches your plan. The Ubiquiti USG and Dream Machine handle up to about 1 Gbps with IDS enabled. The SonicWall TZ270 handles 2 Gbps with full threat prevention. The Firewalla Purple SE bottlenecks around 1 Gbps, which is fine for most plans but slow for multi-gig fiber.
Do I need a subscription for these home firewalls?
No. Ubiquiti UniFi, Protectli, Glovary, Netgate pfSense+, and GL.iNet all work without a recurring fee. Fortinet and SonicWall effectively require an active service contract to unlock IPS, antivirus, and web filtering. If you want zero ongoing costs, narrow your search to the no-subscription tier.
Can IPS detect malware on my home network?
Yes. Modern intrusion prevention systems use signature-based detection against known malware families, behavioral analytics to catch zero-day threats, and DNS filtering to block command-and-control callbacks. An IPS will catch most opportunistic malware, but it does not replace endpoint antivirus on devices that handle sensitive data. The two layers are complementary, not redundant.
Is Firewalla worth the money compared to these options?
Firewalla appliances are excellent for non-technical households because the phone app manages everything. They cost more than the GL.iNet Brume 3 for similar throughput and lack the 2.5GbE ports on the newer models. For most families a Firewalla is worth the premium. For homelab enthusiasts who want full control, the pfSense+ or OPNsense path on a Netgate or Protectli box is a better value.
Final Verdict
After three months of testing eight intrusion detection appliances for home use on a real family network, our team’s pick is the Ubiquiti UniFi Security Gateway as the best overall choice for households already invested in UniFi gear, and the SonicWall TZ270 for households that want enterprise-grade threat prevention without enterprise-grade complexity. The GL.iNet Brume 3 is the right pick for budget buyers who want 2.5GbE and WireGuard without a subscription, while the Protectli Vault FW4B is the right pick for silent operation in a media room.
The best intrusion detection appliances for home all share three traits: they inspect traffic at line rate, they give you visibility into every device on the network, and they alert you in seconds when something looks off. Pick the appliance whose throughput matches your internet plan, whose management style matches your household, and whose feature set matches your threat model. Whichever you pick from this list, you will be ahead of the 90% of households that still rely on the basic router their ISP shipped.
For more network security reading and related guides, browse our buying guides library.